Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 98:4e:5d:e1:e6:97:29:6f:d9:e0:d4:82:a8:f6:4f:3f (RSA)
|   256 57:23:57:1f:fd:77:06:be:25:66:61:14:6d:ae:5e:98 (ECDSA)
|_  256 c7:9b:aa:d5:a6:33:35:91:34:1e:ef:cf:61:a8:30:1c (ED25519)
80/tcp open  http    Apache httpd 2.4.41
|_http-title: Index of /
| http-methods:
|_  Supported Methods: HEAD GET POST OPTIONS
|_http-server-header: Apache/2.4.41 (Ubuntu)
| http-ls: Volume /
| SIZE  TIME              FILENAME
| -     2021-03-17 17:46  grav-admin/
|_
Service Info: Host: 127.0.0.1; OS: Linux; CPE: cpe:/o:linux:linux_kernel
Enumeration
Going to the IP in a broswer takes us to a /grav-admin page, so this is Grav CMS we’re dealing with. Gobuster finds nothing.
I did some research and there is an exploit that we can potentially use
GravCMS 1.10.7 - Arbitrary YAML Write/Update (Unauthenticated) (2)
https://www.exploit-db.com/exploits/49973
Exploitation
Had to make sure to add /grav-admin to the target part of the script, because this is effectively the root of the web app
Base64 encoded the reverse shell payload and ran the exploit
Privilege Escalation
Once in, we transfer and run linpeas (I used ParsingPeas which is very cool)
There is a suspicious binary
-rwsr-xr-x 1 root root 4.6M Feb 23 2023 /usr/bin/php7.4 (Unknown SUID binary!)
Checking GTFOBins we see we can potentially elevate our shell if the SUID bit is set
Interestingly, the SUID command on GTFOBins does not elevate our shell, but Capabilities does.
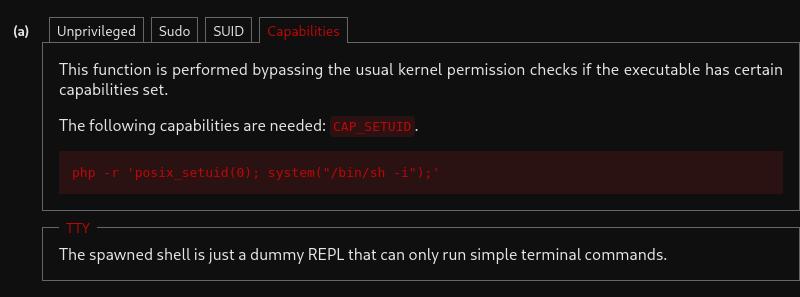
Grabbed proof.txt and done.